Me watching the production server after running a command ChatGPT said was safe. 💀

Website: https://darkwebinformer.com/
Website Pricing (Crypto friendly): https://darkwebinformer.com/pricing
Socials: https://darkwebinformer.com/socials
API Access: https://darkwebinformer.com/api-details
X: https://x.com/DarkWebInformer
Telegram: https://t.me/SliceForLifeee
No longer posting on this platform. The only platforms I am posting on are X and Telegram.
Updated: 2026-11-22
Me watching the production server after running a command ChatGPT said was safe. 💀
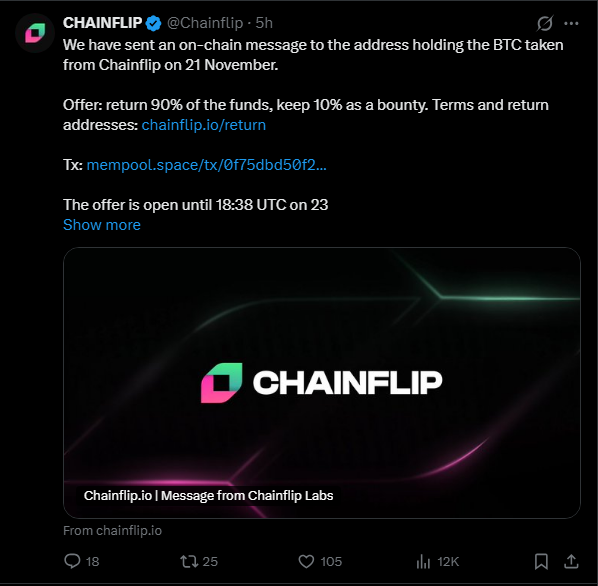
🚨🇫🇷 SOS Oxygène patient database allegedly leaked, approximately 15,000 records exposed
Threat actor "morphyn1337", associated with LunarisSec, claims to have released patient data from SOS Oxygène, a French provider of home oxygen therapy and respiratory care services.
The dataset reportedly contains:
• Patient names and contact information • Residential addresses and phone numbers • Patient identification and healthcare records • Medical service and delivery-related information
The actor previously advertised the dataset for sale and has now published an approximately 19.8 MB JSON file containing the alleged patient records.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
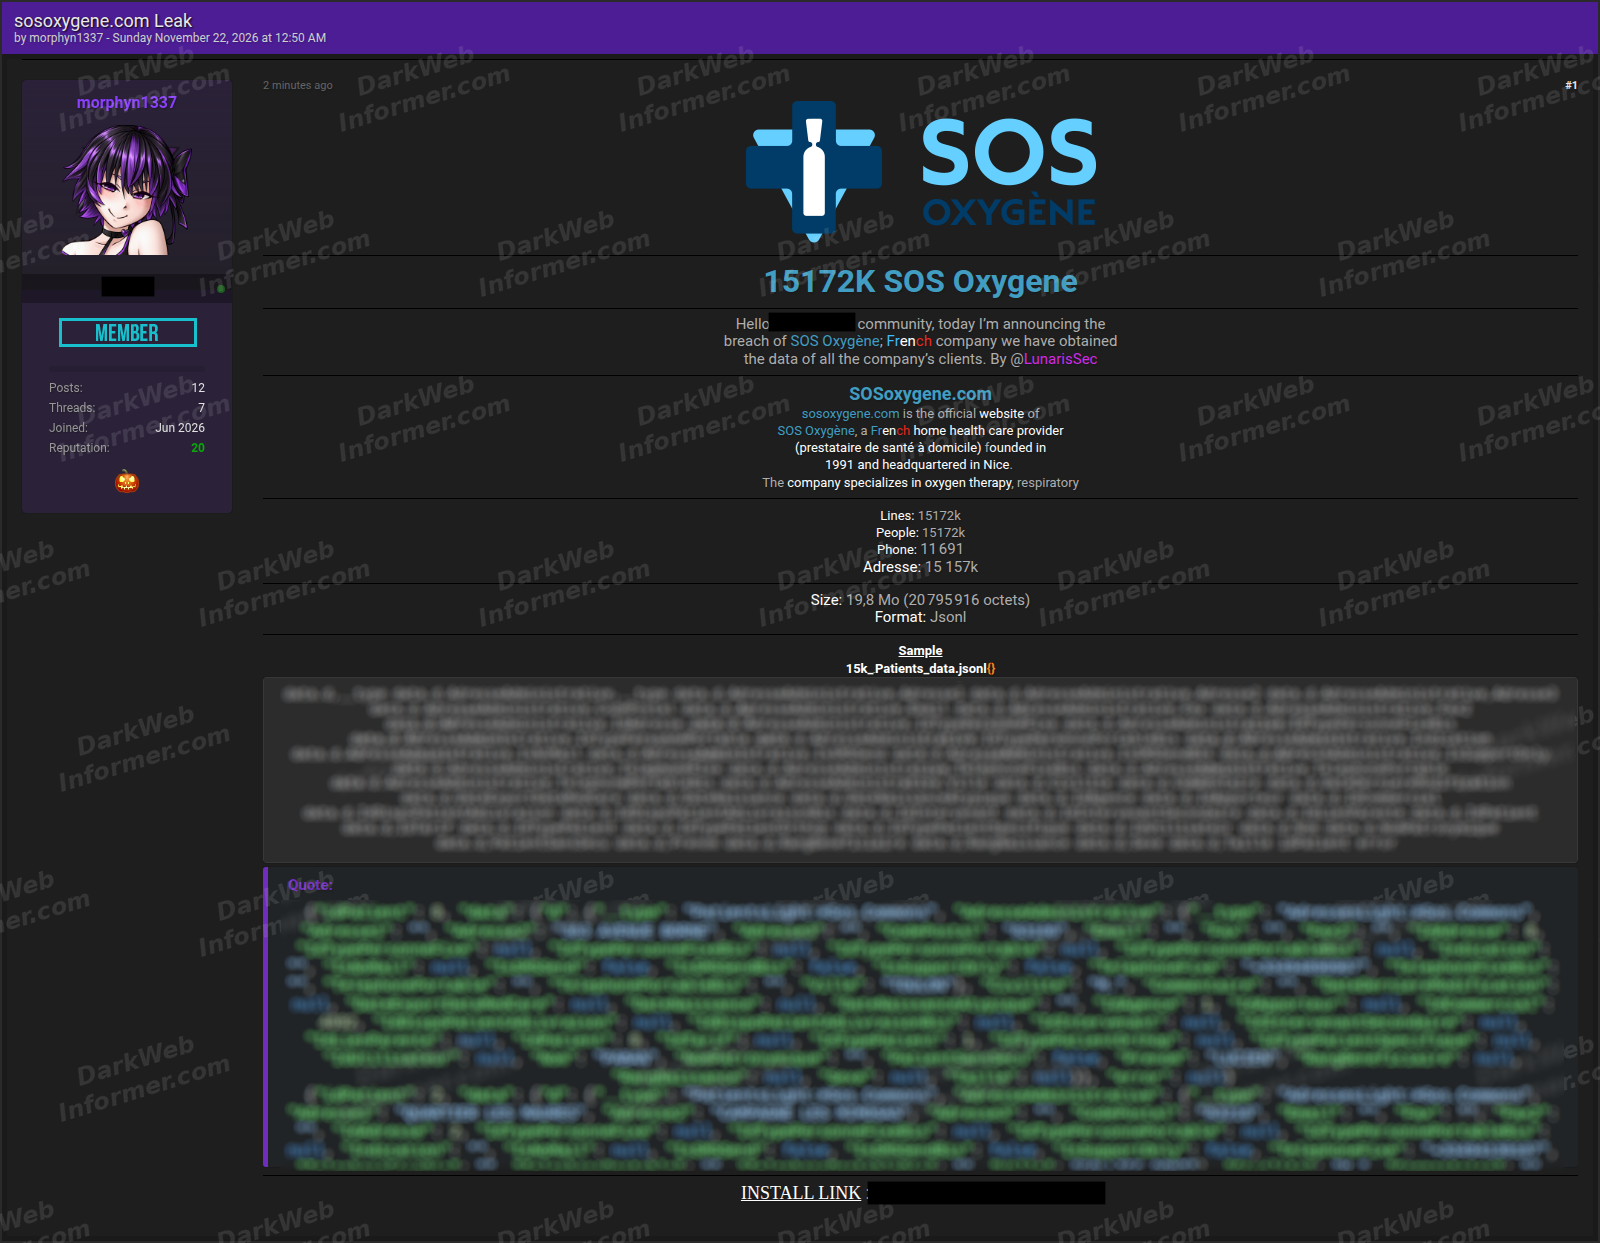
🚨 Chainflip's FLIP token plunges over 30% after a suspected $4.86 million vault theft, as the protocol offers the attacker a 10% bounty to return the stolen funds.
Blockchain investigators identified a suspicious transaction that drained 520.22 ETH, approximately 3.25 million USDC, and 758,000 USDT from Chainflip's Ethereum vault. The protocol says an additional 122.86 BTC was also taken.
The withdrawal carried a valid cryptographic signature, raising suspicions of a compromised validator key. Much of the stolen Ethereum-side funds was subsequently moved through Tornado Cash.
Chainflip has activated full safe mode, suspending swaps and withdrawals while investigating the incident.
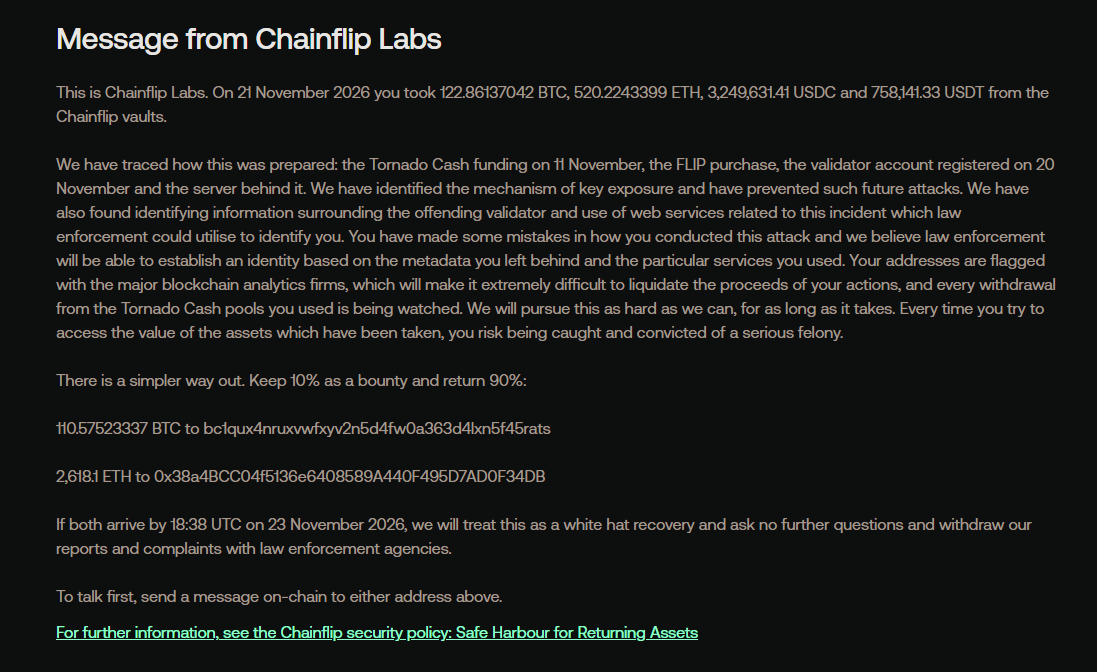
The company has now sent an on-chain message offering the attacker a deal: return 90% of the stolen funds and keep 10% as a bounty before 18:38 UTC on November 23.
Chainflip claims it has traced the attack's preparation, identified evidence of key exposure, and gathered information that could help law enforcement identify the attacker. It says it will withdraw its complaints if the funds are returned before the deadline.
Sources:
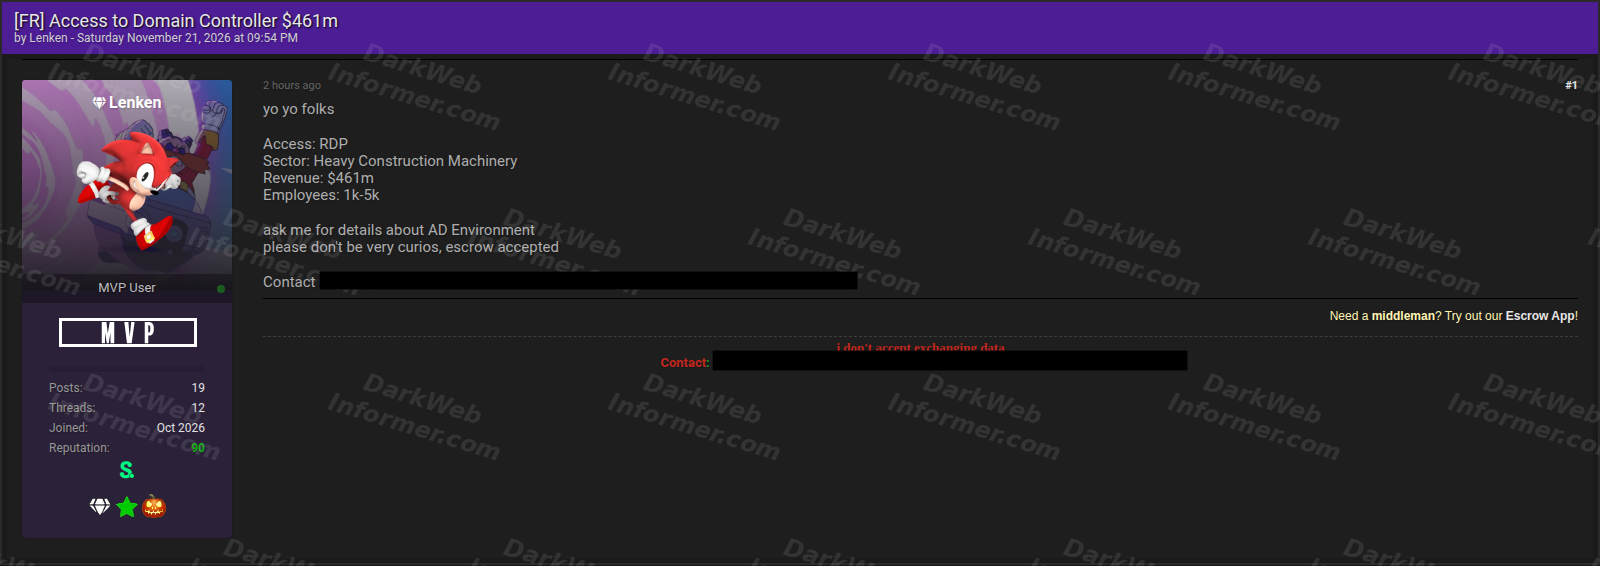
🚨🇫🇷 Initial Access: French Heavy Construction Machinery Company
A threat actor is advertising RDP access to an unnamed French heavy construction machinery company reportedly generating $461M in revenue and employing between 1,000 and 5,000 people.
The listing is titled as access to a Domain Controller, with additional details about the Active Directory environment available privately. Escrow is accepted.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
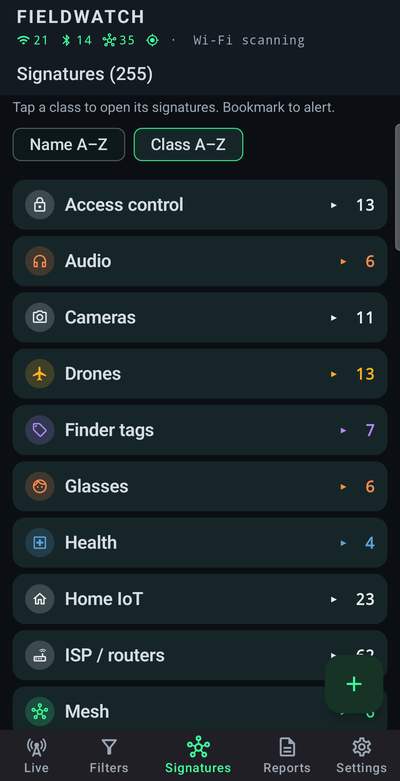
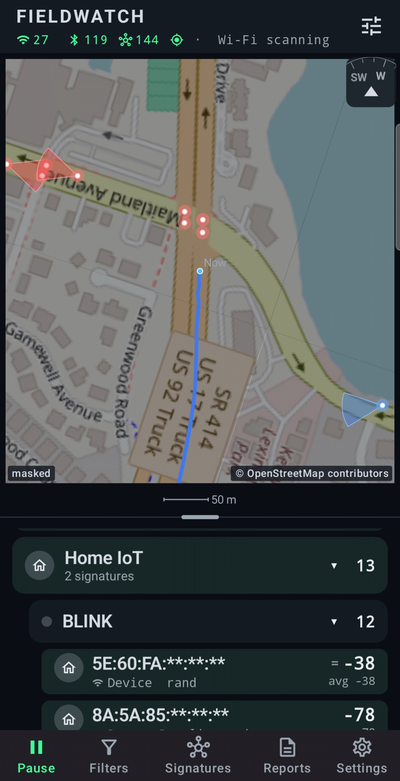
Fieldwatch: a receive-only Android app for passively observing nearby Wi-Fi access points and Bluetooth LE devices
GitHub: https://github.com/OffGridPete/Fieldwatch
Fieldwatch runs entirely on-device with no account, backend server, or external radio hardware required. It listens for Wi-Fi and BLE broadcasts, identifies known device signatures, and lets users filter, tag, and document what their phone detects nearby.
Fieldwatch | Passive Wi-Fi & BLE Monitoring:
• Wi-Fi access point and Bluetooth LE discovery • Extensible device signature library • Filtering and custom views • GPS tagging and movement/co-travel analysis • Reporting and AI export • Fully offline operation • No ads, account, or backend server • Android 10+ support
The project is aimed at field observation, RF awareness, research, and documenting nearby wireless devices using only the phone’s built-in radios.
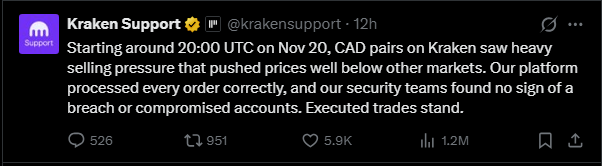
🚨🇨🇦 Bitcoin crashes 71% to just C$24,250 on Kraken, and the exchange says all trades will stand.
Heavy selling began around 20:00 UTC on November 20, sending Kraken's Canadian-dollar trading pairs into a massive price collapse. Bitcoin briefly traded for approximately US$16,900 while global prices remained near US$57,800.
Other cryptocurrencies, including Ethereum and stablecoins USDT and USDC, experienced similar crashes against the Canadian dollar. Some traders reported successfully purchasing discounted Bitcoin and withdrawing it before prices recovered.
Kraken confirmed that its systems processed all orders correctly and found no evidence of a security breach or compromised accounts. The exchange says every completed trade will remain valid.
By November 21, Bitcoin had recovered to approximately C$82,000, leaving some traders with potentially significant gains and others facing substantial losses.
Source: https://cryptoslate.com/kraken-says-trades-stand-after-bitcoin-sold-at-24250-canadian/
🚨🇺🇸 Microsoft confirms hackers exploited a vulnerability in Entra Connect Health to steal customer tenant information.
The security flaw was introduced on July 23 and remained undetected until November 9, allowing unauthorized parties to access administrator email addresses, tenant IDs, domain names, license information, and directory synchronization details.
Microsoft confirmed that attackers exploited the vulnerability but found no evidence of unauthorized configuration changes. Passwords, authentication tokens, and valid cryptographic keys were not exposed.
The company deployed a server-side fix on November 19 and began notifying affected organizations. The number of compromised tenants remains unknown, and Microsoft warns that the exposed information could be used in targeted phishing and social engineering attacks.
A couple of threat feed changes:
Monitored forums: 33
🚨🇺🇸 GoFundMe confirms hackers breached its fundraising platform and accessed customers' personal information.
According to a security notice, attackers gained unauthorized access to the GoFundMe Pro API during two separate periods, October 10–18 and November 8–9, 2026.
The compromised information includes names, postal addresses, phone numbers, and, in some cases, dates of birth and additional details submitted through registration forms.
GoFundMe says donor login credentials, full payment card numbers, security codes, and bank account details were not accessed. The company has disabled unauthorized accounts, secured the affected platform, and notified law enforcement.
The investigation remains ongoing, and the total number of affected individuals has not been disclosed.
Source: https://statusstack.com/service/classy/incidents/01a1fb2b-00a9-7357-8717-0fc880587a0f
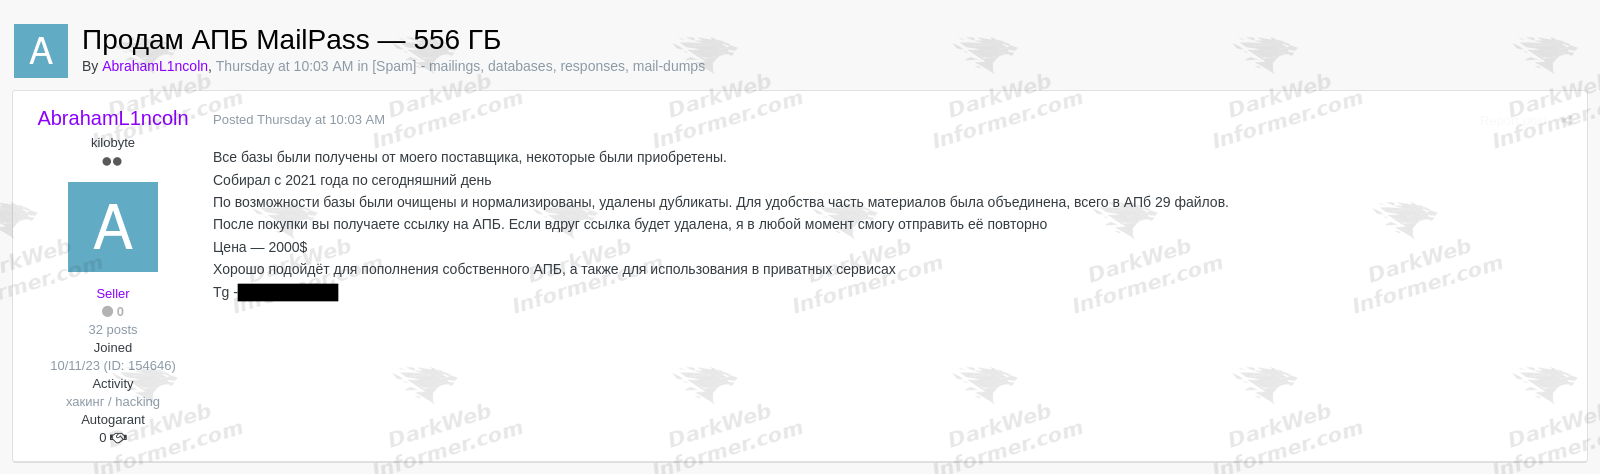
🚨 A 556 GB collection of email and password datasets is being offered for $2,000
An actor known as "AbrahamL1ncoln" is selling a MailPass dataset collection reportedly assembled from multiple sources between 2021 and November 2026.
The advertised collection includes:
• 556 GB of data across 29 files • Email and password datasets • Datasets reportedly cleaned and normalized • Duplicate records removed • Data obtained from suppliers and previous purchases
The seller is offering the collection for $2,000, with download access and replacement links if needed.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
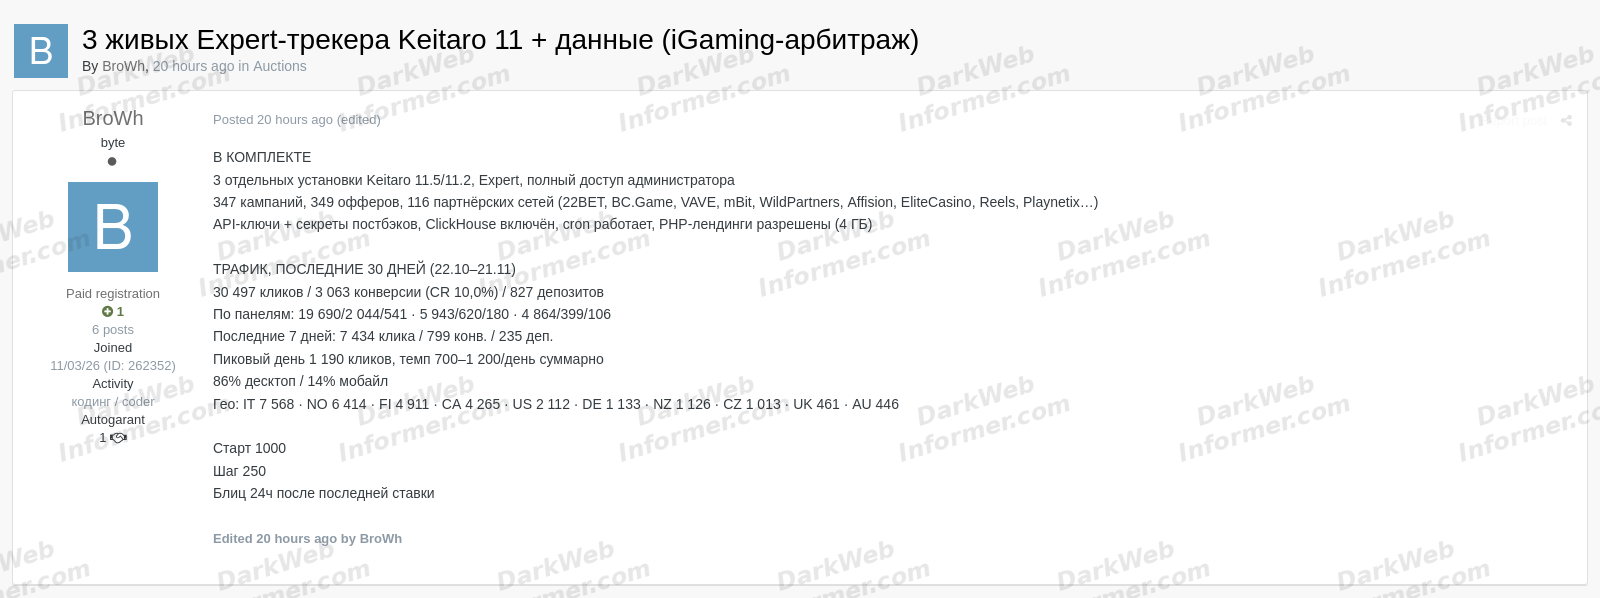
🚨 Three active Keitaro 11 iGaming traffic trackers with full administrator access offered for sale
An actor known as "BroWh" is auctioning three live Keitaro Expert installations used for gambling affiliate marketing, along with associated credentials, configurations, and campaign data.
The advertised package includes:
• 347 campaigns and 349 offers • 116 affiliate networks, including 22BET, BC.Game, and VAVE • API keys, postback secrets, and ClickHouse credentials • Cron jobs and 4 GB of PHP landing pages • Full administrator access to all three installations
The seller reports 30,497 clicks, 3,063 conversions, and 827 deposits over the past 30 days, with traffic primarily originating from Italy, Norway, Finland, and Canada.
Bidding starts at 1,000, with increments of 250.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
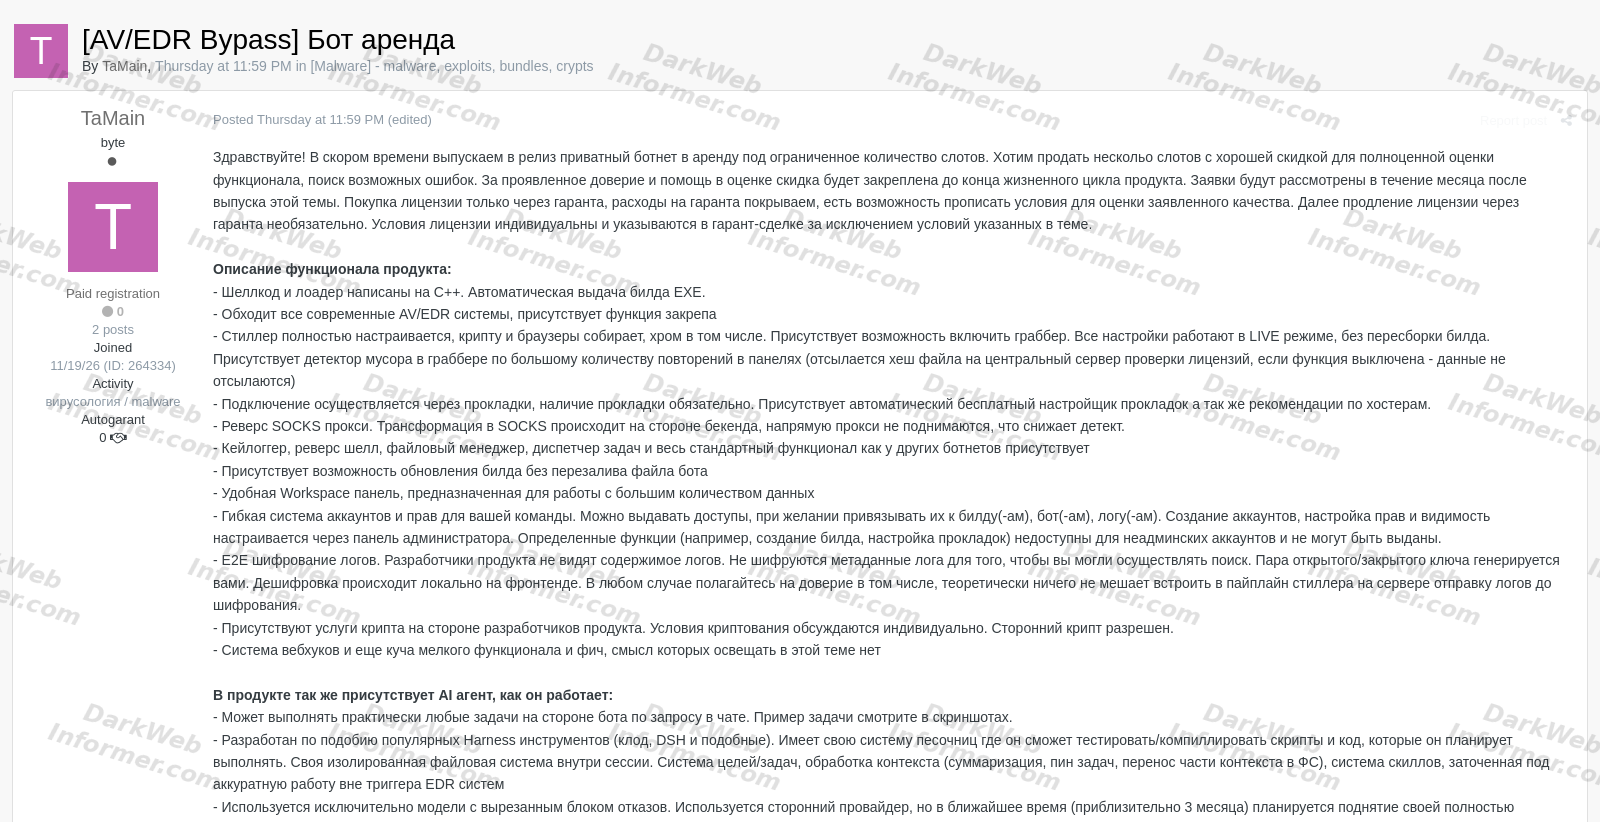
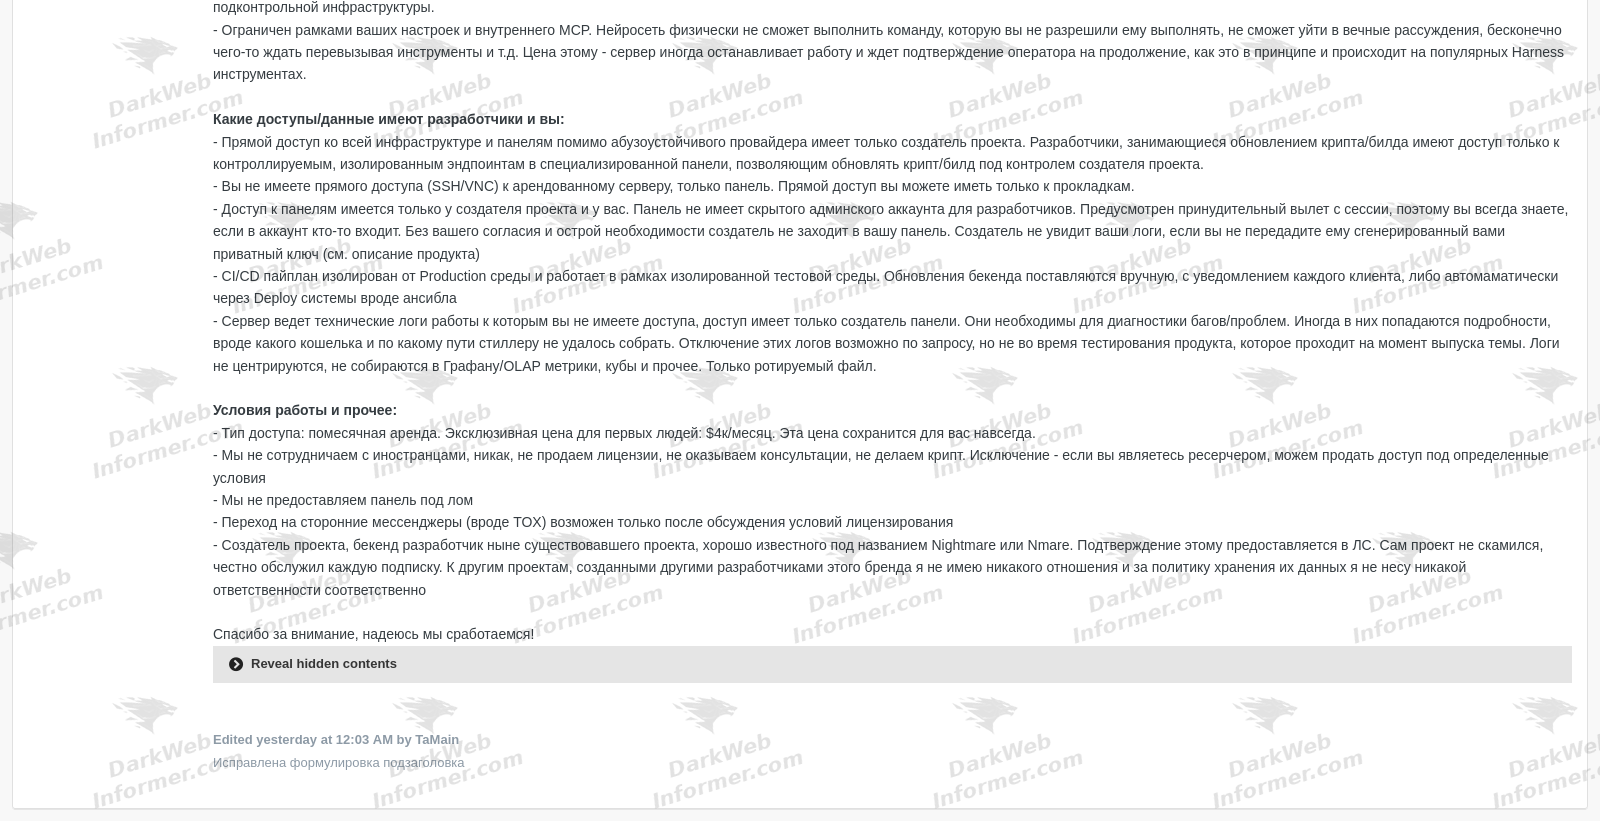
🚨 New AI-powered botnet advertised with AV/EDR bypass capabilities, priced at $4,000 per month
An actor known as "TaMain" is preparing to launch a private botnet rental service featuring malware deployment, credential theft, and an integrated AI agent designed to automate operations on infected systems.
Advertised capabilities:
• C++ shellcode loader with automatic EXE generation • Claimed bypass of modern AV/EDR solutions • Configurable infostealer targeting browsers and cryptocurrency wallets • Keylogging, reverse shell, and file management • Reverse SOCKS proxy support • Remote payload updates without reinstalling • AI agent capable of generating, testing, and executing scripts • Encrypted logs and multi-user management panel
The operator is offering limited early-access licenses at $4,000 per month, with discounted slots available before the official launch.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
Pushed a fix to the threat feed to ensure translation of text is always in English. Will adjust as needed. Monitoring.
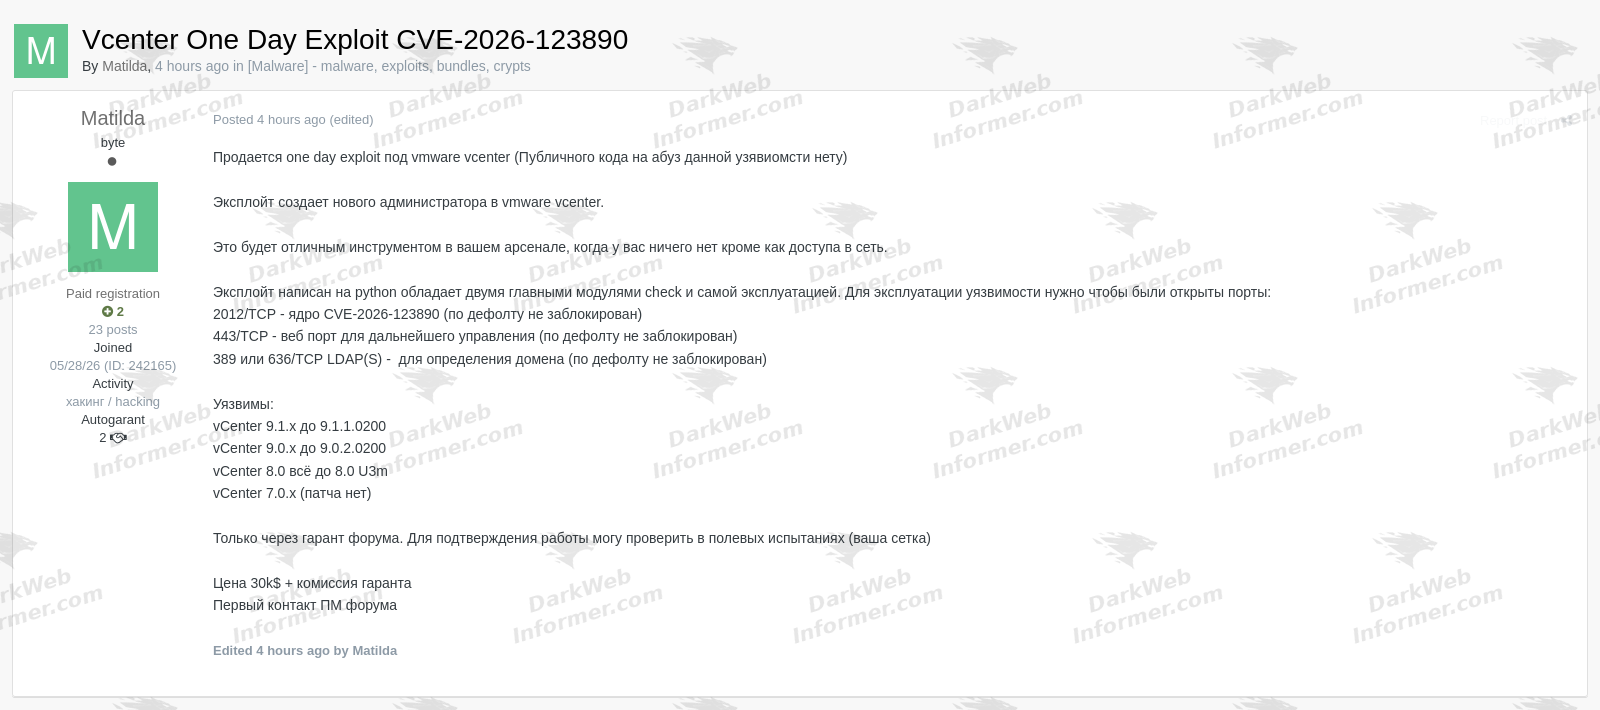
🚨 VMware vCenter exploit for critical authentication bypass vulnerability offered for $30,000; CVE-2026-123890
An actor known as "Matilda" is selling a Python-based exploit for VMware vCenter, claiming it can create a new administrator account through the recently disclosed vulnerability.
The seller claims the exploit includes:
• Two modules for vulnerability checking and exploitation • Support for vCenter versions 7.0 through 9.1 • Administrator account creation • Successful testing against live environments • Demonstrations available to prospective buyers
CVE-2026-123890 carries a critical CVSS score of 9.8. Broadcom disclosed the vulnerability on November 19 and released security updates. Exploitation in the wild has also been reported.
The seller's exploit claims remain unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
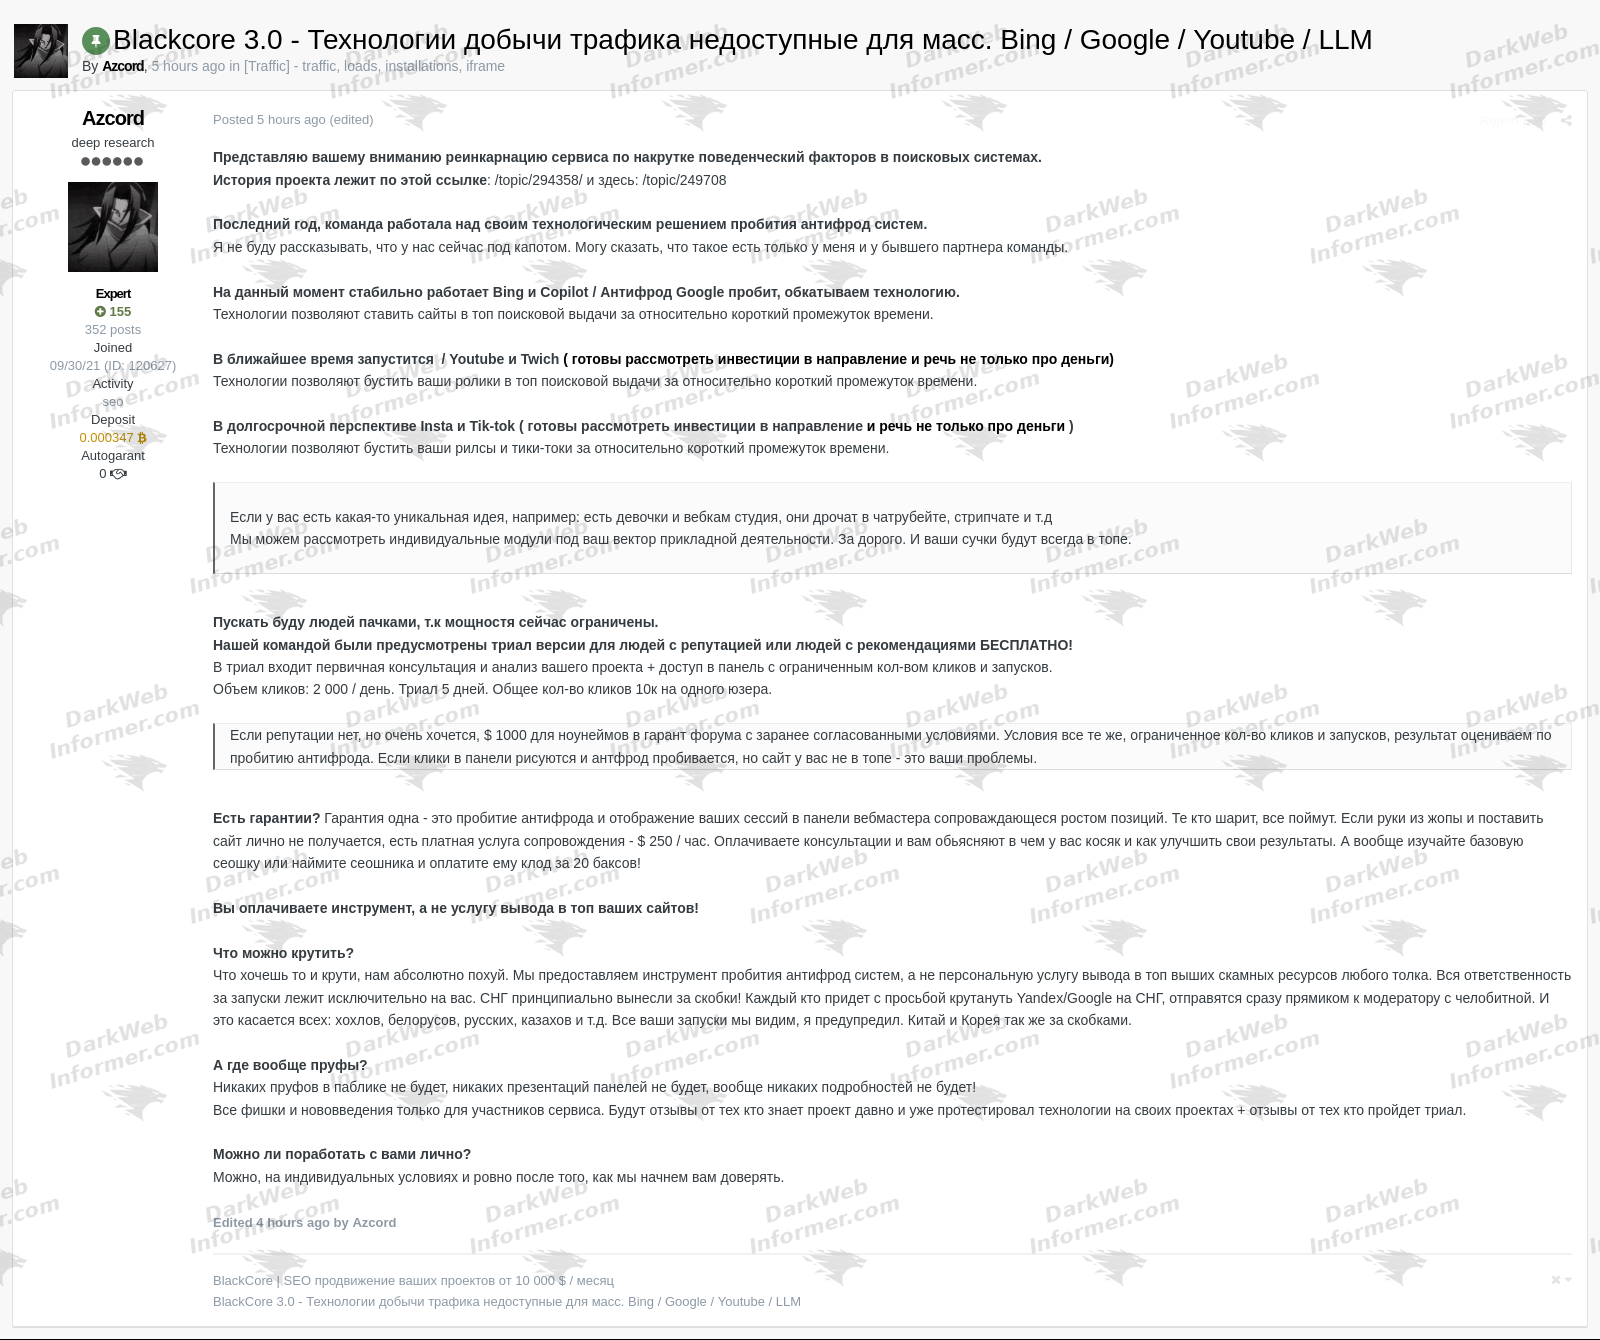
🚨 BlackCore 3.0 advertised as a search-ranking manipulation platform claiming to bypass Google and Bing anti-fraud systems
An actor known as "Azcord" is promoting BlackCore 3.0, a platform designed to artificially manipulate user engagement signals and boost websites in search rankings.
The operator claims the following capabilities:
• Bing and Microsoft Copilot manipulation operational • Google anti-fraud bypass achieved, with testing ongoing • Artificial traffic and engagement generation • YouTube and Twitch manipulation planned • Instagram and TikTok support under consideration
The service offers a five-day trial with up to 10,000 clicks for vetted users. Others must provide a $1,000 deposit, while additional support costs $250 per hour.
The operator claims the technology can improve search rankings within a relatively short period.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
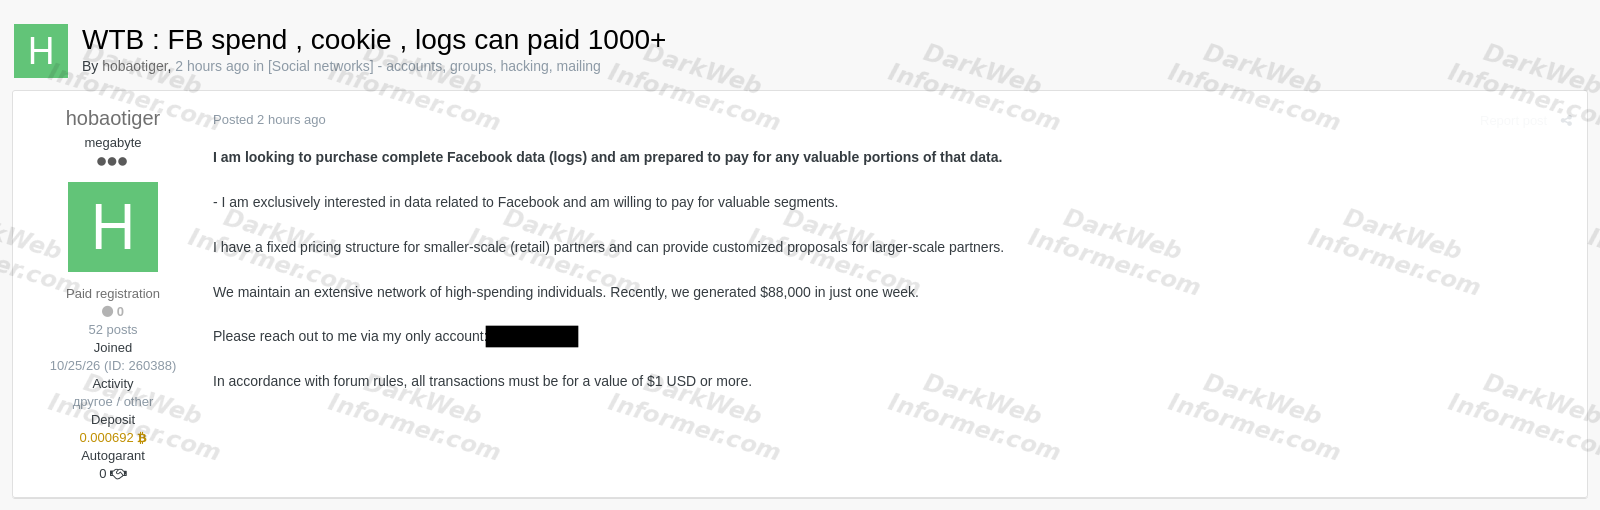
🚨 Threat actor offering $1,000+ for Facebook account logs, cookies, and advertising-related data
An actor using the handle "hoboatiger" is actively seeking compromised Facebook account information, including session cookies, infostealer logs, and data associated with advertising accounts.
The actor claims to work with a network of high-spending individuals and reports generating $88,000 in a single week.
The listing offers fixed pricing for smaller suppliers and customized agreements for larger-scale providers.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
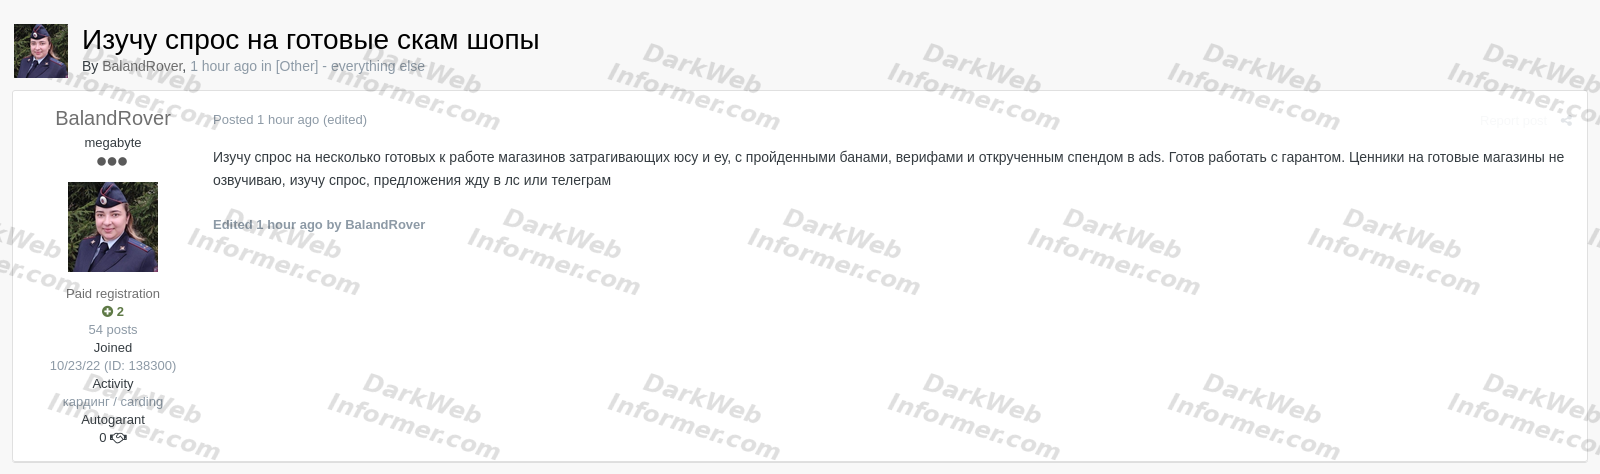
🚨 Ready-made scam stores targeting US and European customers advertised on a cybercrime forum
An actor known as "BalandRover" is gauging interest in several ready-to-operate fraudulent online stores targeting the United States and European Union.
The actor claims the stores have already undergone verification processes and accumulated advertising spend, potentially allowing buyers to begin operations without starting from scratch.
Prices have not been disclosed, and the actor is accepting inquiries through private messages and Telegram, with escrow available.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
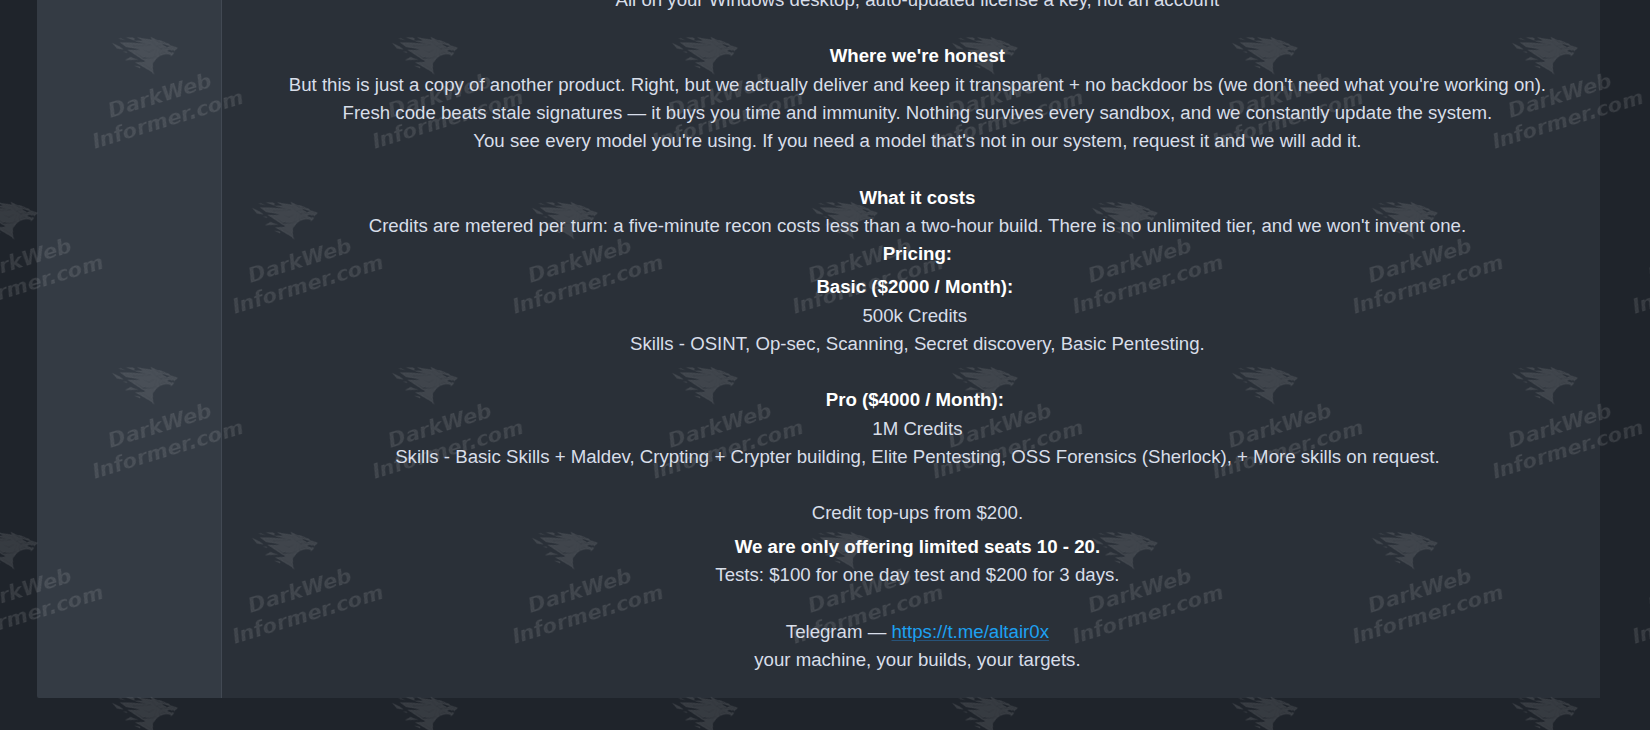
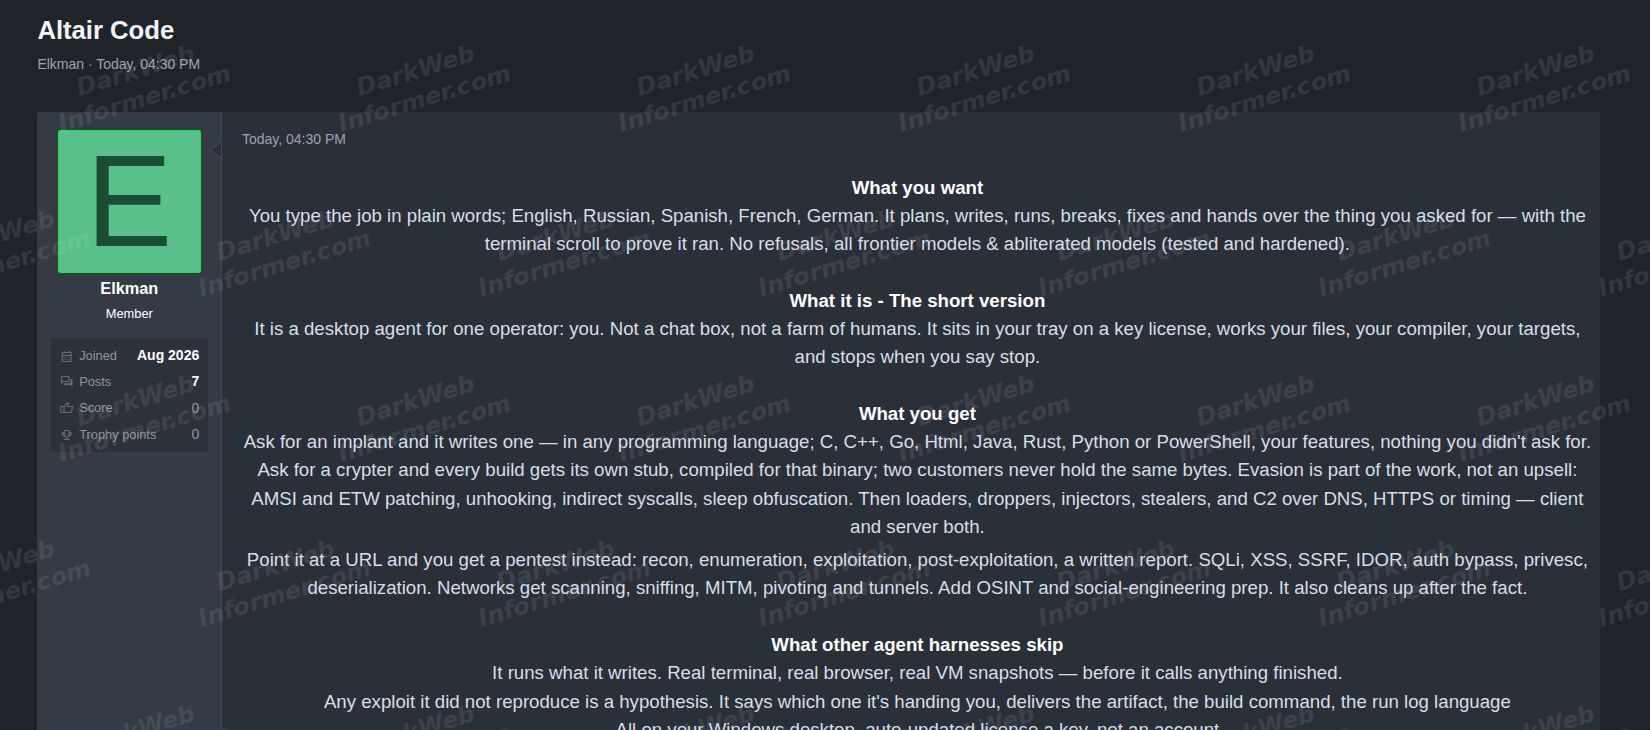
🚨 Altair Code AI agent advertised for automated malware development, exploitation, and offensive security operations
An actor known as "Elkman" is promoting Altair Code, a Windows desktop AI agent that allegedly uses unrestricted AI models to autonomously develop malware, execute penetration tests, and perform offensive security tasks through natural-language instructions.
Advertised capabilities:
• Malware implants, loaders, droppers, and infostealer development • Custom crypters and payload obfuscation • AMSI/ETW evasion, indirect syscalls, and anti-analysis • Automated vulnerability discovery and exploitation • Network reconnaissance, lateral movement, and post-exploitation • C2 infrastructure over DNS and HTTPS • Real terminal execution, browser automation, and VM testing
Pricing starts at $2,000/month for basic access and $4,000/month for advanced capabilities. One-day testing is offered for $100.
The developer claims the agent can independently write, compile, execute, debug, and deliver working tools without human intervention.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
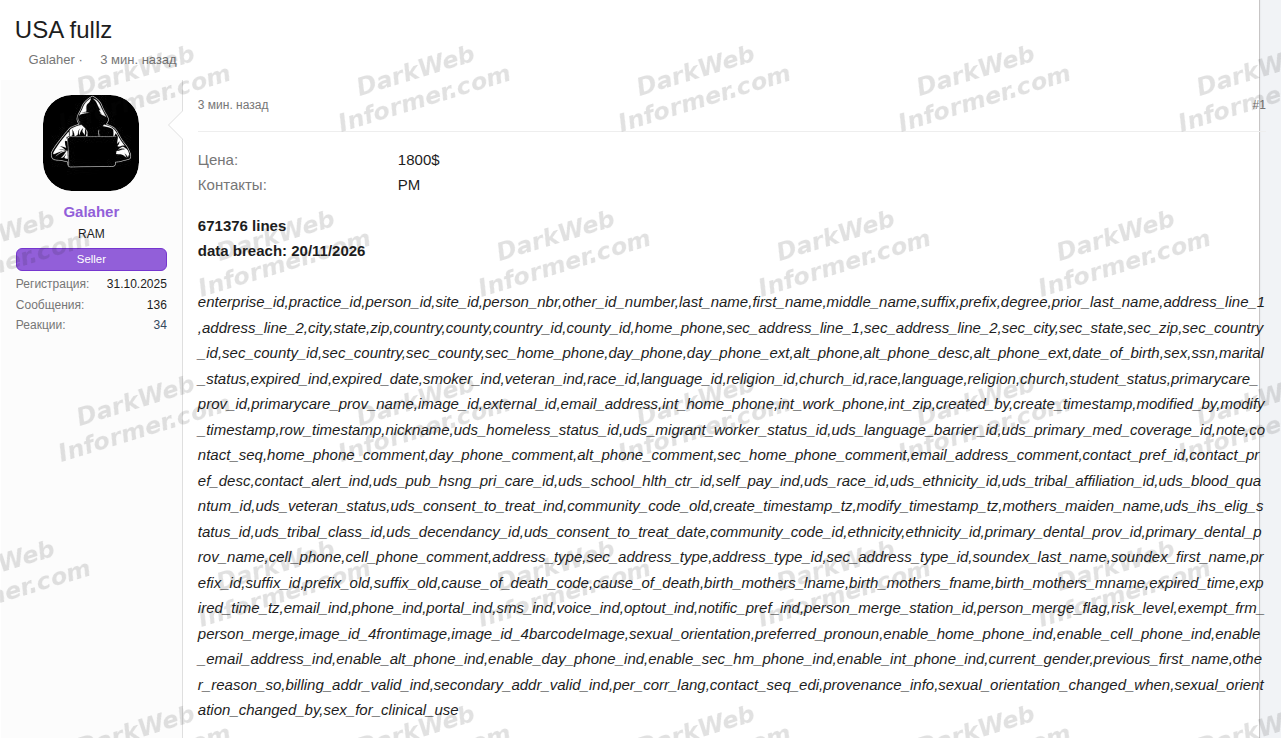
🚨🇺🇸 Over 671,000 US records containing sensitive personal and medical information offered for $1,800
An actor known as "Galaher" is selling a database allegedly containing 671,376 records, claiming the data was breached on November 20, 2026.
The advertised dataset includes:
• Full names, dates of birth, and Social Security numbers • Residential addresses, phone numbers, and emails • Healthcare provider and insurance information • Patient identifiers and medical-related records • Demographic information and other sensitive personal details
The source of the database and the affected organization have not been disclosed.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
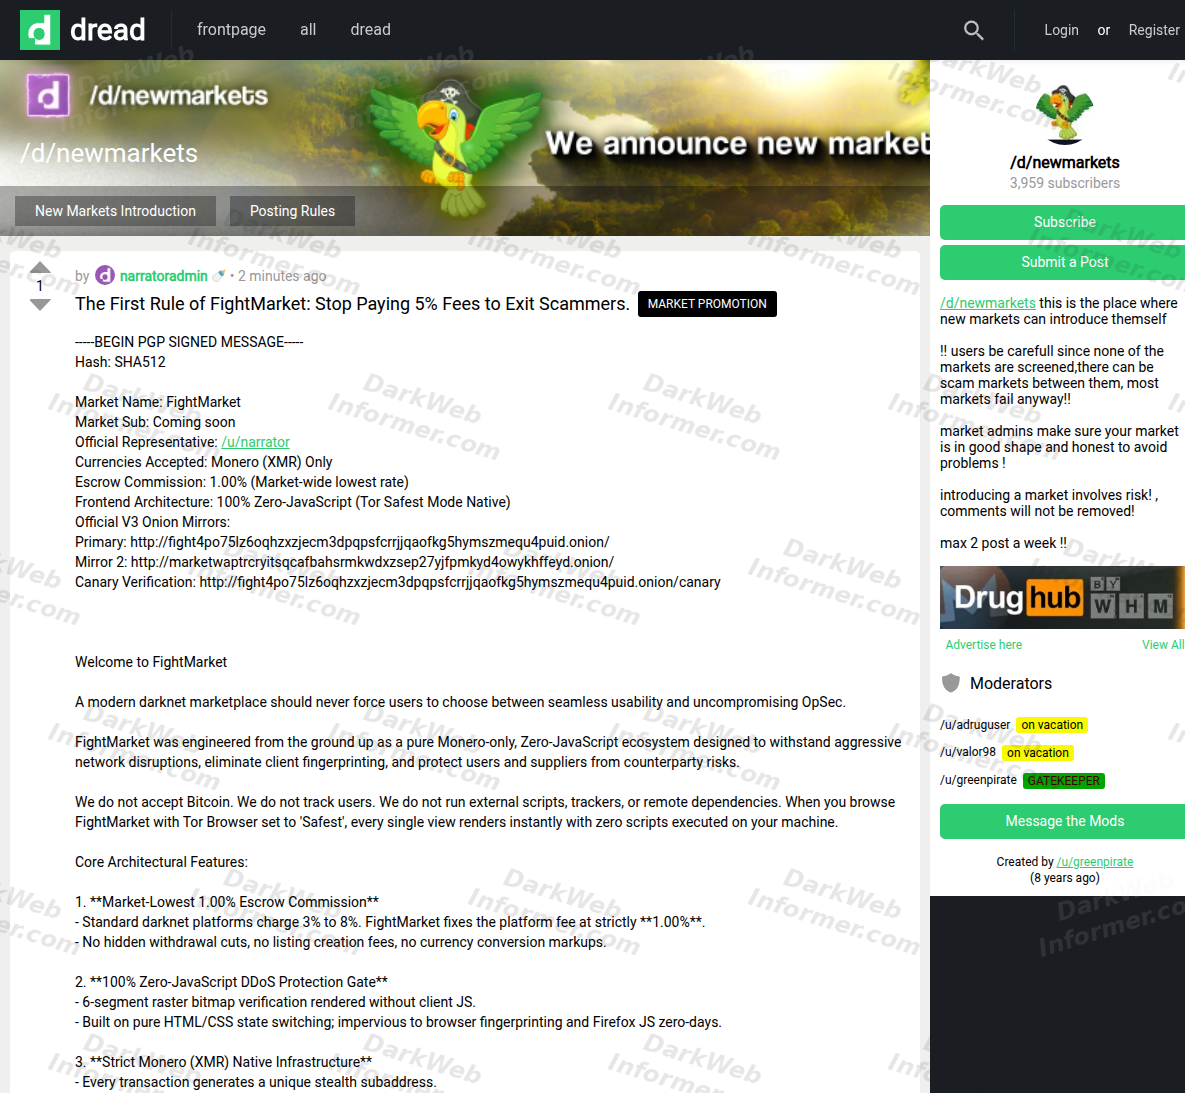
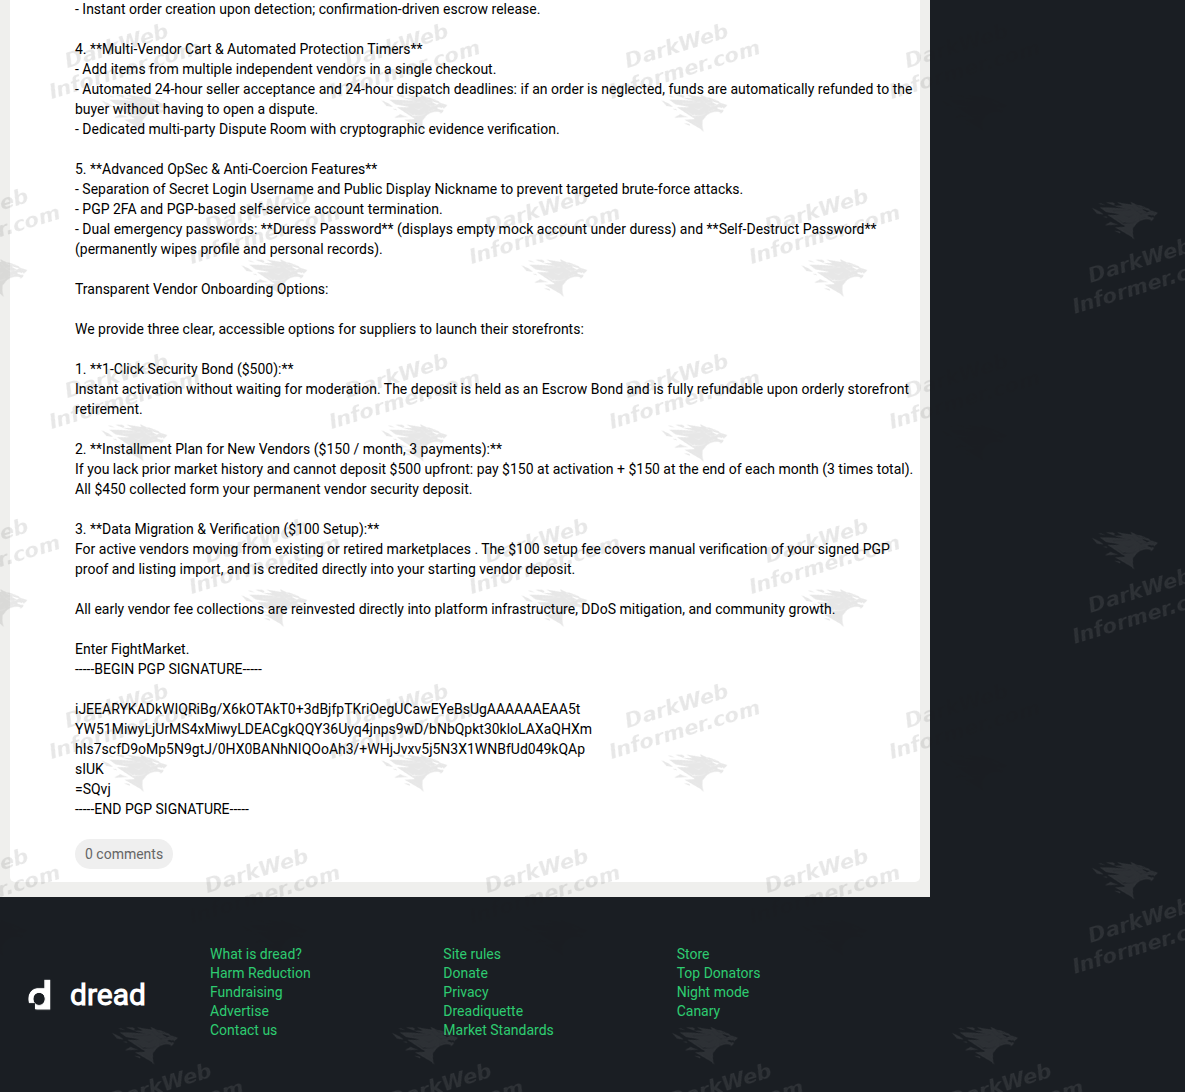
⚠️ New Darknet Market: Fight Market
Dark Web: http://fight4po75lz6oqhzxzjecm3dpqpsfcrrjjqaofkg5hymszmequ4puid[.]onion
Dark Web Mirror: http://marketwaptrcryitsqcafbahsrmkwdxzsep27yjfpmkyd4owykhffeyd[.]onion
Dread Announcement: https://dreadohblesmagfagqup24vw7catlvmqhhce5itz7wxr4vffgemjzaad[.]onion/post/1be9e51cef38a74ab2ee
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
🚨🇺🇸 Initial Access: $13.1B US Entertainment Company
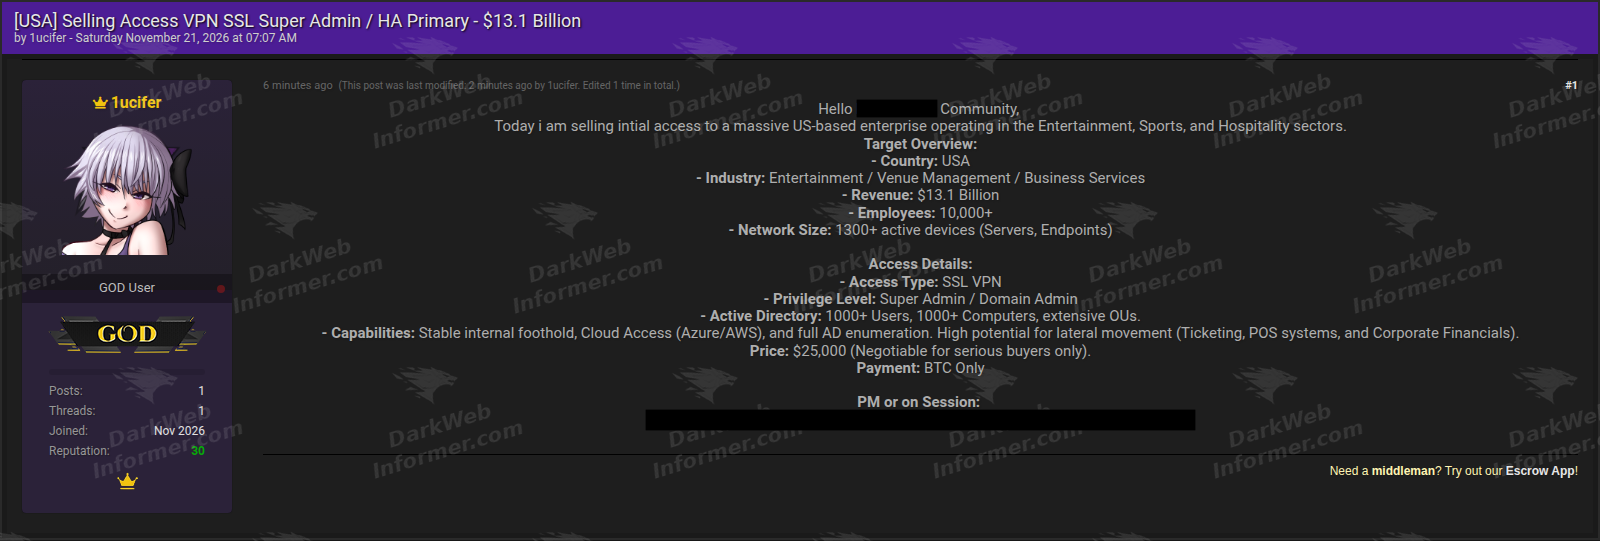
A threat actor is advertising SSL VPN access to a major U.S. entertainment, sports, and hospitality company reportedly generating $13.1B in revenue.
The advertised access includes Super Admin/Domain Admin privileges, Azure and AWS access, and visibility across an Active Directory environment with 1,000+ users and 1,000+ computers.
The actor claims the network includes more than 1,300 active devices and potential access paths to ticketing, POS, and corporate financial systems.
The access is listed for $25,000 in BTC.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
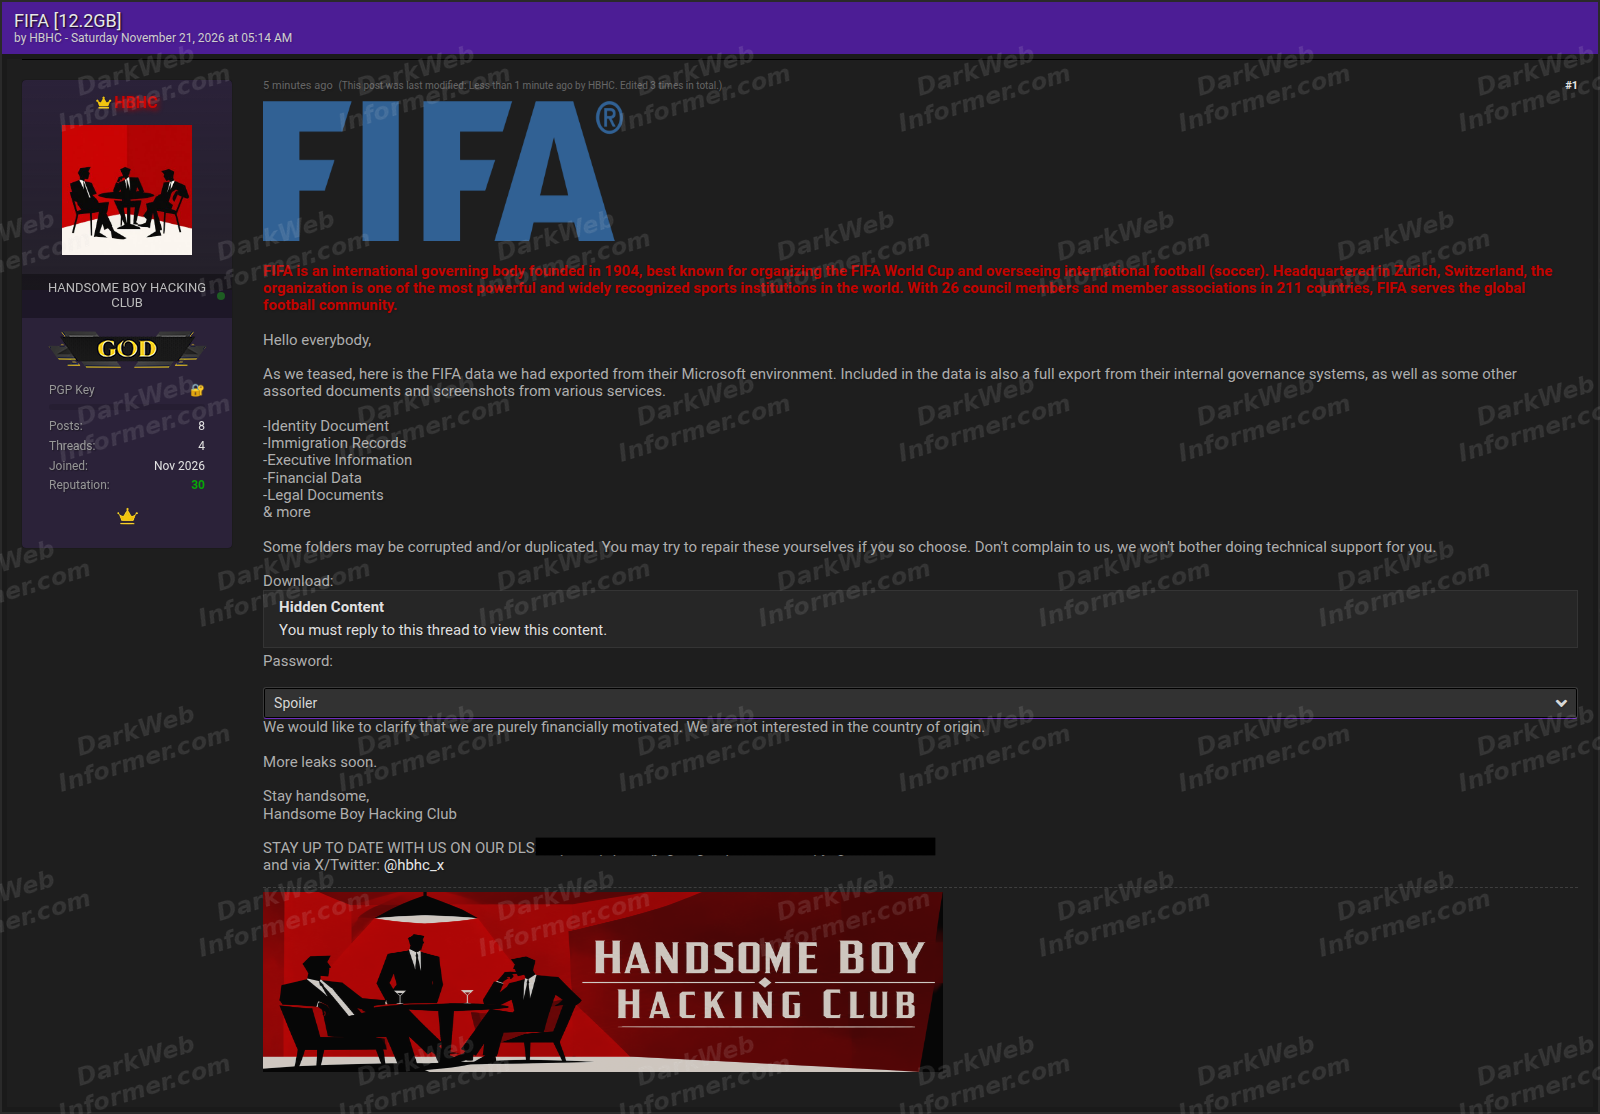
🚨🇨🇭 FIFA allegedly breached, 12.2 GB of sensitive internal documents leaked
The Handsome Boy Hacking Club (HBHC) claims to have released data stolen from FIFA, the international governing body of football, headquartered in Switzerland.
The group claims the files were extracted from FIFA's Microsoft environment and internal governance systems.
Data allegedly exposed:
• Identity and immigration documents • Executive information • Financial records • Legal documents • Internal governance records and screenshots
The group has advertised the files for download and warned that some folders may contain corrupted or duplicate data.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
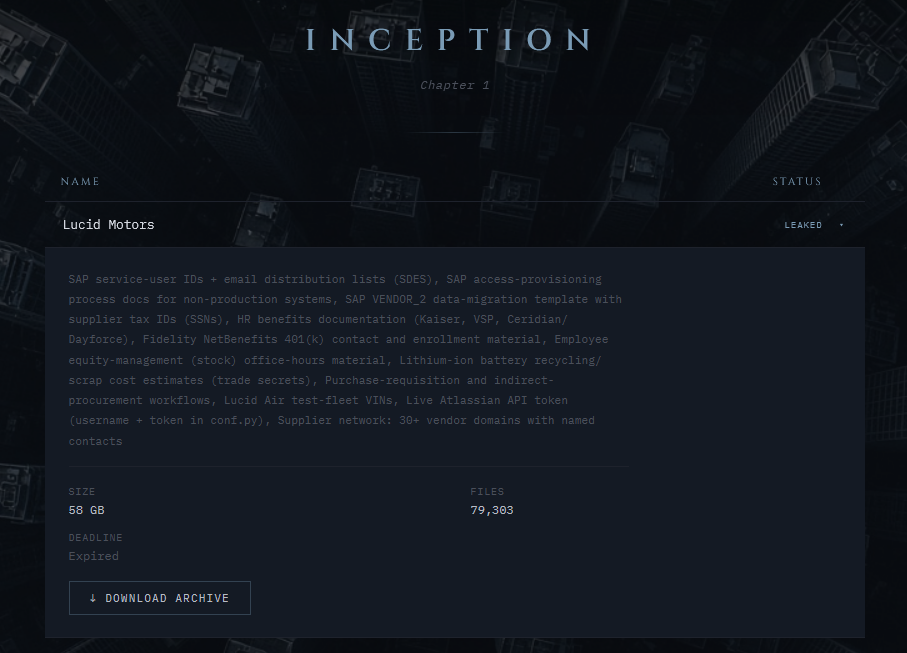
‼️🇺🇸 Inception ransomware claims Lucid Motors and says 58 GB of company data has already been leaked.
🇺🇸 Lucid Motors - A U.S.-based electric vehicle manufacturer known for the Lucid Air and Lucid Gravity.
The listing claims 58 GB across 79,303 files, including:
• SAP service-user IDs and email distribution lists • SAP access-provisioning and supplier data • Supplier tax IDs and Social Security numbers • Employee benefits and 401(k) documentation • Employee equity-management records • Lithium-ion battery recycling and scrap-cost estimates • Purchase requisition and procurement workflows • Lucid Air test-fleet VINs • A live Atlassian API token • Supplier information spanning 30+ vendor domains
The deadline is marked as expired and the archive as leaked.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. Crypto friendly. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
🚨🇺🇸 FBI investigating another suspected cyberattack, this time targeting nationwide criminal database
According to CNN, citing two people briefed on the investigation, suspected hackers gained access to the National Crime Information Center (NCIC), a critical system used by federal, state, and local law enforcement agencies across the United States.
The database contains information used for criminal background checks, outstanding arrest warrants, missing persons, and other law enforcement investigations.
This marks the second reported FBI breach in recent months, following a September incident in which hackers stole sensitive personal information belonging to federal agents and job applicants.
The identities of the attackers, the extent of the latest intrusion, and whether any sensitive criminal records were stolen remain unclear.
Source: https://www.cnn.com/2026/11/20/politics/fbi-hacked-again-target-crime-databas
🚨🇺🇸 CrowdStrike reportedly in talks to acquire Zscaler in potential $32 billion cybersecurity mega-deal
According to Bloomberg and Reuters, discussions between the two cybersecurity giants are ongoing, with a potential agreement possibly coming soon. However, no deal has been finalized, and negotiations could still fall apart.
The acquisition would combine CrowdStrike's Falcon endpoint protection platform with Zscaler's cloud security and zero-trust network access technologies, creating one of the world's largest cybersecurity companies with a combined market value of approximately $265 billion.
Following the reports, Zscaler shares surged more than 16% in after-hours trading, while CrowdStrike shares declined. Neither company has publicly confirmed the negotiations.
🚨🇺🇸 Illinois officials investigate suspected cyberattack targeting Algonquin Dam on the Fox River
Illinois authorities are investigating an apparent cyberattack targeting the Algonquin Dam in McHenry County on November 16.
The Illinois Department of Natural Resources says staff immediately took action to prevent unauthorized access and maintain dam operations. Officials have not disclosed how the attack occurred or whether any systems were compromised.
Illinois State Police, state emergency management and technology agencies, and the federal Cybersecurity and Infrastructure Security Agency (CISA) are investigating.
Authorities say there is currently no indication the incident is connected to other recent cyberattacks or outages across the United States.
Source: https://www.cbsnews.com/chicago/news/algonquin-dam-fox-river-cyberattack/
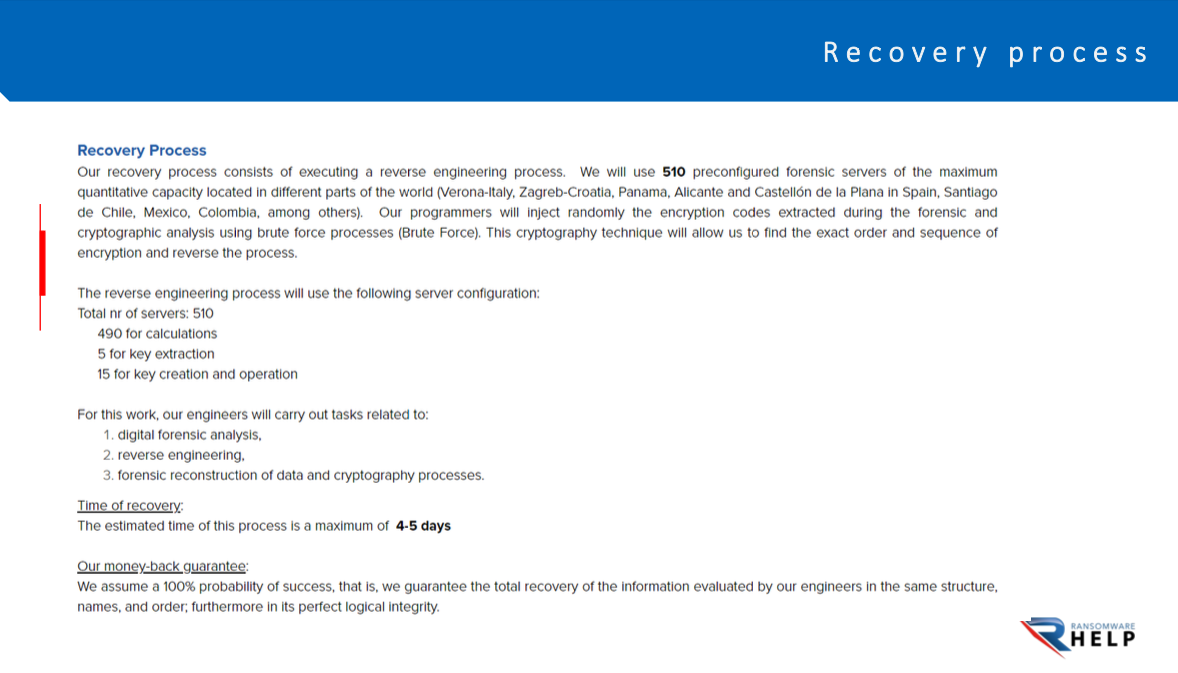
👀 CTO of ‘RansomwareHelp’ Indicted for Wire Fraud
Source: https://krebsonsecurity.com/2026/11/cto-of-ransomwarehelp-indicted-for-wire-fraud/
🚨🇨🇦 Staples Canada confirms website breach exposing customers' personal information and encrypted passwords
Staples Canada has disclosed a cybersecurity incident involving its Staples Print website, where an unauthorized party gained access to customer information between November 1 and 5.
The compromised information includes names, email addresses, shipping and billing addresses, order summaries, and encrypted passwords.
Staples says no financial information was exposed and the attacker has been removed from its systems. Potentially affected customers will be required to reset their passwords when they next log in.
The company has not disclosed how many customers were affected and is continuing to investigate the incident.
Source: https://globalnews.ca/news/12160464/staples-print-hack/
🚨🇺🇸 Sacramento man sentenced to 27 years in prison for sexually exploiting children through Snapchat and Instagram
Francisco Mariano Orantes, 33, was sentenced to 27 years in federal prison after sexually exploiting at least seven underage girls between 2023 and 2024.
According to the Department of Justice, Orantes impersonated a teenage girl on Snapchat and Instagram to gain victims' trust and manipulate them into producing explicit images and videos.
Investigators discovered that he used geolocation tools to identify victims' home addresses and schools, threatening to release their private images if they refused his demands.
Authorities recovered more than 11,000 images and 14,000 videos of child sexual abuse material from his devices. Orantes pleaded guilty in May 2026.
🚨🇺🇸 Minnesota county confirms cyberattack exposing Social Security numbers, medical records, fingerprints, and law enforcement information
Otter Tail County, Minnesota, has confirmed that hackers accessed its government network between July 3 and August 1, 2026, stealing sensitive information maintained by the county.
The compromised data may include names, addresses, Social Security numbers, driver's license numbers, financial accounts, medical records, health insurance information, police reports, passport numbers, immigration identification numbers, and fingerprints.
The county says the volume and complexity of the stolen files made it impractical to identify and individually notify everyone affected. Instead, officials issued a public notification on November 16 and are offering 12 months of complimentary identity theft protection.
The total number of affected individuals remains unknown.
Source: https://ottertailcounty.gov/notice-of-data-security-incident/
🚨🇺🇸 Prism Medical Products confirms data breach affecting over 1.3 million people, exposing medical and financial information
Prism Medical Products, a subsidiary of healthcare distributor Henry Schein, has confirmed that hackers accessed its systems and stole sensitive information belonging to approximately 1.33 million individuals.
The breach was discovered on October 19 and potentially exposed names, Social Security numbers, driver's license numbers, medical records, health insurance details, and financial account information.
The Wall Street extortion group has claimed responsibility and says it is publishing stolen data. Claim is currently unverified.
Prism says it has rebuilt affected systems, restored operations, and is offering impacted individuals 24 months of free credit and dark web monitoring.
Source: https://www.inforisktoday.com/prism-medical-products-notifying-13-million-data-theft-a-33474
🚨🇺🇸 Hackers access financial and medical information of nearly 4,000 retired New York City government workers
Hackers breached a database operated by Atticus Administration, exposing sensitive information belonging to as many as 4,000 retired NYC employees awaiting medical reimbursement payments.
The attackers accessed the system in September and October, potentially exposing names, financial information, medical provider details, identification numbers, and medical co-payment records.
The database was being used to distribute up to $53 million in settlement reimbursements. Investigators also discovered suspicious reimbursement claims that may have been attempts to steal settlement funds.
EmblemHealth says the fraudulent claims were detected and no settlement payments have been distributed. The attackers' identities remain unknown.
🚨🇺🇸 Phoebe Putney Health System confirms patient data exposed in third-party vendor breach
Georgia-based Phoebe Putney Health System has confirmed that patients' sensitive personal and medical information was stolen following a cyberattack on MedCom Solutions, a former billing services provider.
The breach occurred between September 18 and 22, 2025, and exposed information including names, Social Security numbers, dates of birth, health insurance details, medical diagnoses, patient account numbers, and prescription information.
Phoebe says it was no longer working with MedCom when the breach occurred, but the vendor still retained patient records. Other hospitals across southern Georgia were also affected.
MedCom has begun notifying impacted patients and is offering complimentary credit monitoring. The total number of affected individuals remains undisclosed.
🚨🇨🇦 Bell Canada confirms cyberattack involving an alleged AI-powered hacker, enterprise customer data stolen
Bell Canada has confirmed that a threat actor breached multiple systems on November 17, stealing enterprise customer information from a platform used to order and manage telecommunications network connections.
The stolen data potentially includes names, job titles, corporate email addresses, phone numbers, business addresses, support ticket information, and IP addresses associated with network equipment.
Bell described the attacker as "agentic," suggesting possible use of AI-powered tools, although the company has not confirmed how AI was involved.
The company says the breach has been contained, customer services were not disrupted, and no credentials or highly sensitive personal information were exposed. The attackers' identities and the number of affected customers remain unknown.
Source: https://www.cbc.ca/news/business/bell-agentic-cyber-attack-9.7430468
⚠️ New Forum: IntelForums
Clearnet: intelforums[.]cc
🚨🇫🇷 La Poste confirms massive data breach exposing personal information of 22 million people in France
French postal giant La Poste has confirmed that its subsidiary Maileva suffered a cyberattack in mid-September, resulting in the theft of personal information belonging to approximately 22 million people, roughly one-third of France's population.
The stolen information includes names and postal addresses belonging to recipients of documents sent by businesses and public institutions.
Depending on the affected organization, additional information contained in correspondence may also have been exposed.
La Poste says no data was altered or destroyed. France's data protection authority (CNIL) has been notified, affected organizations have been informed, and a criminal investigation is underway.
Source: https://www.lapostegroupe.com/fr/actualite/cyberattaque-de-maileva-ce-quil-faut-savoir
Pushed a fix to the threat feed that should stop alerts from appearing, randomly disappearing after a short time, and then reappearing permanently on the first page. You will need to refresh the feed to get the update.
Pushed a fix to the threat feed that should stop alerts from appearing, randomly disappearing after a short time, and then reappearing permanently on the first page.
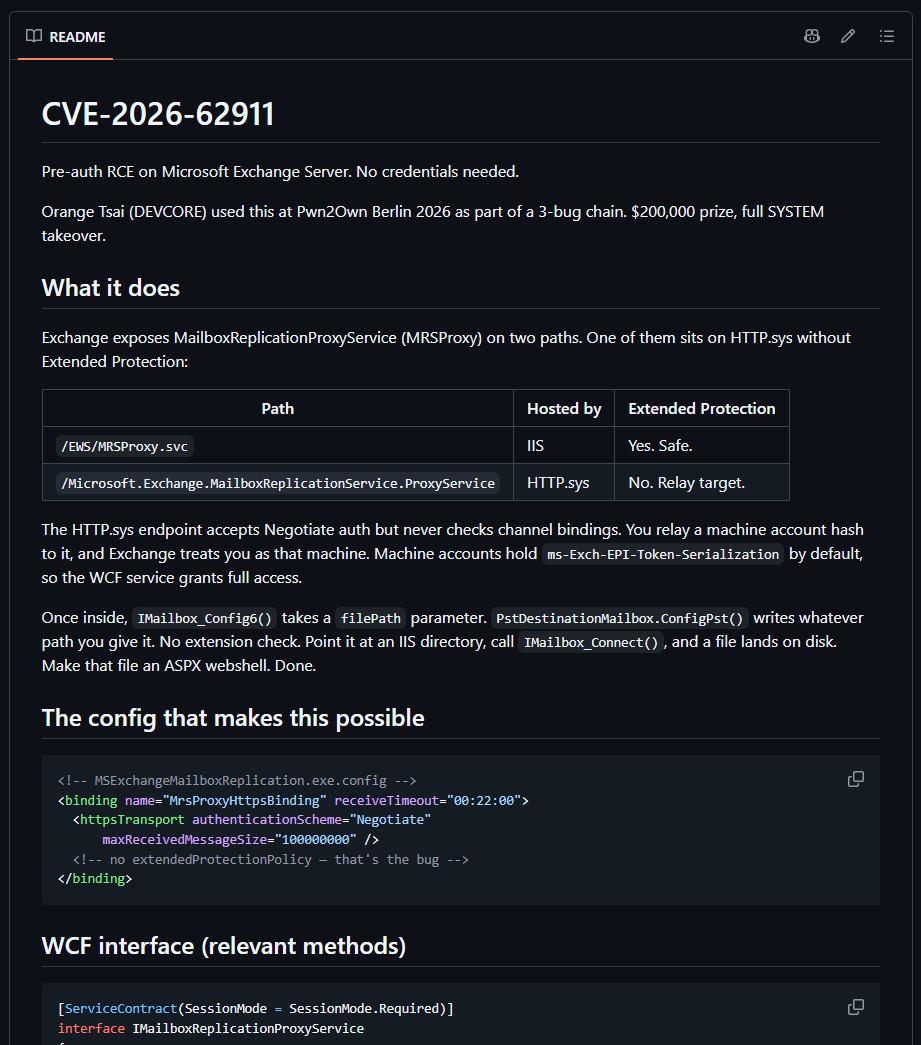
🚨 A Microsoft Exchange authentication bypass can be chained into SYSTEM-level code execution; CVE-2026-62911
PoC: https://github.com/hypnguyen1209/CVE-2026-62911
The flaw is an authentication bypass by capture-replay in Microsoft Exchange Server. Public exploit code chains NTLM relay against the MRSProxy service and can ultimately write a webshell to disk, leading to code execution as SYSTEM.
Microsoft Exchange Server | Authentication Bypass / RCE Chain:
• CVSS: 8.0 High • Attack: Network-based • Impact: Privilege escalation and potential SYSTEM-level code execution • Affected: Exchange Server 2016 CU23, Exchange Server 2019 CU14/CU15, and Exchange Server Subscription Edition RTM below patched builds • Fixed: August 2026 security updates
The PoC demonstrates the relay chain against Exchange MRSProxy and shows how the flaw can be combined with other primitives to achieve full server compromise.
🚨🇩🇪 Microsoft 365 outage leaves 15 hotel guests poisoned by chlorine after critical safety alerts fail
A hotel at Germany's Phantasialand theme park reported 15 guests suffering chlorine poisoning after the recent Microsoft 365 outage prevented automated safety warnings from reaching staff.
A malfunctioning pool dosing system released excessive chlorine, but alerts about dangerous levels were not received because the hotel's monitoring system relied on email services disrupted by the outage.
Around 40 emergency responders were deployed, with four victims hospitalized and one kept for further observation.
The incident highlights the dangers of relying solely on cloud-based services for critical safety systems without independent backup alarms.
Source: https://web26.bernama.com/en/region/news.php?id=2634698
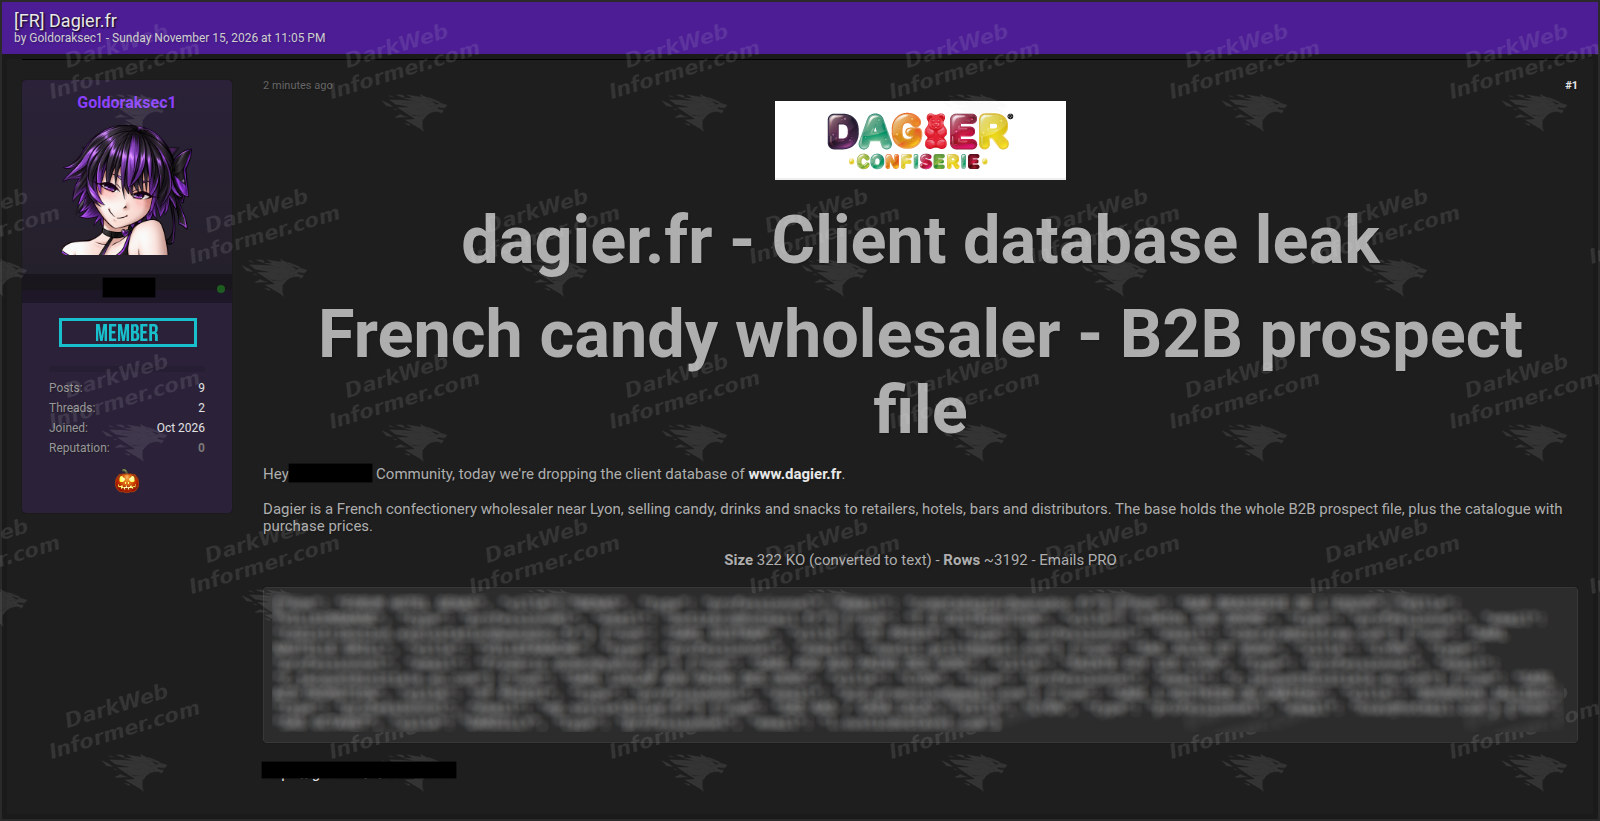
🚨🇫🇷 Dagier customer database allegedly leaked, over 3,100 business records exposed
Threat actor "Goldoraksec1" claims to have leaked a client database belonging to Dagier, a French confectionery wholesaler near Lyon.
Victim: Dagier Sector: Wholesale / Food Distribution Actor: Goldoraksec1 Records: Approximately 3,192
Data allegedly exposed:
• Business and customer names • Professional email addresses • Cities and business locations • Customer classifications • Product catalog and wholesale purchase prices
The actor has published sample records and made the dataset available for download.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
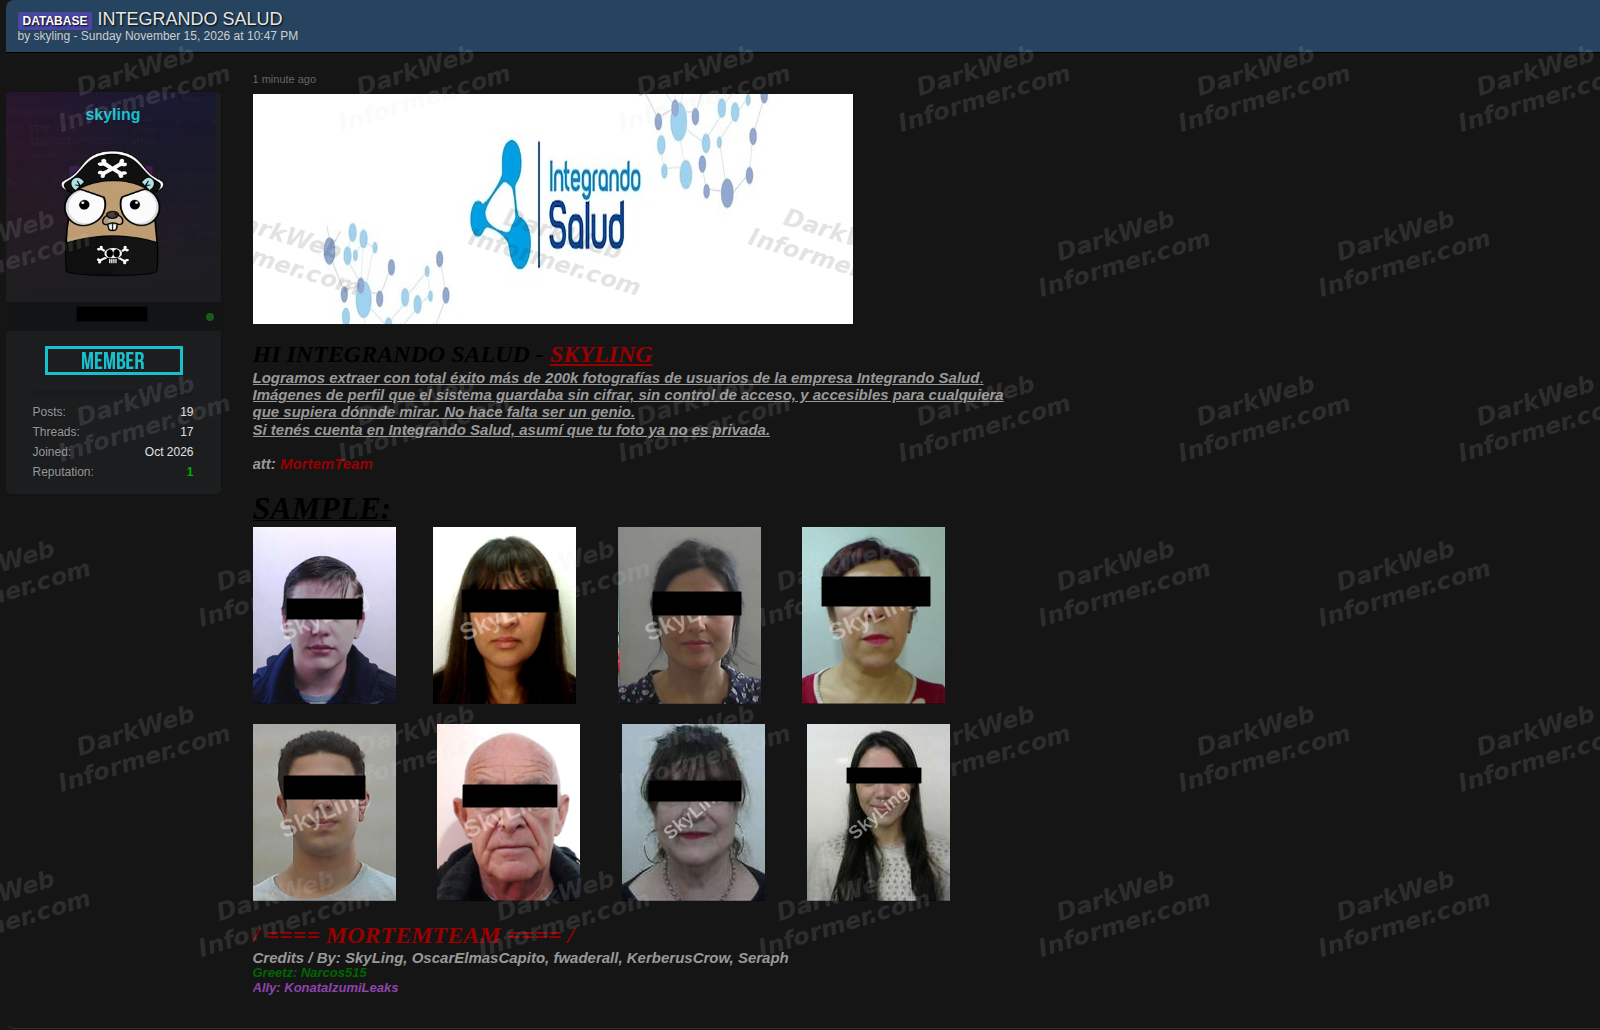
🚨🇦🇷 Integrando Salud allegedly breached, over 200,000 user photographs exposed
Threat actor "SkyLing", associated with MortemTeam, claims to have extracted more than 200,000 user photographs from Integrando Salud, an Argentine healthcare software platform.
Victim: Integrando Salud Sector: Healthcare / Medical Software Actor: SkyLing / MortemTeam Records: 200,000+ photographs
Data allegedly exposed:
• User profile photographs • Images stored without encryption • Photographs allegedly accessible without proper access controls
The actor claims the images were accessible due to inadequate security protections and has published several sample photographs as evidence.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
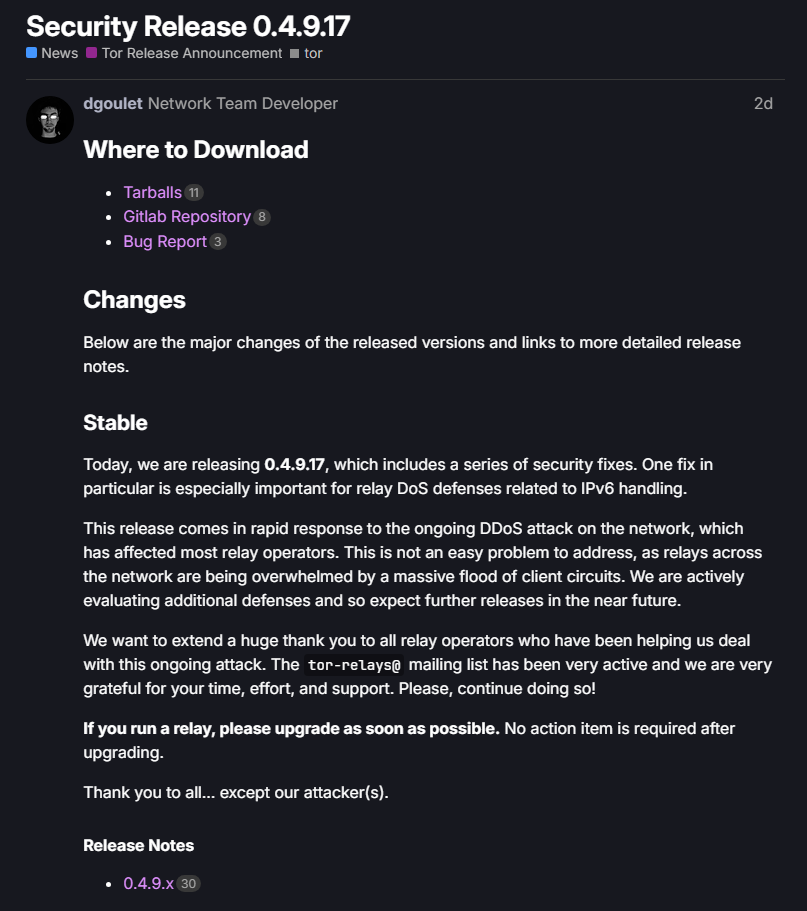
🚨 Tor network under massive DDoS attack, emergency security update released as relays are overwhelmed
The Tor Project has released an emergency security update, version 0.4.9.17, in response to an ongoing distributed denial-of-service (DDoS) attack affecting most relay operators across its network.
Attackers are flooding relays with massive numbers of client circuits, overwhelming infrastructure and disrupting network operations.
The update strengthens IPv6-based DoS protections by tracking clients by network prefix rather than individual IP addresses.
Tor warns that defending against the attack remains challenging and additional security releases may be necessary. Relay operators are urged to upgrade immediately.
Source: https://forum.torproject.org/t/security-release-0-4-9-17/22454
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
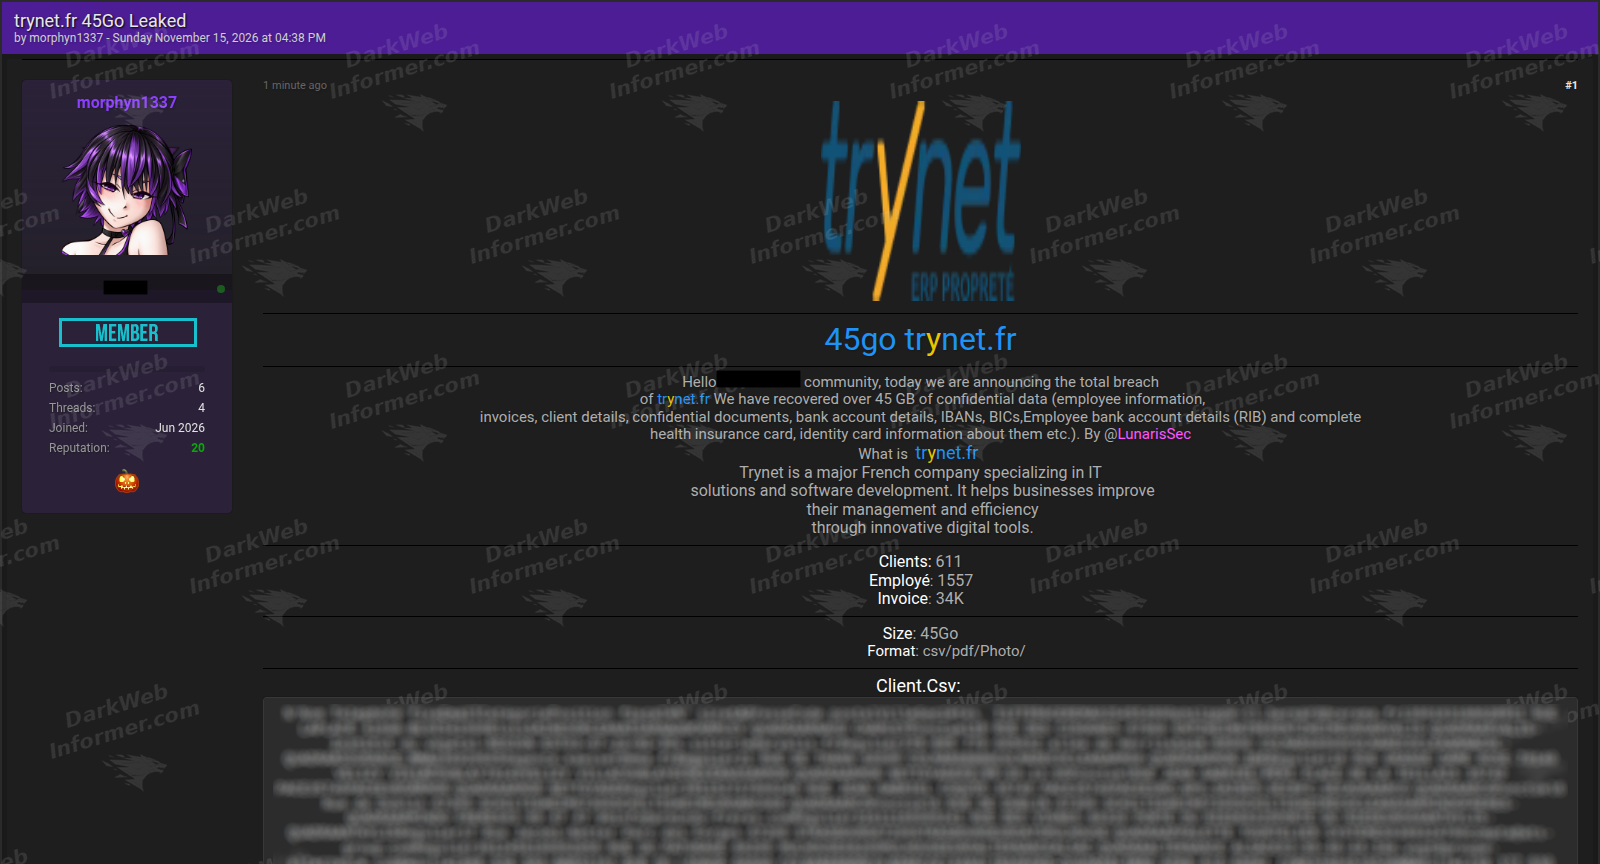
🚨🇫🇷 Trynet allegedly breached, 45 GB of sensitive corporate and employee data leaked
Threat actor "morphyn1337", associated with LunarisSec, claims to have compromised Trynet, a French IT solutions and software development company.
Victim: Trynet Sector: IT / Software Development Actor: morphyn1337 / LunarisSec Data: 45 GB | 1,557 employees | 611 clients | 34K invoices
Data allegedly exposed:
• Employee and customer information • Confidential corporate documents • Invoices and financial records • Bank account details, IBANs, BICs, and RIBs • Health insurance cards and identity documents
The actor has published samples and a download link for the allegedly stolen files.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
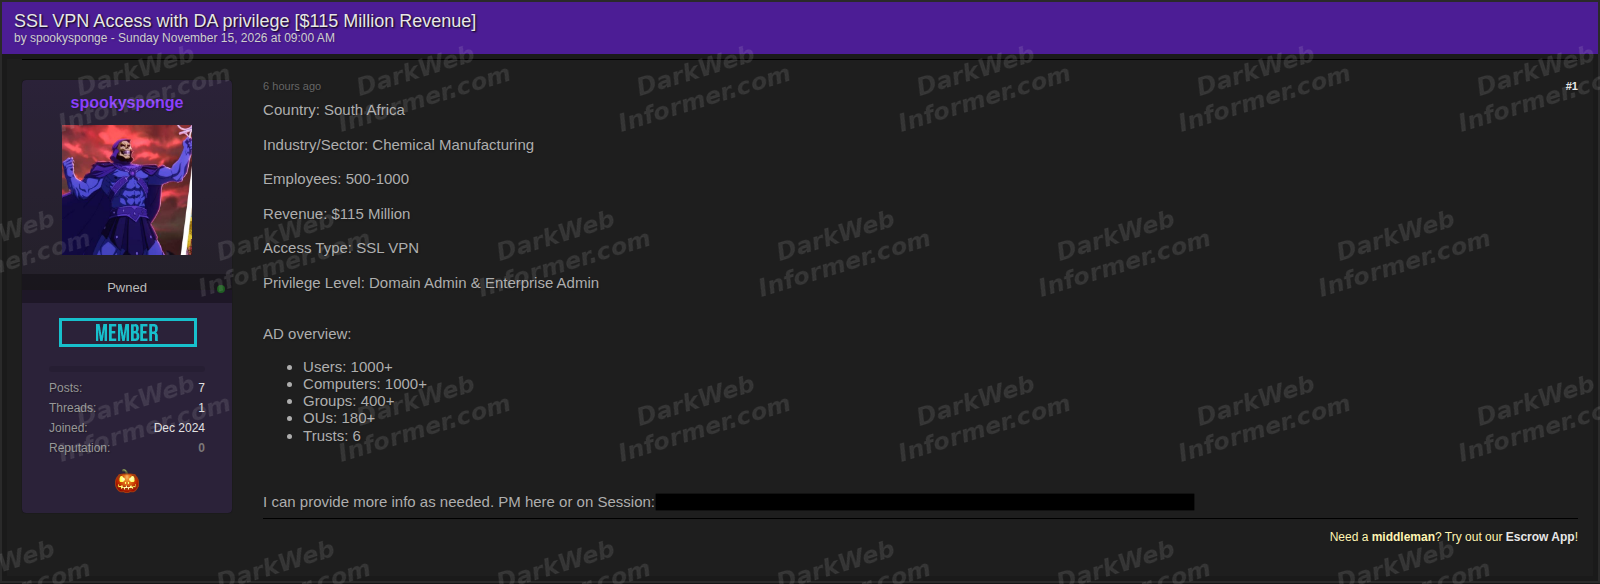
🚨🇿🇦 Initial Access: South African Chemical Manufacturer
A threat actor is advertising SSL VPN access to an unnamed South African chemical manufacturing company reportedly generating $115M in revenue.
The advertised access includes Domain Admin and Enterprise Admin privileges across an Active Directory environment with 1,000+ users, 1,000+ computers, 400+ groups, 180+ OUs, and six trusts.
The company is described as having 500-1,000 employees.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
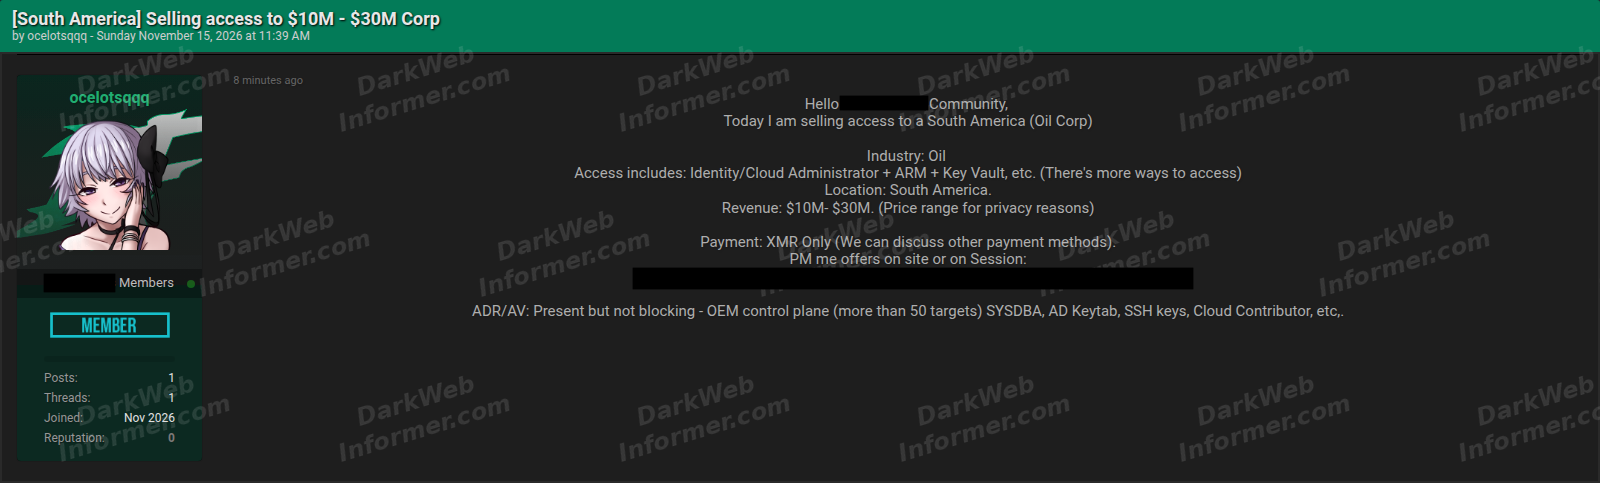
🚨🌎 Initial Access: South American Oil Company
A threat actor is advertising access to an unnamed South American oil company reportedly generating $10M-$30M in revenue.
The advertised access includes Identity/Cloud Administrator privileges, ARM and Key Vault access, SYSDBA access, AD keytabs, SSH keys, Cloud Contributor privileges, and an OEM control plane covering more than 50 targets.
The actor claims endpoint security is present but not blocking the access. Payment is requested in XMR.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
🚨 SeverVault launches marketplace advertising millions of infostealer logs and over 1 billion compromised accounts
Clearnet:
sever[.]to sever[.]ws sever[.]cx sever[.]st
Dark Web:
http://severgoodb3kdzmdnrnx3gb4jbw4gxe43mhvnxaacfq7oowb2ttsh7id[.]onion
http://sever4apt73wclanpzgoelsscbj274xupr4npybhyr4vyvxl7jlarrqd[.]onion
http://severown5xd6ojimw7qij32dvgeav5ath7fei4w7rbui5zo2rutk3yad[.]onion
http://severxpppwio5sku5ffx2ddlbqszqous3wr7hph52dlcbdr3henfibid[.]onion
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
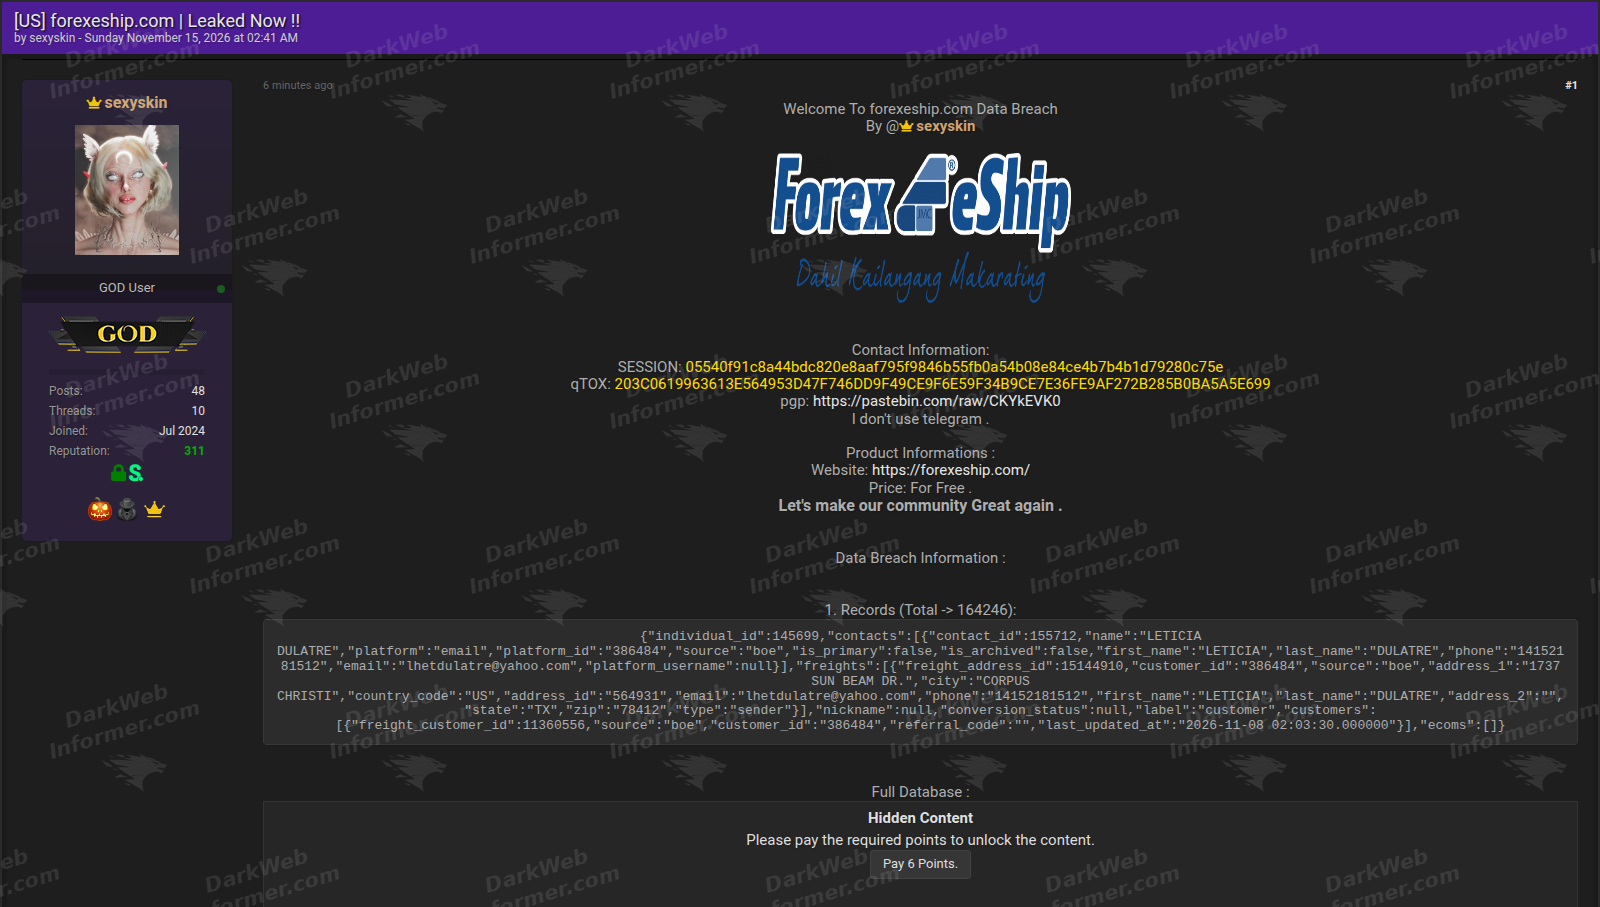
🚨🇺🇸 Forex eShip allegedly breached, over 164,000 records leaked
Threat actor "sexyskin" claims to have compromised Forex eShip, a shipping and logistics services provider, and released a database containing customer and shipment-related information.
Victim: Forex eShip Sector: Shipping / Logistics Actor: sexyskin Records: 164,246
Data allegedly exposed:
• Customer names and contact information • Email addresses and phone numbers • Residential and delivery addresses • Freight customer and account identifiers • Shipping and customer account records
The actor has published sample records and made the full database available for download.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
⚠️ New Darknet Market: Eidos Market
Dark Web: http://eidosvous7edu6jv7c2cgvytomvln6zgv4x6uggsio4pvvbzinmlurad[.]onion
Dread Announcement: https://dreadohblesmagfagqup24vw7catlvmqhhce5itz7wxr4vffgemjzaad[.]onion/post/760f3e3f563b874ba394
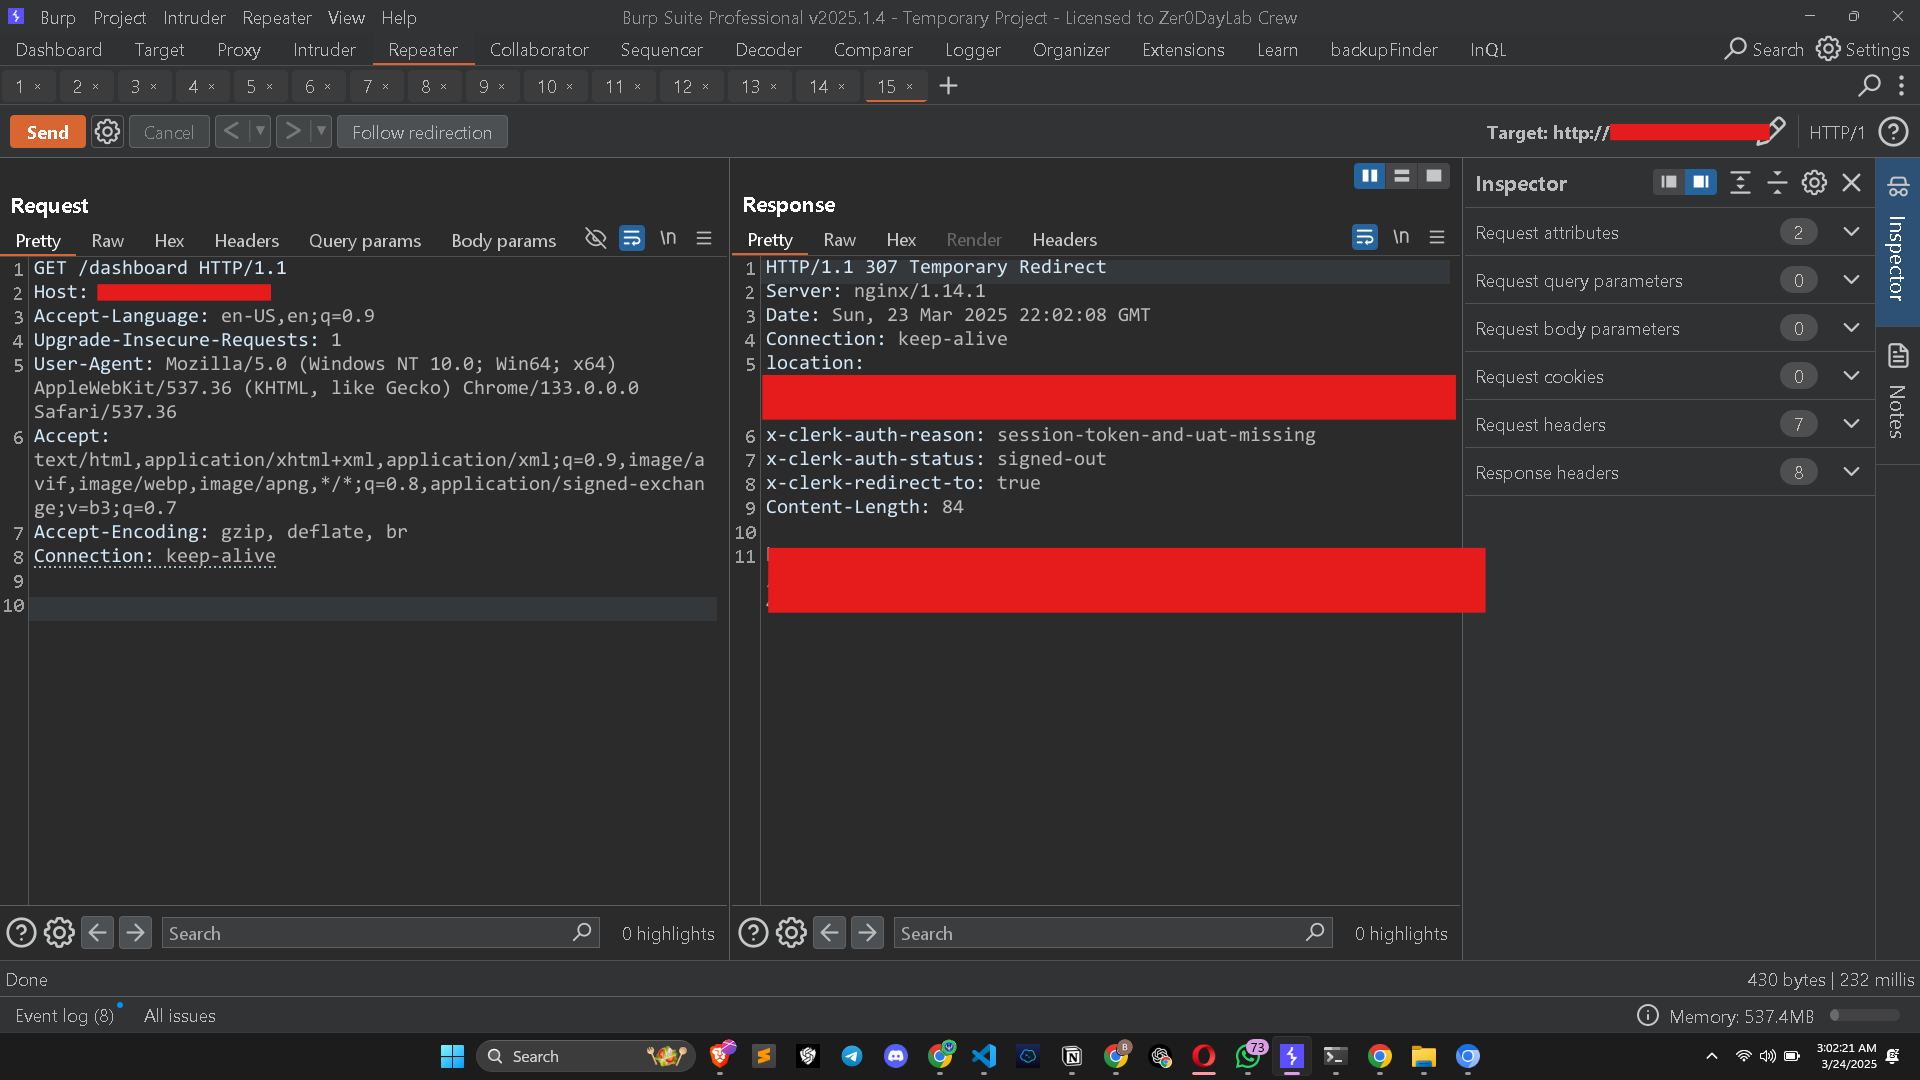
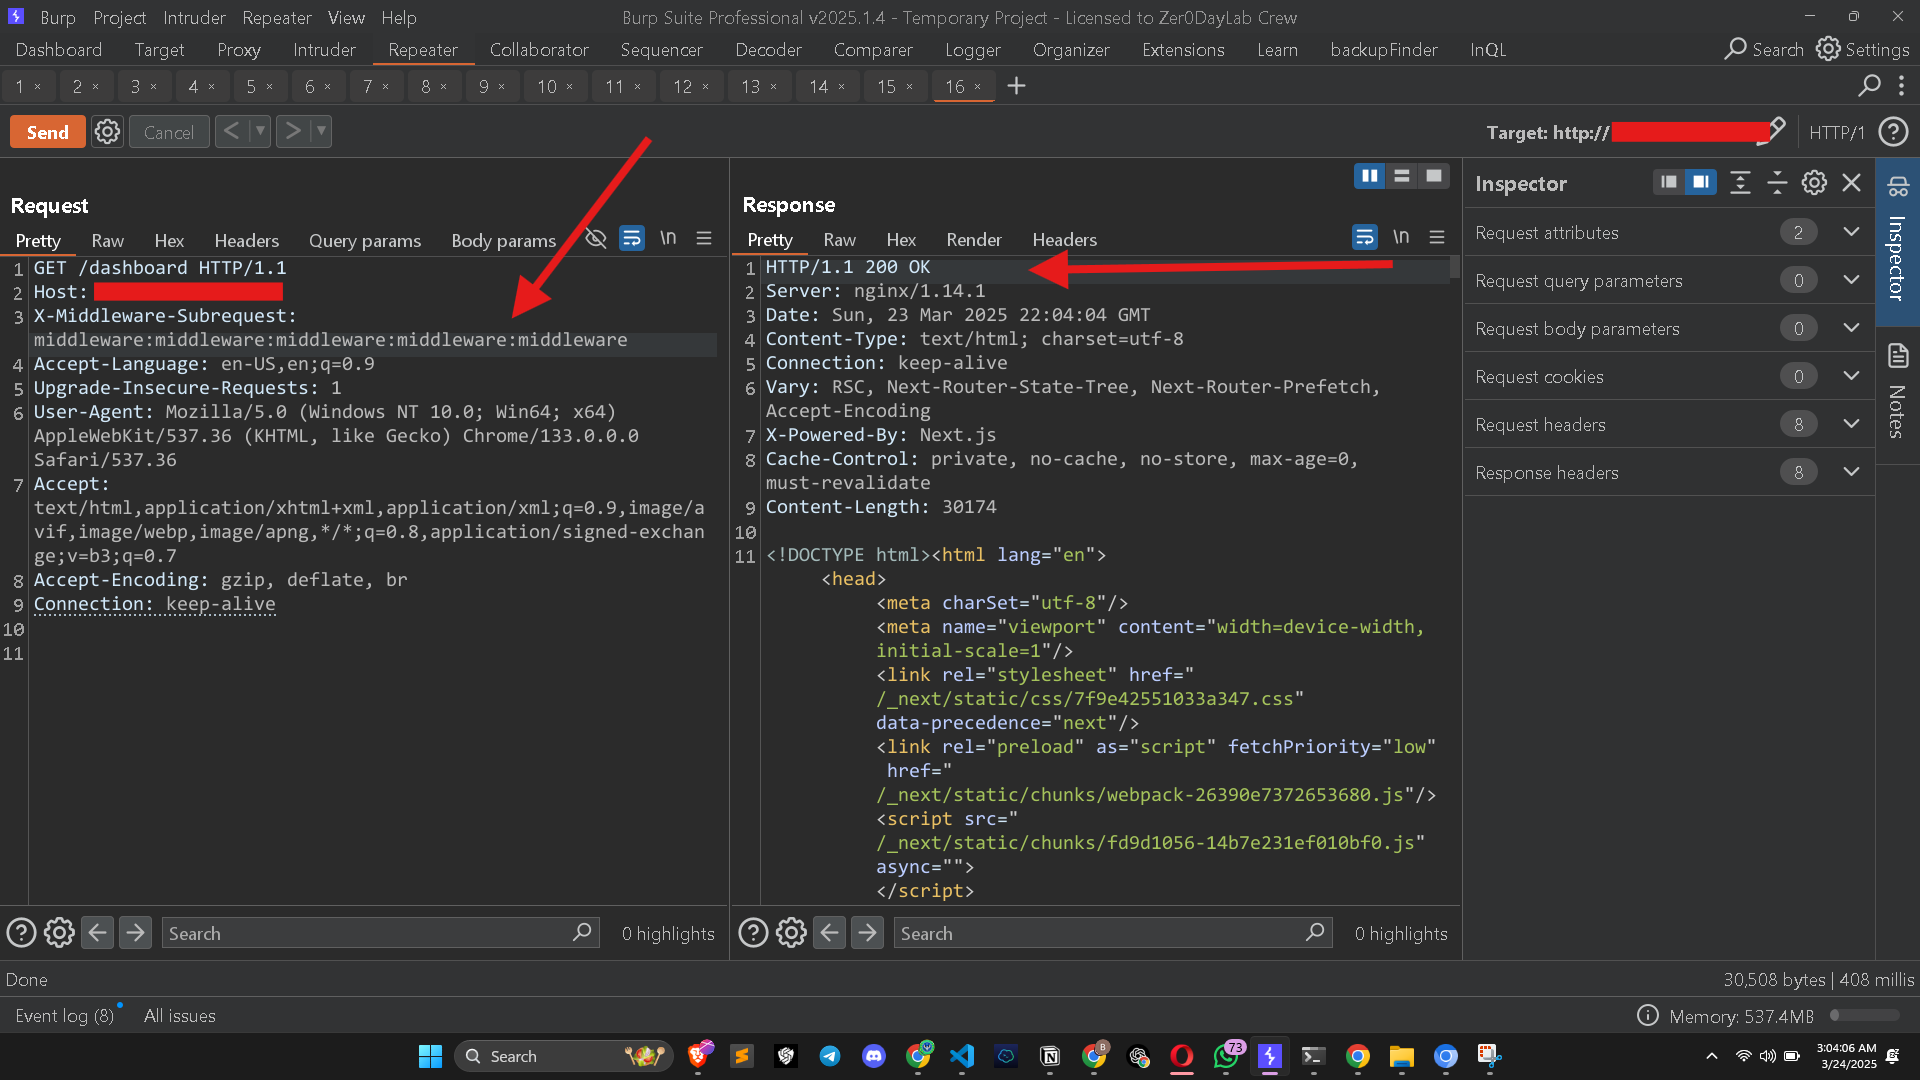
🚨 A Next.js middleware flaw can let unauthenticated attackers bypass authorization checks; CVE-2025-29927
PoC: https://github.com/alinaclark672377250/CVE-2025-29927-POC
The vulnerability affects applications that rely on Next.js middleware for access control. By abusing the x-middleware-subrequest header, an attacker can cause middleware checks to be skipped and potentially reach protected routes without authentication.
Next.js Middleware | Authorization Bypass:
• CVSS: 9.1 Critical • Attack: Remote, unauthenticated • Affected: Next.js 11.1.4–12.3.4, 13.x < 13.5.9, 14.x < 14.2.25, 15.x < 15.2.3 • Fixed: 12.3.5, 13.5.9, 14.2.25, 15.2.3 • Impact: Bypass of middleware-based authorization controls
The repository demonstrates the header-based bypass against a protected route.
🚨🇫🇷 FIC Expertise customer database allegedly leaked, 2,500 records exposed
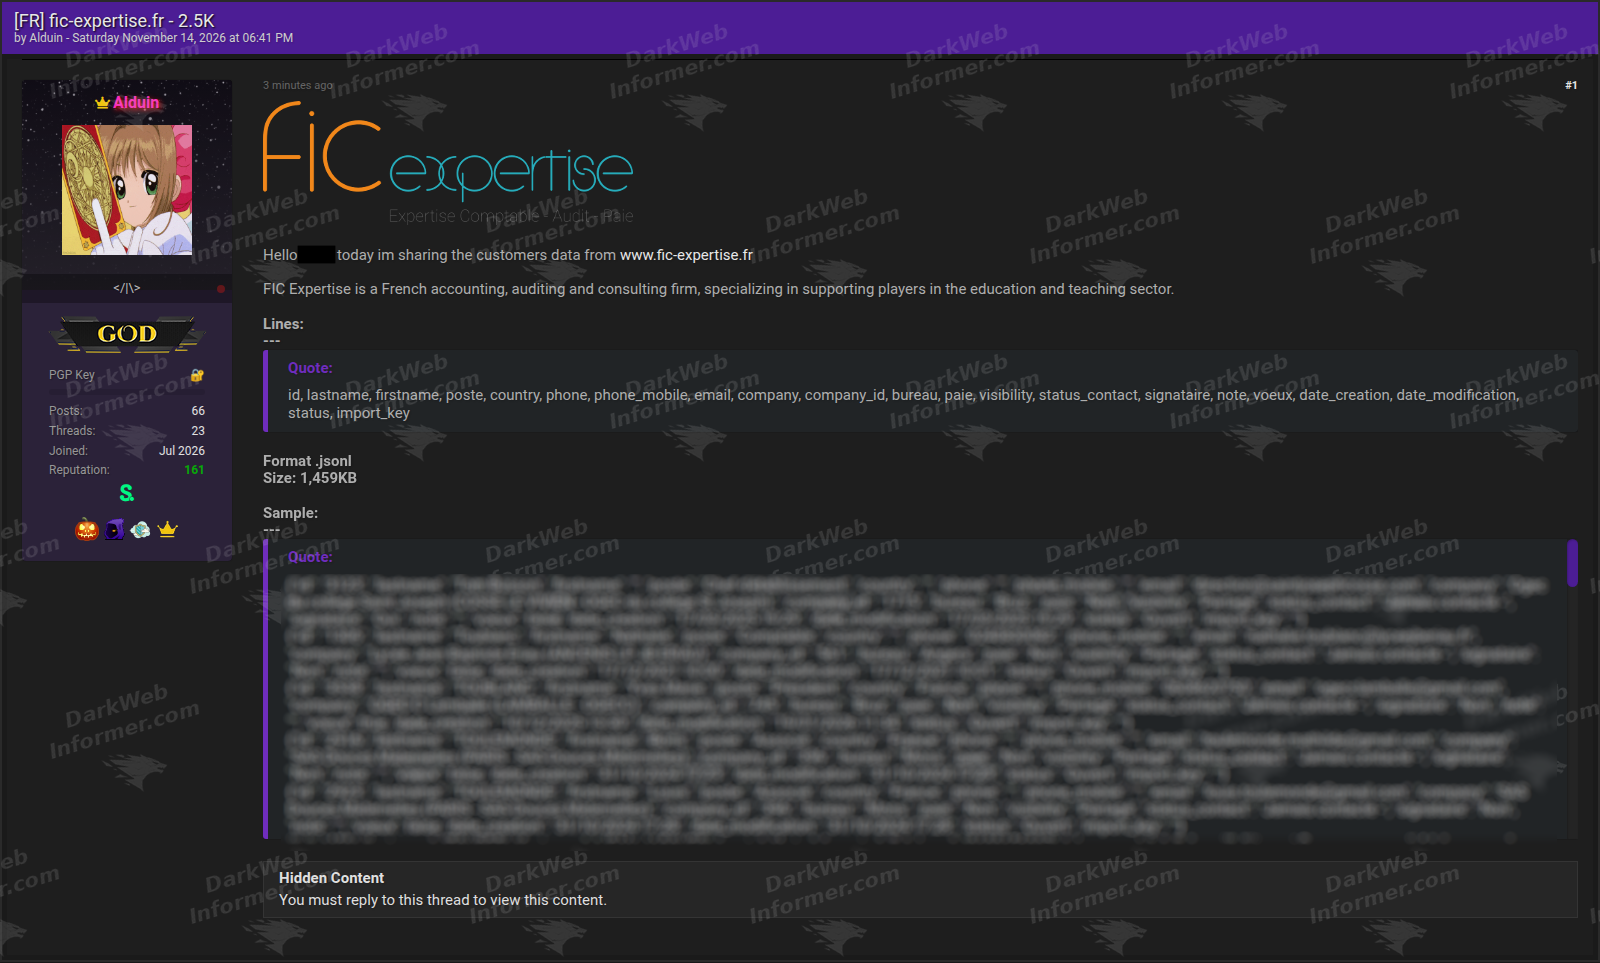
Threat actor "Alduin" claims to have leaked customer data from FIC Expertise, a French accounting, auditing, and consulting firm specializing in the education sector.
Victim: FIC Expertise Sector: Accounting / Consulting Actor: Alduin Records: Approximately 2,500
Data allegedly exposed:
• Customer names and contact information • Email addresses and phone numbers • Company names and organizational details • Job titles and office affiliations • Internal notes and customer contact statuses
The actor has published sample records, with the database advertised for download.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
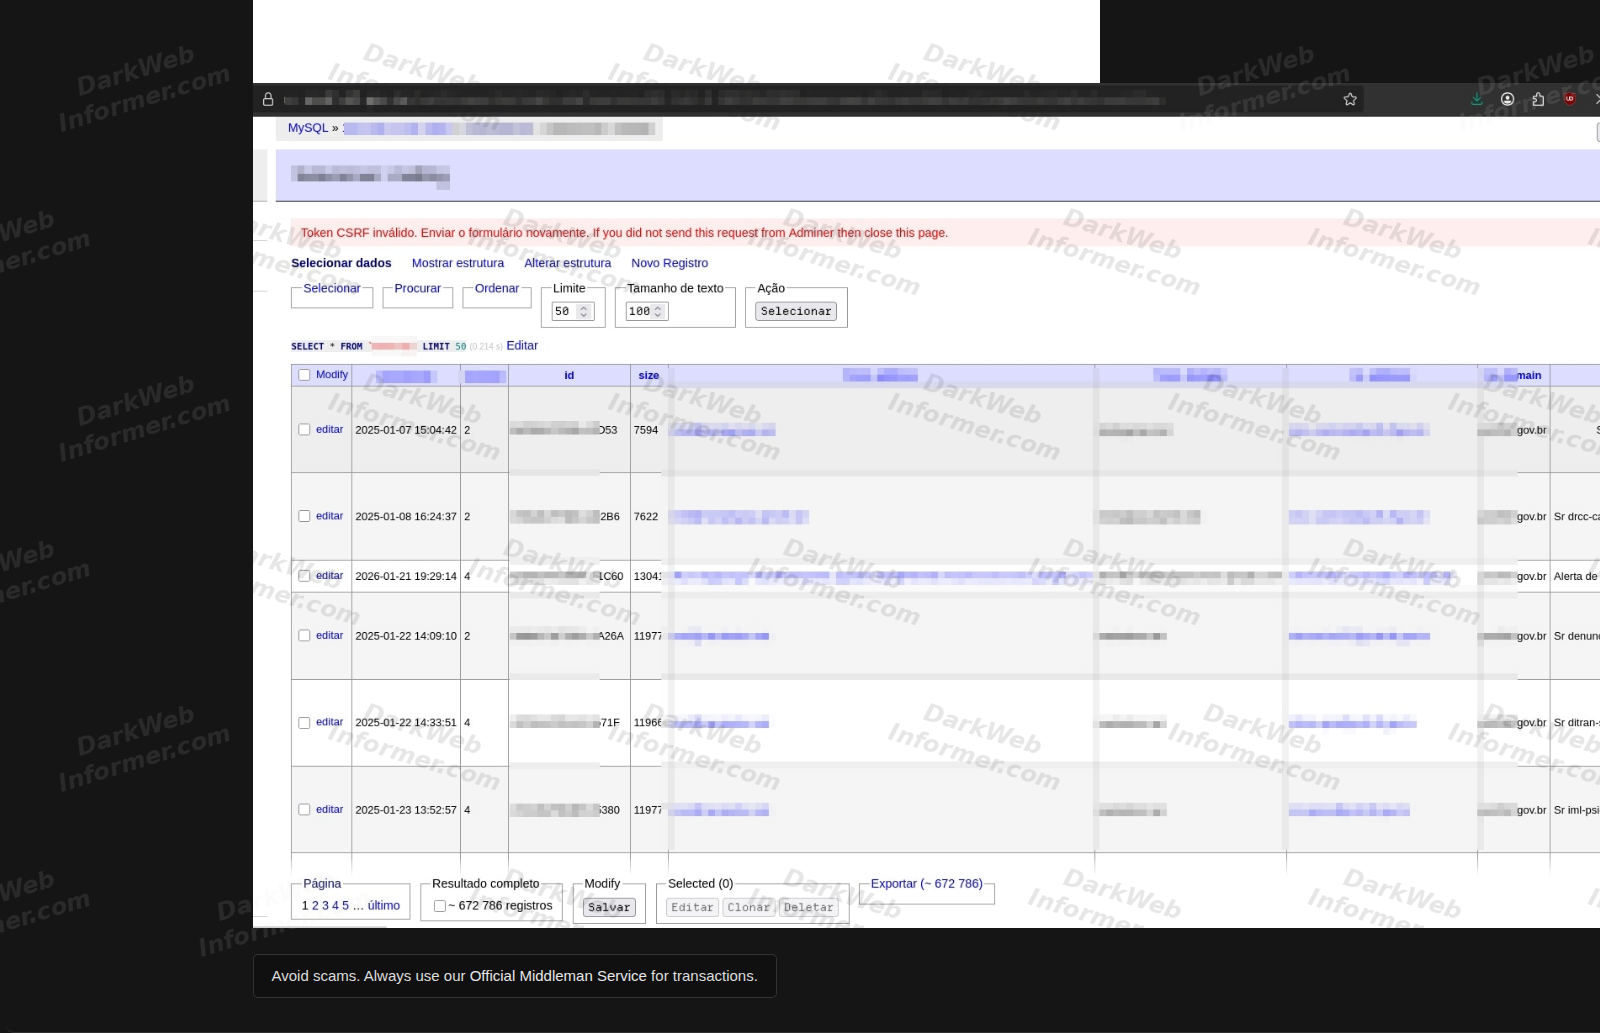
👀🚨🇧🇷 Brazilian Civil Police agency allegedly compromised, server access offered for $40,000
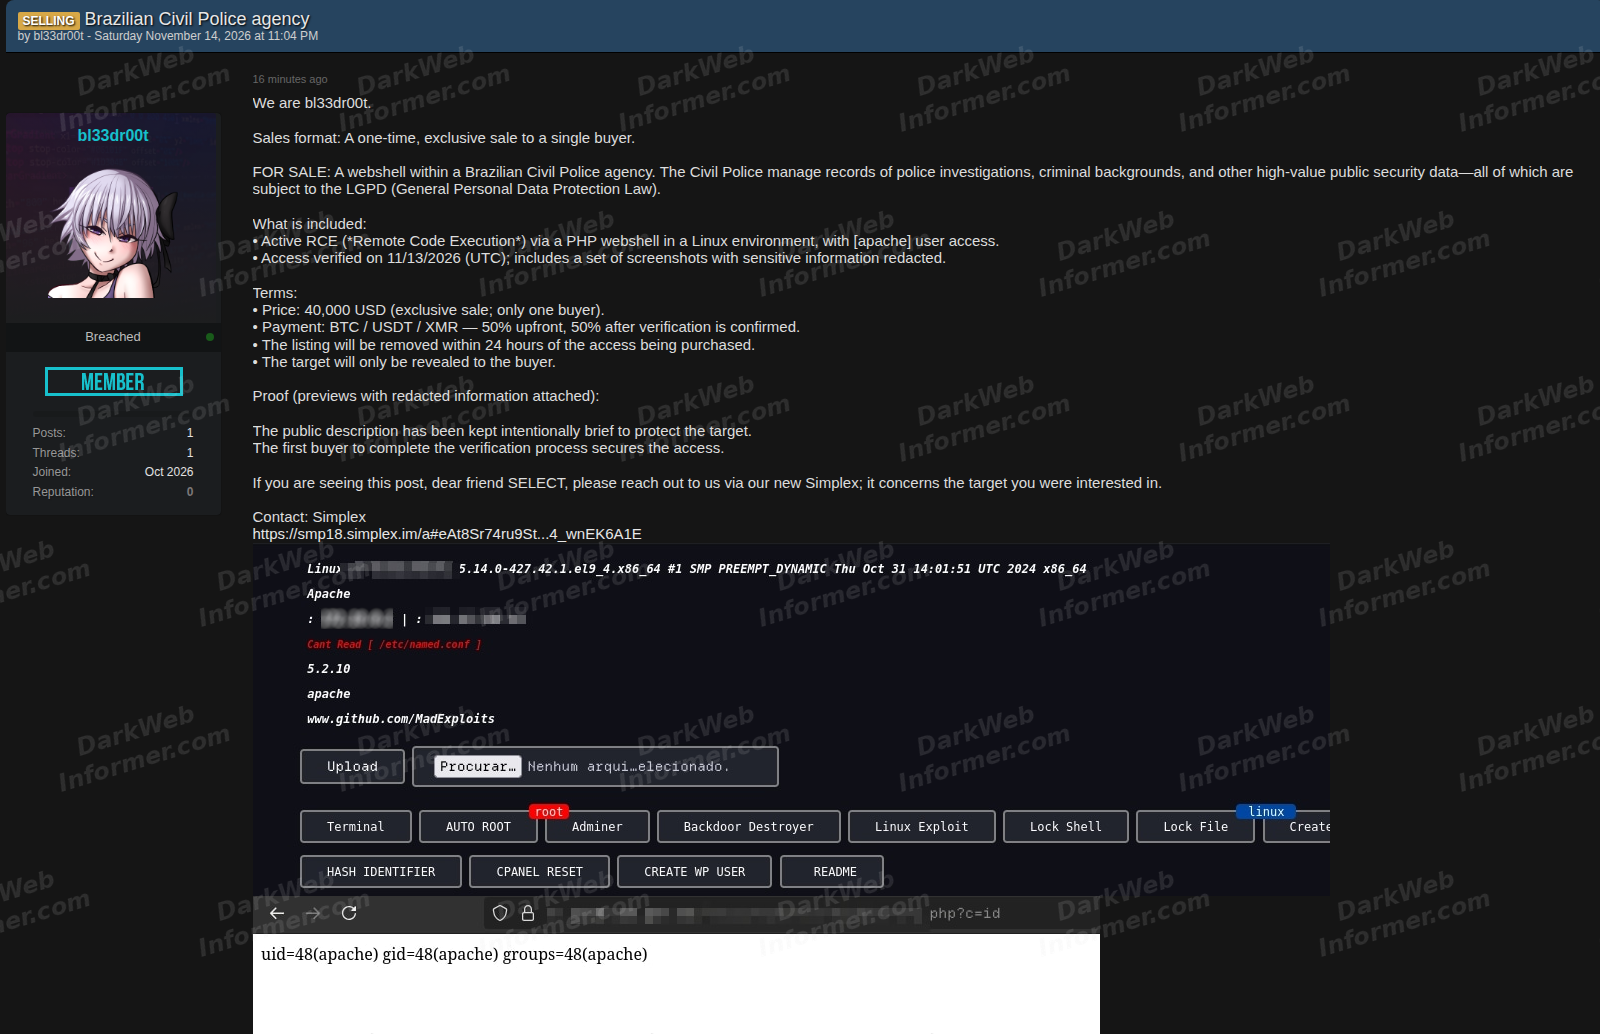
Threat actor "bl33dr00t" claims to have obtained remote code execution (RCE) access to an unidentified Brazilian Civil Police agency and is offering exclusive access to a single buyer.
Victim: Unidentified Brazilian Civil Police agency Sector: Law Enforcement / Government Actor: bl33dr00t Price: $40,000 Status: Unverified
Access allegedly includes:
• Active PHP webshell on a Linux server • Remote code execution under the Apache user • Access to internal systems and databases • Potential exposure of criminal investigation records
The actor has published redacted screenshots showing webshell access and a database containing approximately 672,786 records.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
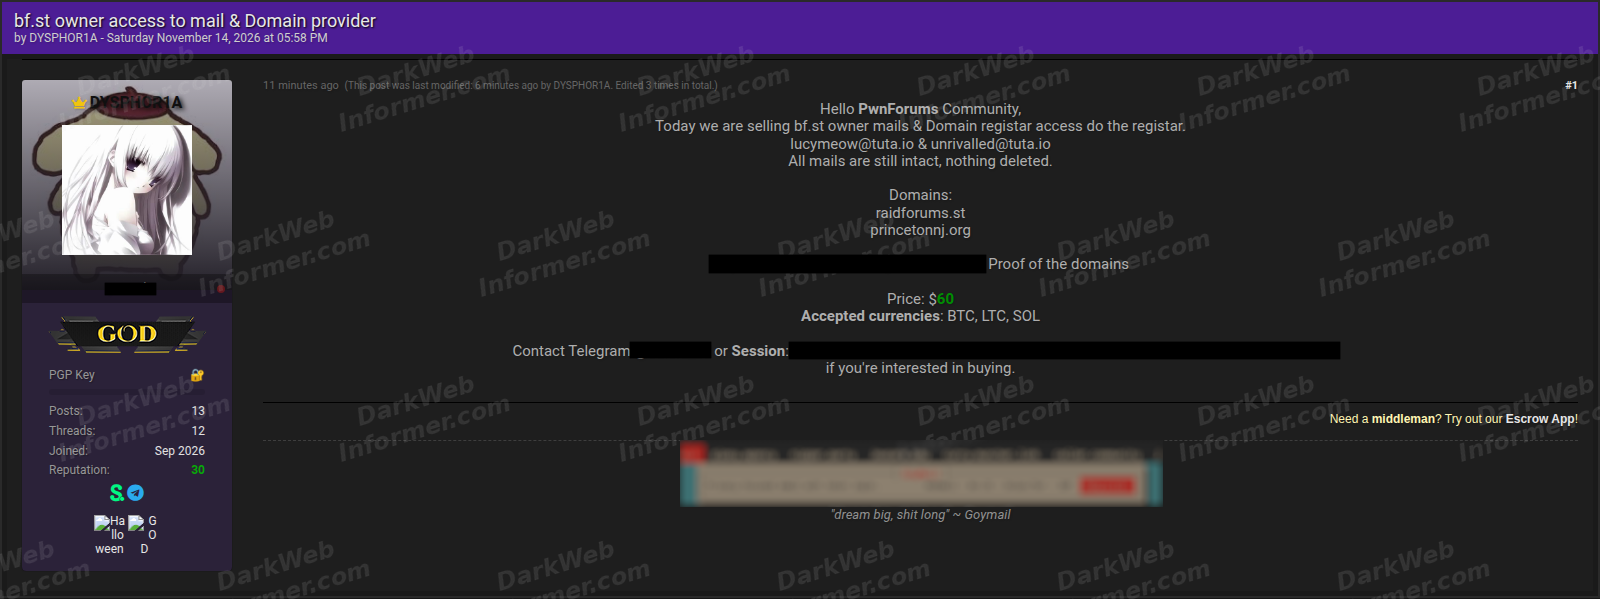
🚨 Alleged access to bf[.]st owner's email and domain registrar accounts offered for $60
Threat actor "DYSPHOR1A" is selling alleged access to email accounts and domain registrar services associated with the owner of bf[.]st.
Target: bf[.]st owner Actor: DYSPHOR1A Price: $60 Status: Unverified
Access allegedly includes:
• Owner's email accounts • Domain registrar access • Domains raidforums[.]st and princetonnj[.]org • Existing mailbox contents
The actor claims all emails remain intact and has published screenshots as proof of access. Payments are accepted in BTC, LTC, and SOL.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
⚠️ Sehranin: A minimalist, fast, and zero-knowledge encrypted file sharing service built with age; https://github.com/filosottile/age.
Dark Web: http://sehranindi5jrlhzoudwaldfmodaba4er4nfuppua2y5ls4l227urgyd[.]onion
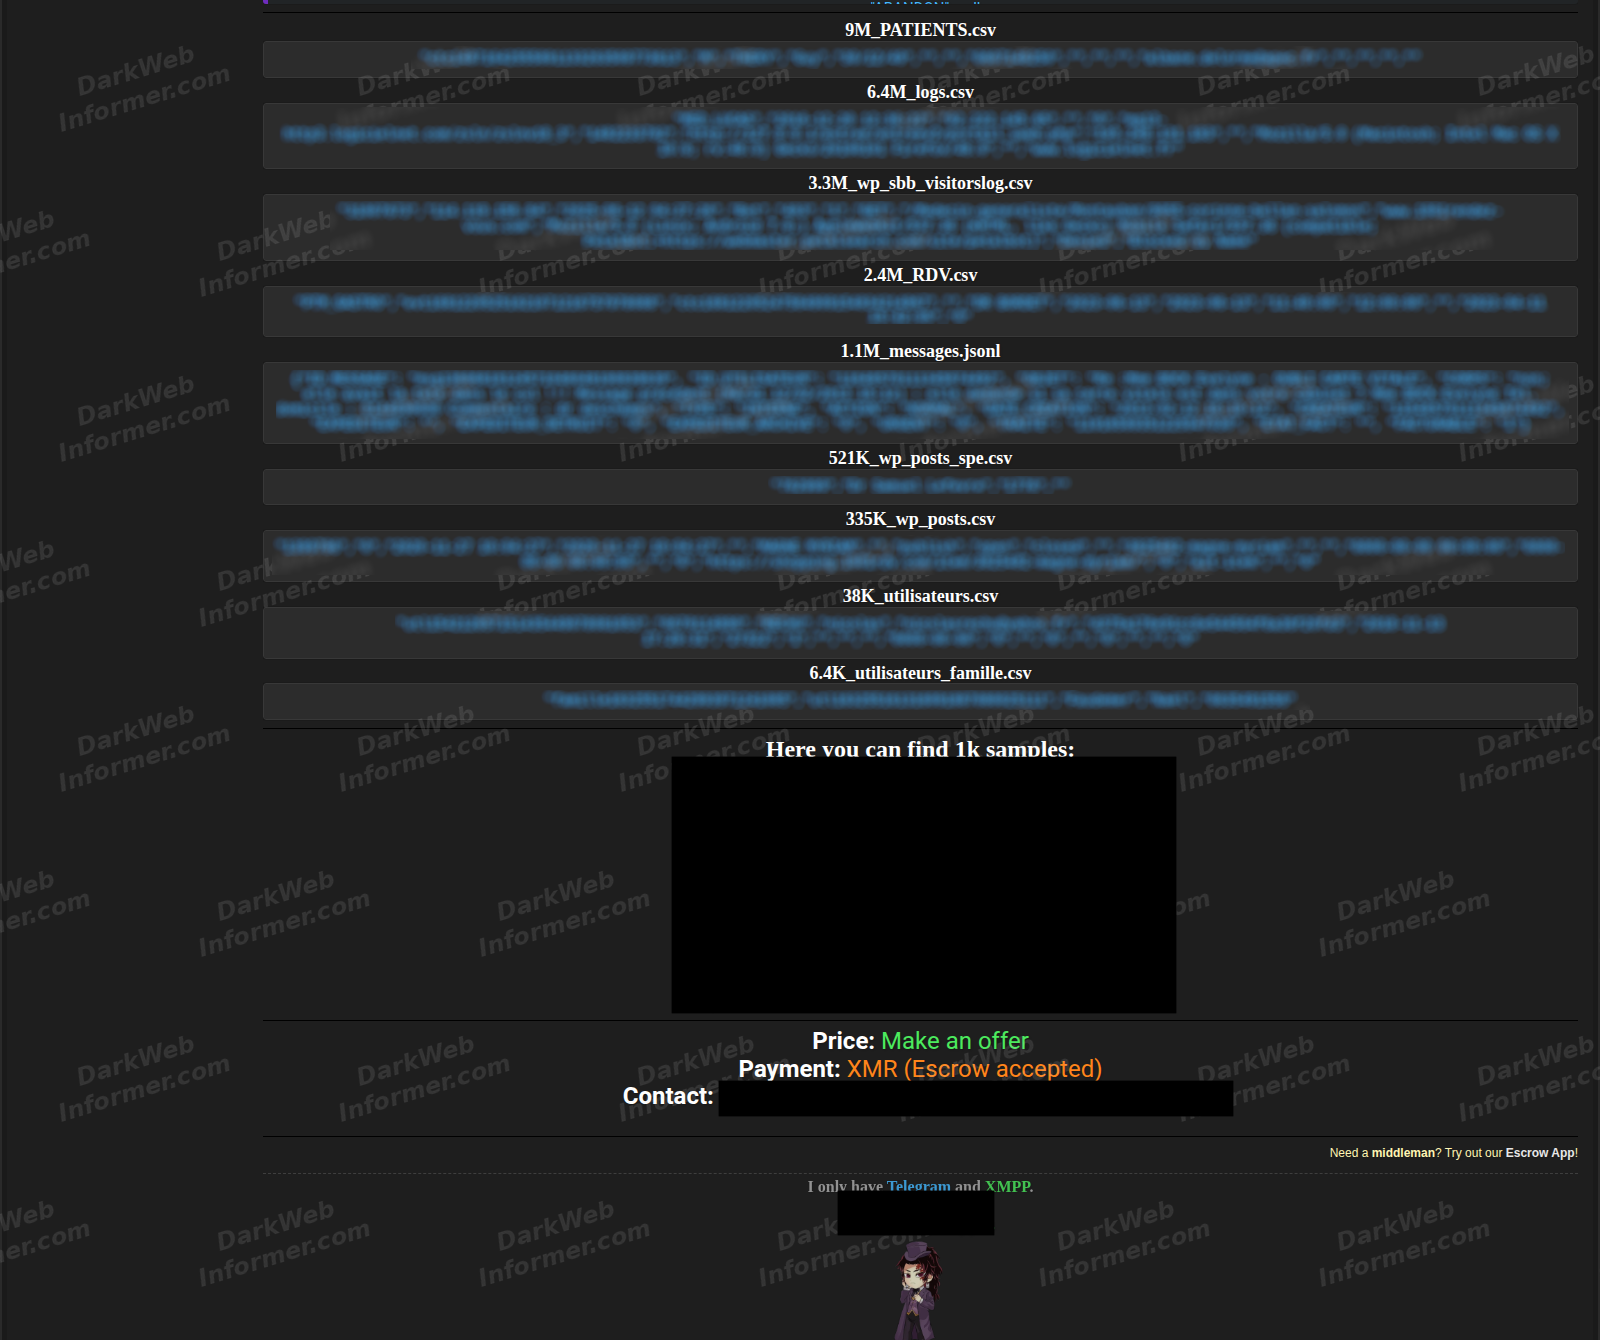
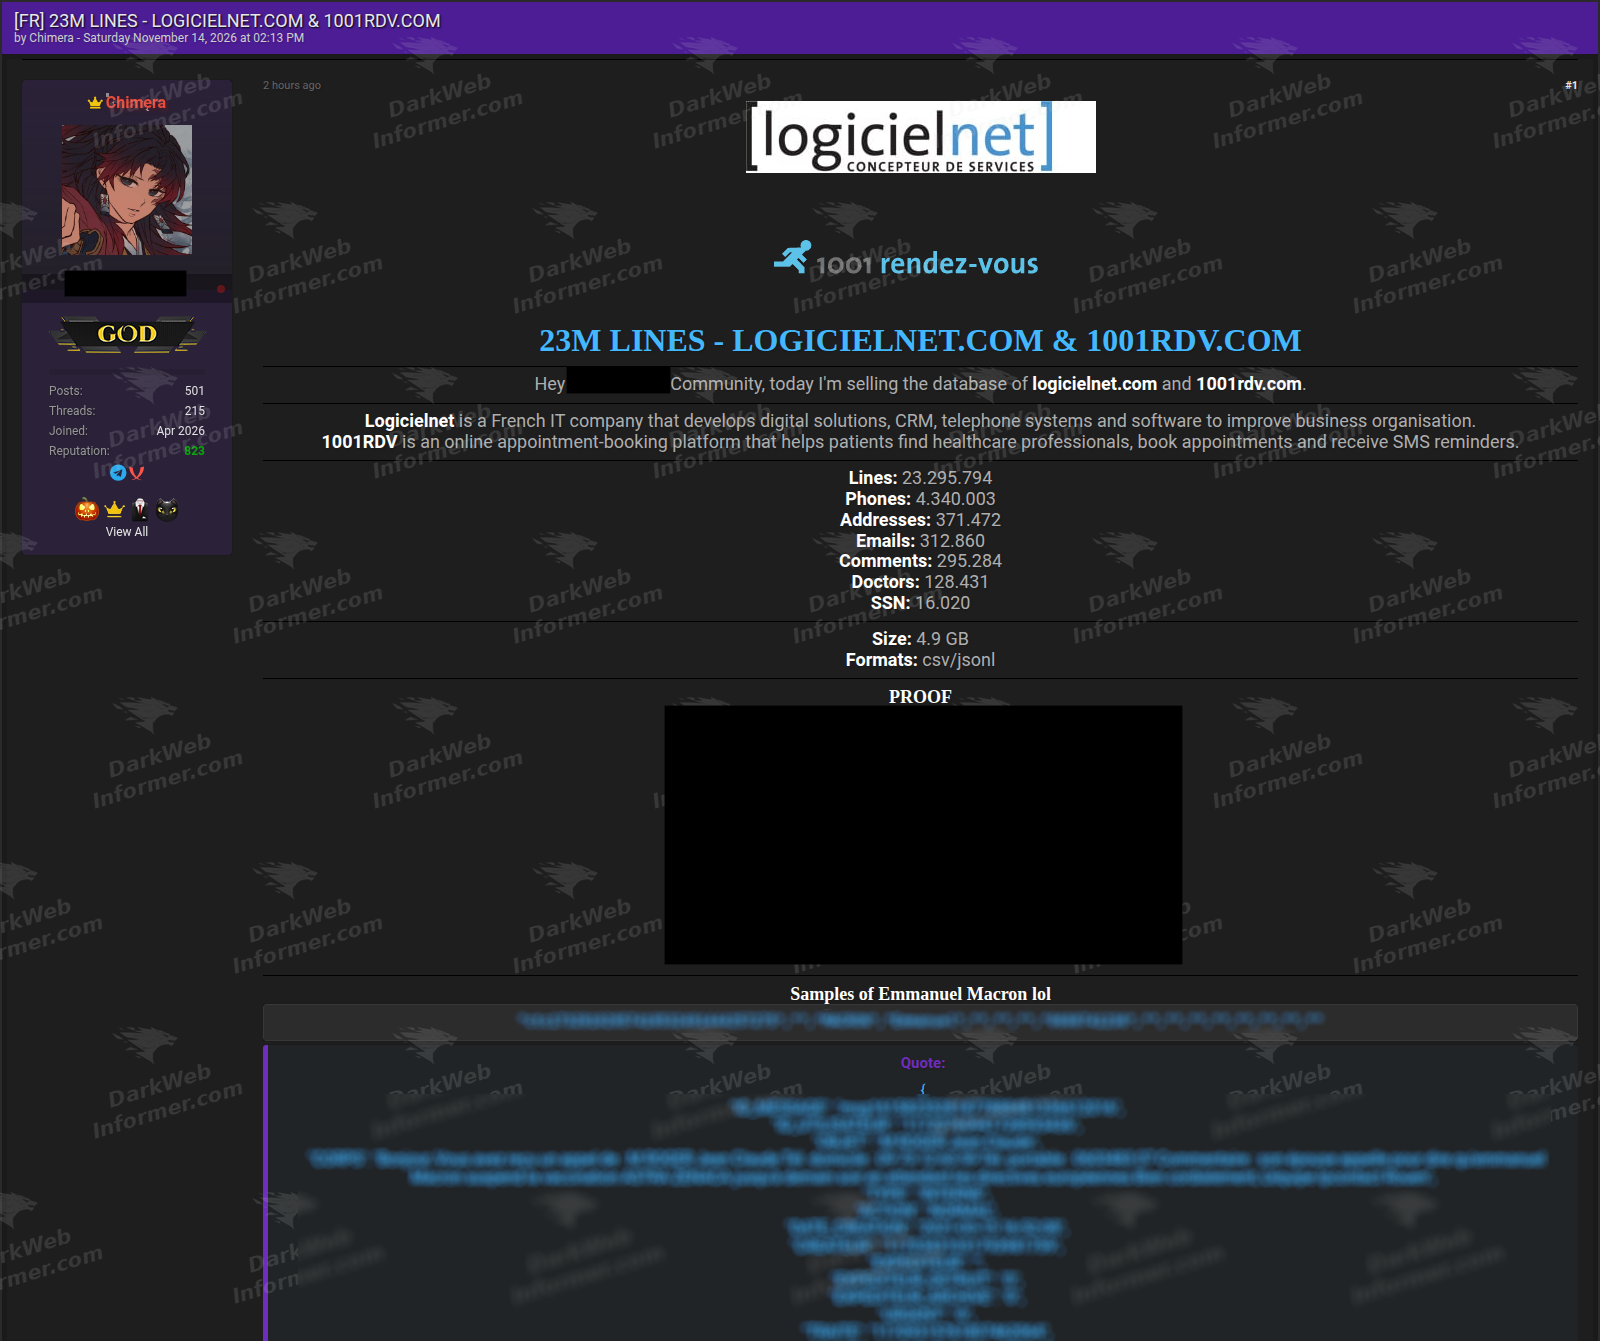
🚨🇫🇷 Logicielnet and 1001 Rendez-Vous allegedly breached, 23.3 million records exposed
Threat actor "Chimera" claims to have obtained 4.9 GB of data from Logicielnet, a French IT company, and 1001 Rendez-Vous, a medical appointment booking platform.
Victims: Logicielnet / 1001 Rendez-Vous Sector: IT / Healthcare Technology Actor: Chimera Records: 23.3M entries | 4.3M phone numbers Status: Unverified
Data allegedly exposed:
• Patient names and contact information • Medical appointment records • Email addresses and physical addresses • Patient messages and communications • Healthcare professional information • Booking histories and system logs
The actor has published 1,000 sample records and is accepting offers for the complete dataset.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
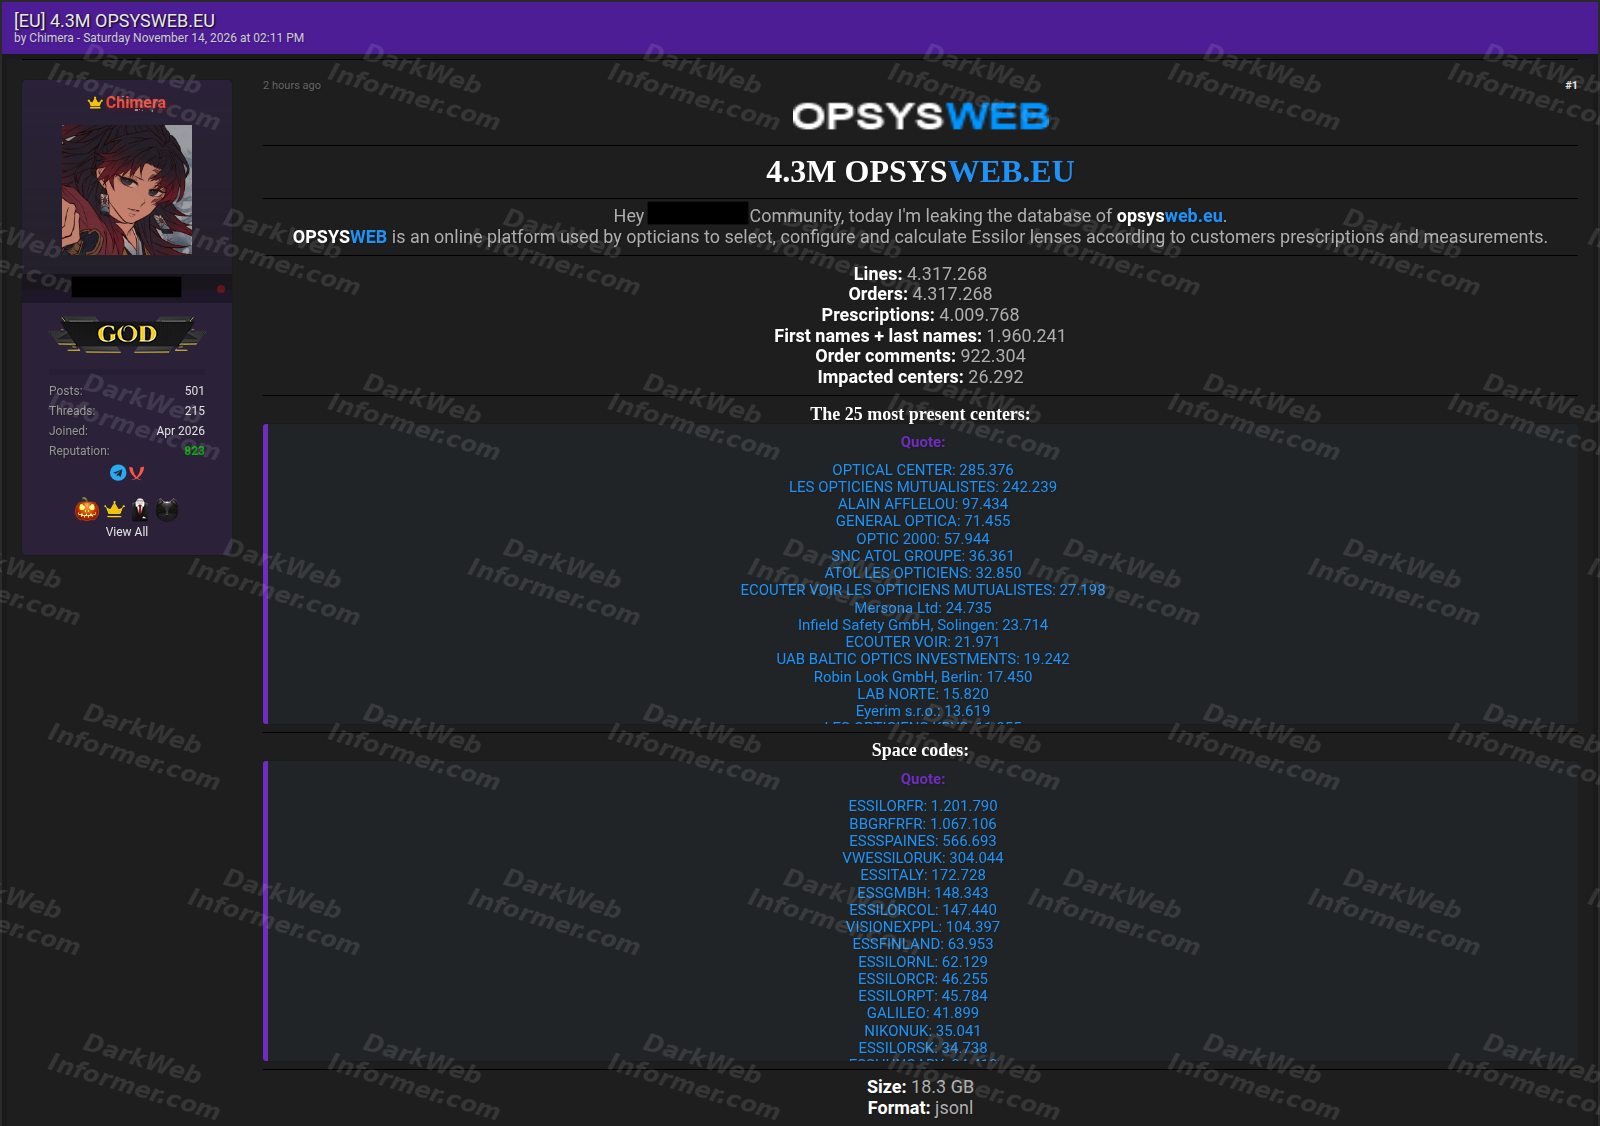
🚨🇪🇺 OPSYSWEB allegedly breached, 4.3 million records exposed
Threat actor "Chimera" claims to have leaked an 18.3 GB database from OPSYSWEB, an optical software platform used by opticians to manage Essilor lens orders and prescriptions.
Victim: OPSYSWEB Sector: Optical / Healthcare Technology Actor: Chimera Records: 4.3M orders | 4M prescriptions Status: Unverified
Data allegedly exposed:
• Patient names and prescription details • Lens measurements and configurations • Order histories and customer comments • Data linked to 26,292 optical centers
The actor has published database samples, with the files reportedly containing nearly 2 million name records.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
‼️🇰🇷🇺🇸🇺🇸🇺🇸 n0n ransomware names four major consumer brands in new leak-site listings.
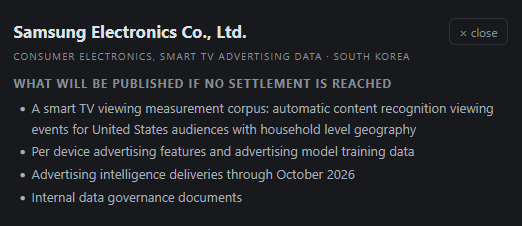
🇰🇷 Samsung Electronics - A South Korean technology company producing smartphones, televisions, appliances, semiconductors, and other consumer electronics.
The listing threatens to publish smart TV viewing measurement data for U.S. audiences, device advertising features and model-training data, advertising intelligence through October 2026, and internal data-governance documents.
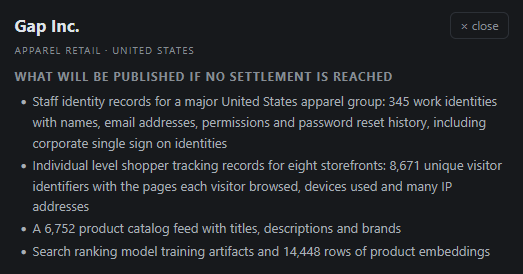
🇺🇸 Gap Inc. - A U.S. apparel retailer operating brands including Gap, Old Navy, Banana Republic, and Athleta.
The listing claims 345 staff identity records, 8,671 unique shopper identifiers tied to page visits, devices and IP addresses, a 6,752-product catalog feed, and 14,448 rows of product embeddings and search-ranking data.
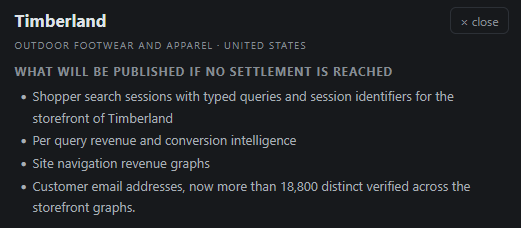
🇺🇸 Timberland - A U.S. footwear and apparel brand known for outdoor boots, clothing, and accessories.
The listing claims shopper search sessions, typed queries, session identifiers, revenue and conversion intelligence, site-navigation revenue graphs, and more than 18,800 verified customer email addresses.
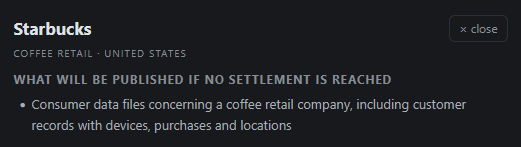
🇺🇸 Starbucks - A U.S.-based global coffeehouse chain.
The listing claims consumer data containing customer records tied to devices, purchases, and locations.
Claim is currently unverified.
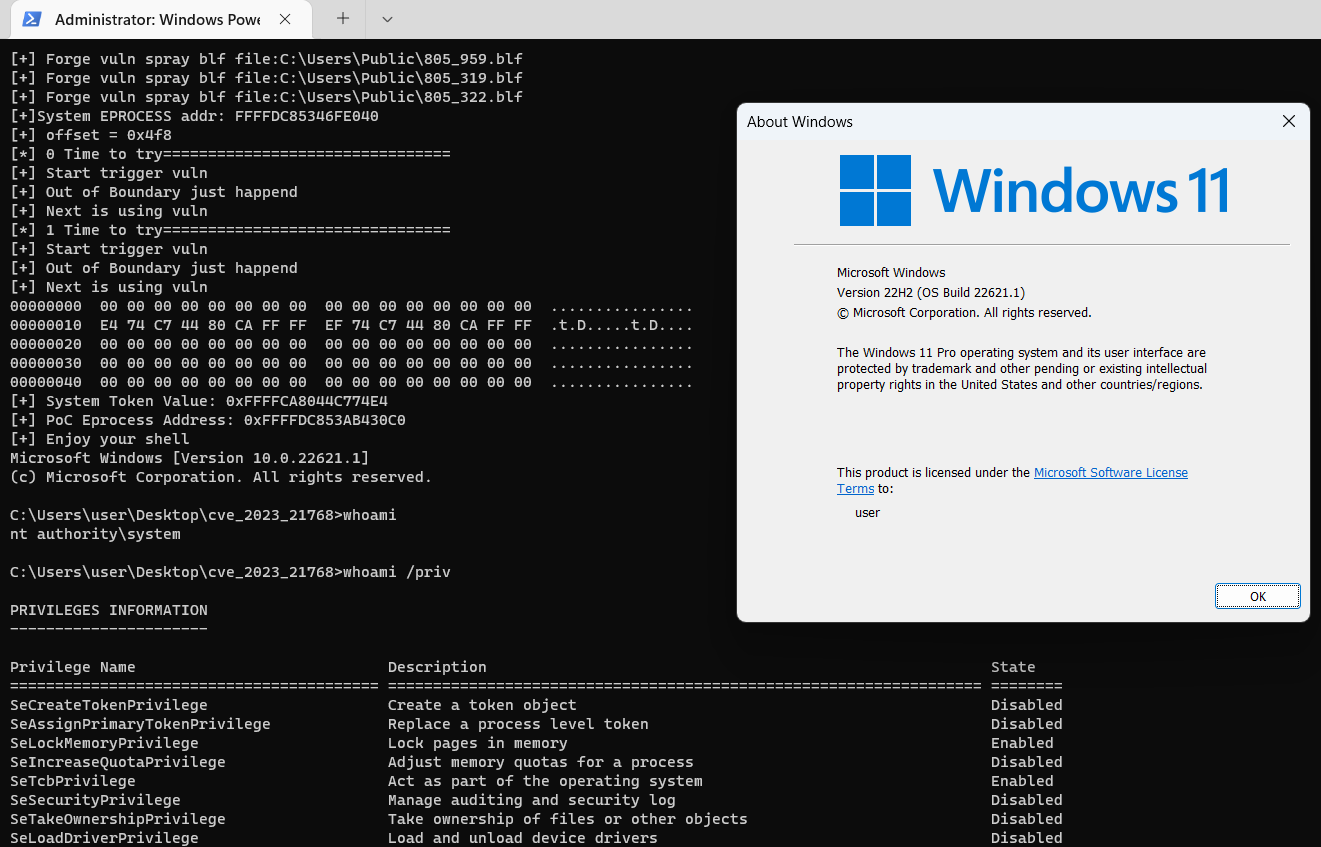
🚨 A Windows Common Log File System flaw can let a local attacker escalate privileges to SYSTEM; CVE-2023-28252
PoC: https://github.com/Joe1sn/CVE_2023_28252
The vulnerability is a heap-based buffer overflow in the Windows CLFS driver. Successful exploitation can allow a local attacker to elevate privileges and execute code with SYSTEM-level permissions.
Microsoft patched the flaw in April 2023, and CISA added it to the Known Exploited Vulnerabilities catalog the same day.
Windows CLFS | Local Privilege Escalation:
• CVSS: 7.8 High • Attack: Local • Impact: Privilege escalation to SYSTEM • CWE: CWE-122 Heap-based Buffer Overflow • Status: Actively exploited in the wild / patched by Microsoft
The PoC demonstrates exploitation of the vulnerable CLFS driver on affected Windows systems.
Reddit's Most Disturbing Confessions
Video Credit: youtube.com/@VisualVenture

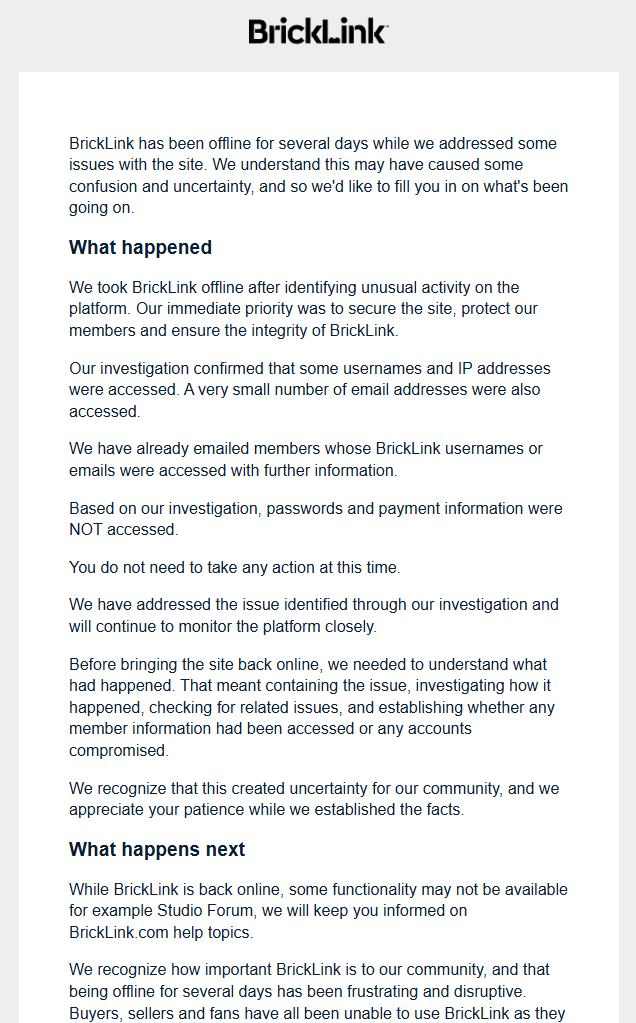
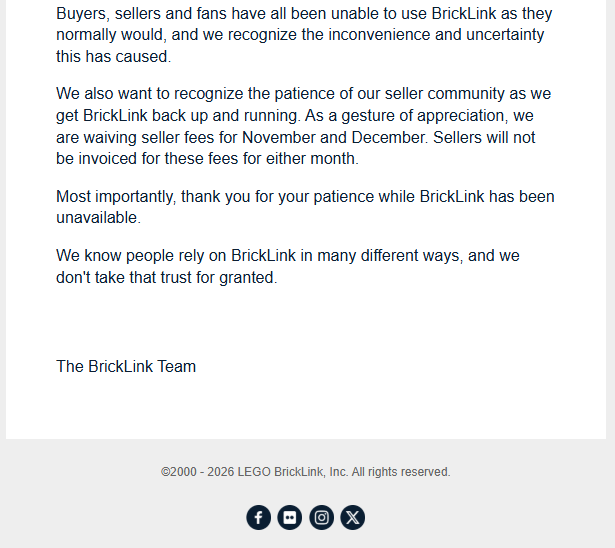
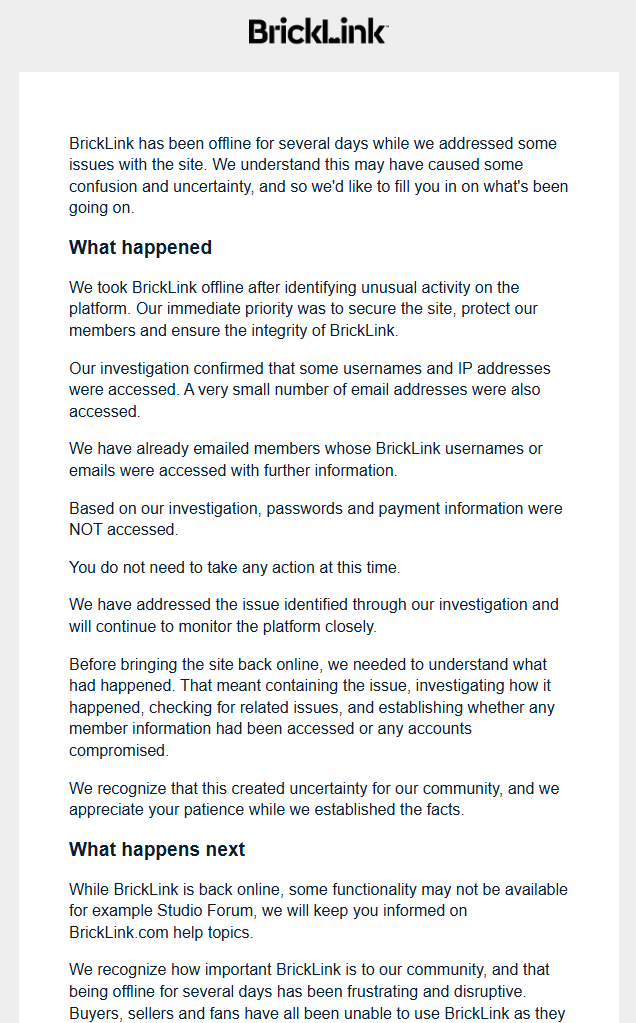
🚨 BrickLink confirms data breach after several days offline
BrickLink says some usernames and IP addresses were accessed, along with a very small number of email addresses.
According to the company, passwords and payment information were not accessed, and affected members have been emailed.
The site is back online with some features still unavailable. Seller fees for November and December are being waived.
🚨 BrickLink confirms data breach after several days offline
BrickLink says some usernames and IP addresses were accessed, along with a very small number of email addresses.
According to the company, passwords and payment information were not accessed, and affected members have been emailed.
The site is back online with some features still unavailable. Seller fees for November and December are being waived.
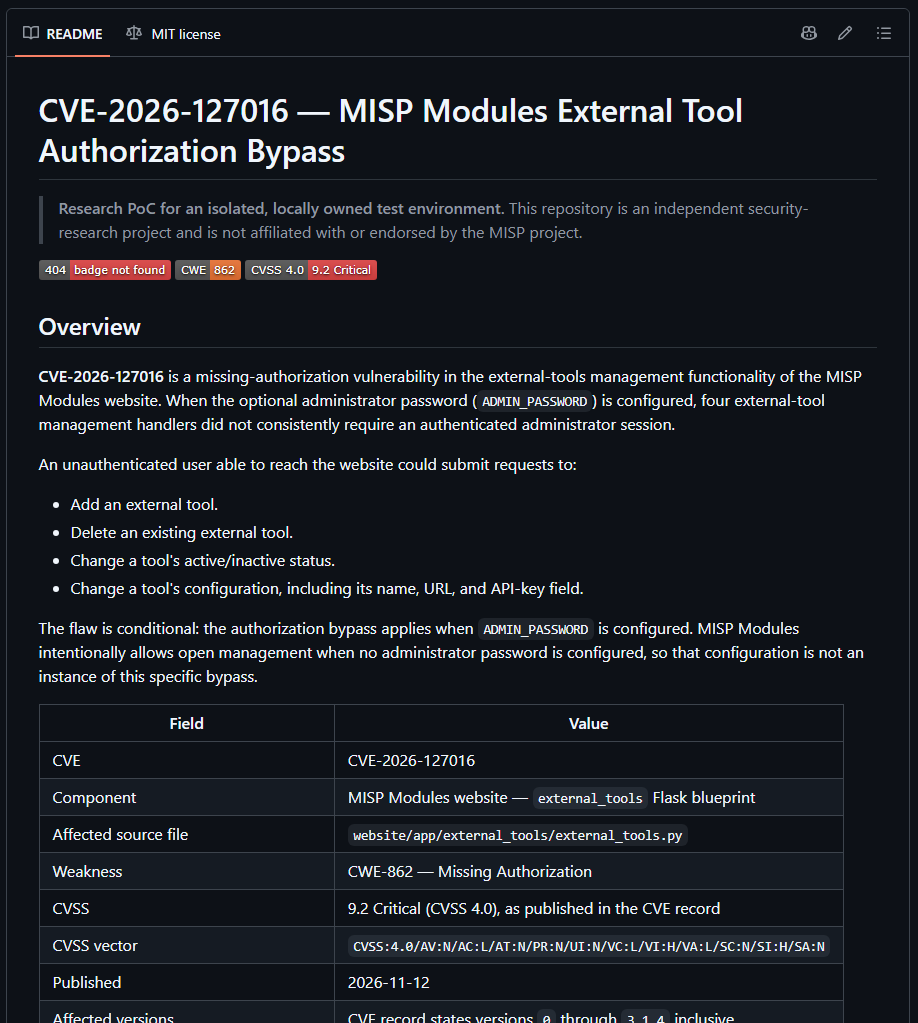
🚨 A critical MISP Modules authorization flaw can let unauthenticated attackers modify external tool configurations; CVE-2026-127016
PoC: https://github.com/fumioryoto/CVE-2026-127016
The vulnerability affects the MISP Modules website component, where external tool management endpoints fail to enforce the configured administrator authentication policy.
An unauthenticated attacker with network access can add or remove tools, toggle their status, and modify settings including API keys and ingestion URLs.
MISP Modules | Missing Authorization:
• CVSS: 9.2 Critical • Affected: MISP Modules ≤ 3.1.4 • Attack: Remote, unauthenticated • Impact: External tool configuration tampering, API key changes, ingestion URL modification • CWE: CWE-862 Missing Authorization
The issue only applies when ADMIN_PASSWORD is configured; installations without an admin password intentionally allow open management access.
🚨🇺🇸 Routine FAA equipment upgrade blamed for nationwide flight shutdown, over 11,000 flights canceled
U.S. Transportation Secretary Sean Duffy says Friday's nationwide ground stop was triggered by routine maintenance involving an upgrade from copper wiring to fiber-optic cable by FAA contractor L3Harris.
Following the upgrade, a router reportedly overloaded critical air traffic control communication systems, forcing the FAA to ground flights nationwide for more than four hours.
More than 8,200 flights were canceled Friday, with at least another 3,000 canceled Saturday. Officials are investigating whether the failure resulted from installation errors or faulty equipment.
The FAA says there is no evidence of a cyberattack or AI-related involvement.
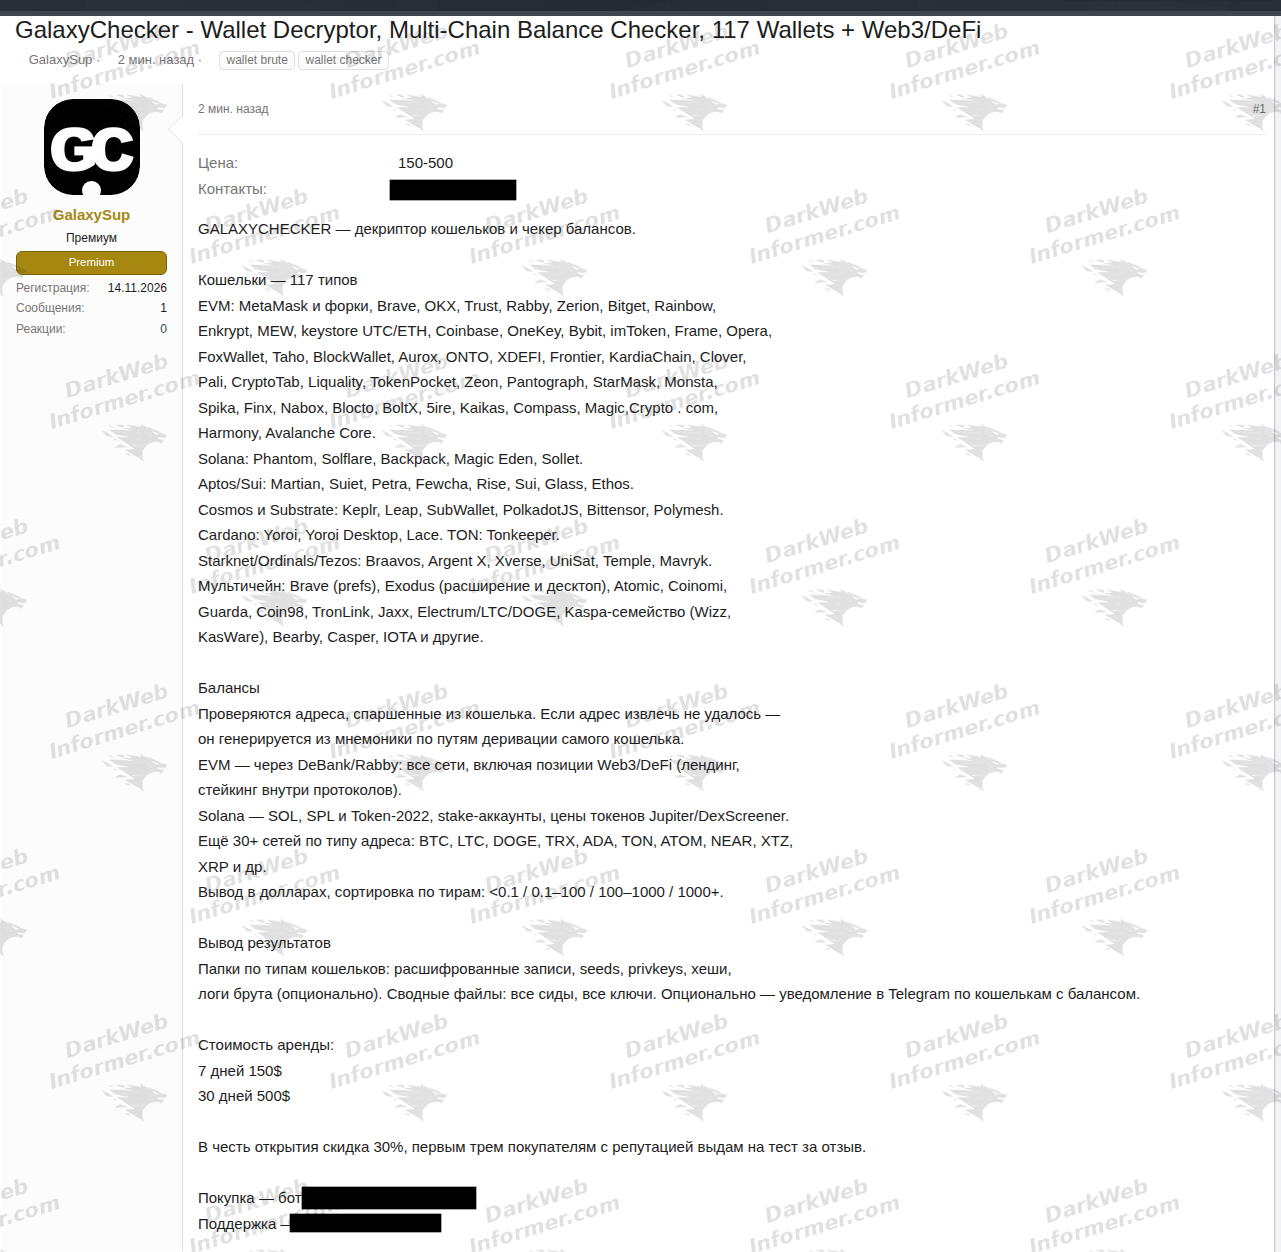
🚨 GalaxyChecker advertised as cryptocurrency wallet decryptor supporting 117 wallet types and multi-chain balance scanning
An actor known as "GalaxySup" is selling access to GalaxyChecker, a tool designed to decrypt cryptocurrency wallet data and identify wallets holding digital assets.
The advertised capabilities include:
• Support for MetaMask, Trust Wallet, Phantom, Exodus, and other wallets • Wallet decryption and seed phrase extraction • Balance scanning across EVM, Solana, Bitcoin, and 30+ networks • Web3/DeFi holdings, staking, and lending position checks • Export of recovered private keys and seed phrases • Telegram alerts for wallets containing funds
Access is advertised at $150 for seven days or $500 for 30 days.
The tool's capabilities have not been independently verified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
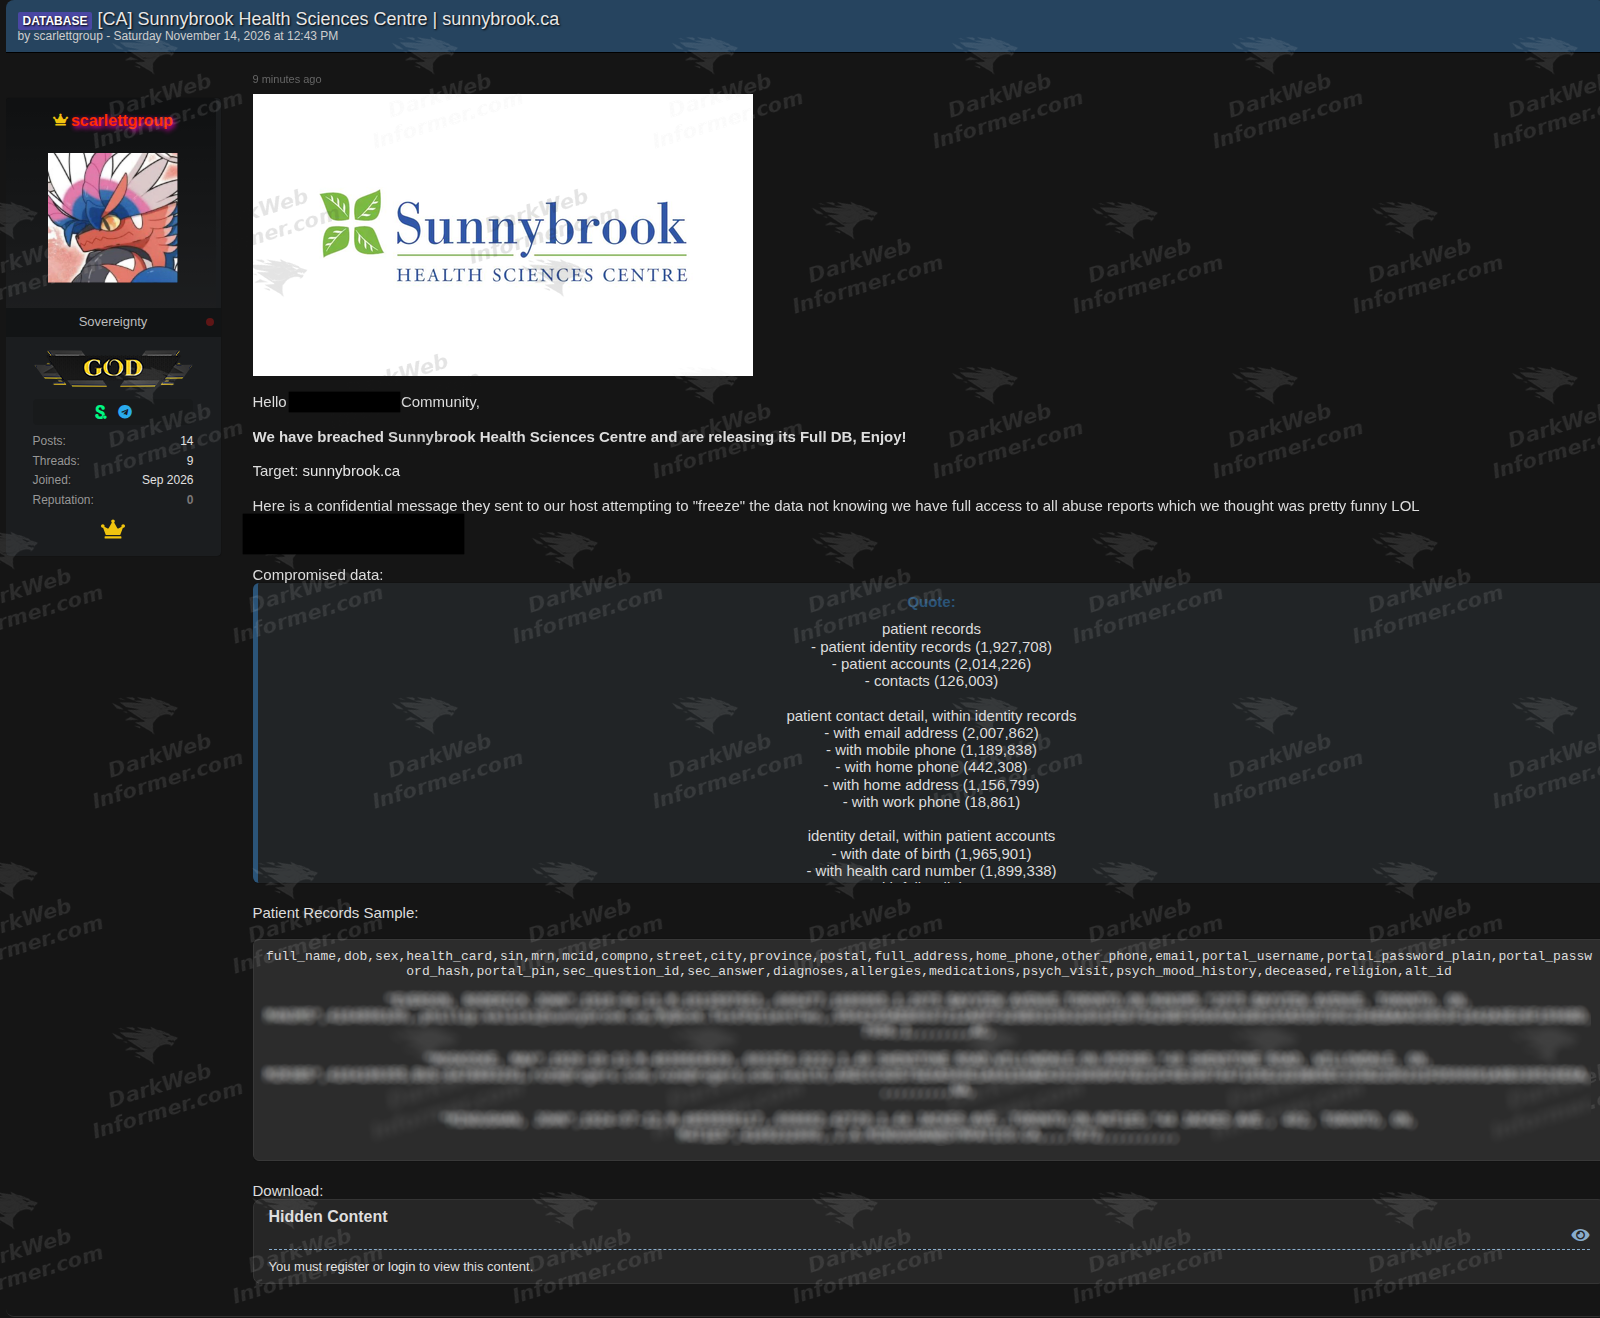
🚨🇨🇦 Sunnybrook Health Sciences Centre allegedly breached, nearly 2 million patient records exposed
The actor "scarlettgroup" claims to have compromised Sunnybrook Health Sciences Centre, a major hospital in Toronto, Canada, and released its patient database.
The advertised data includes:
• 1,927,708 patient identity records • Over 2 million patient account entries • Names, dates of birth, and contact information • Health card and Social Insurance Numbers (SIN) • Medical diagnoses, allergies, and patient portal credentials
The actor has published sample records and claims to have access to internal communications concerning the alleged breach.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
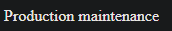
Top 5 forum PwnForums is currently showing a "Production maintenance" message when visiting their clearnet and onion site.
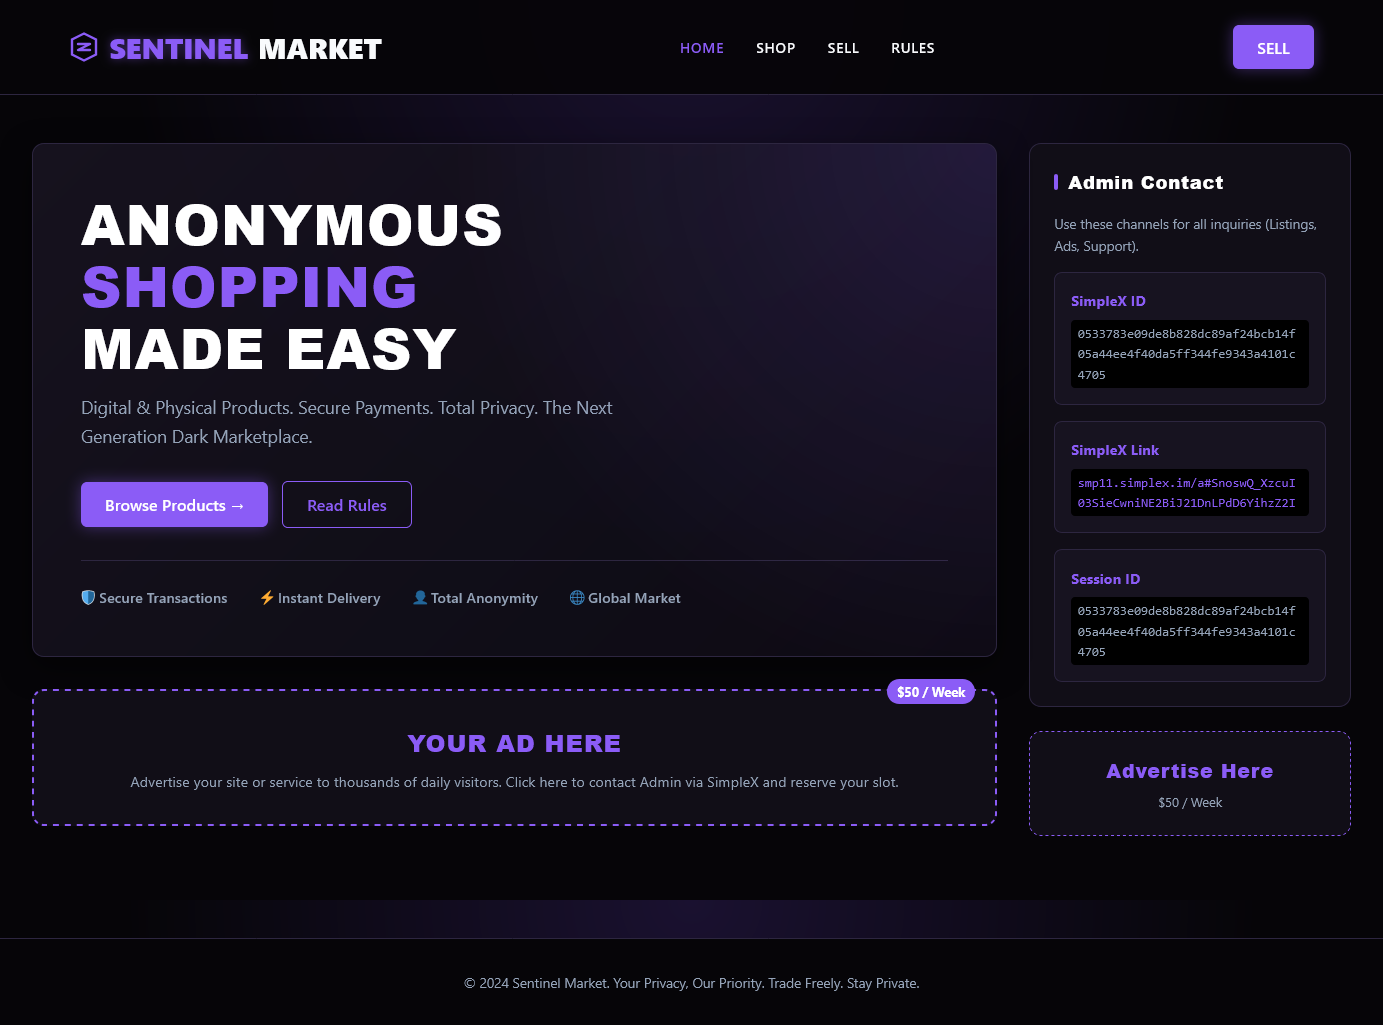
⚠️ New Darknet Market: Sentinel Market
Dark Web: http://lofd6lahoimt5mubrbvpzdbihh5gh3233qpk3j3nou77n272i7beykid[.]onion
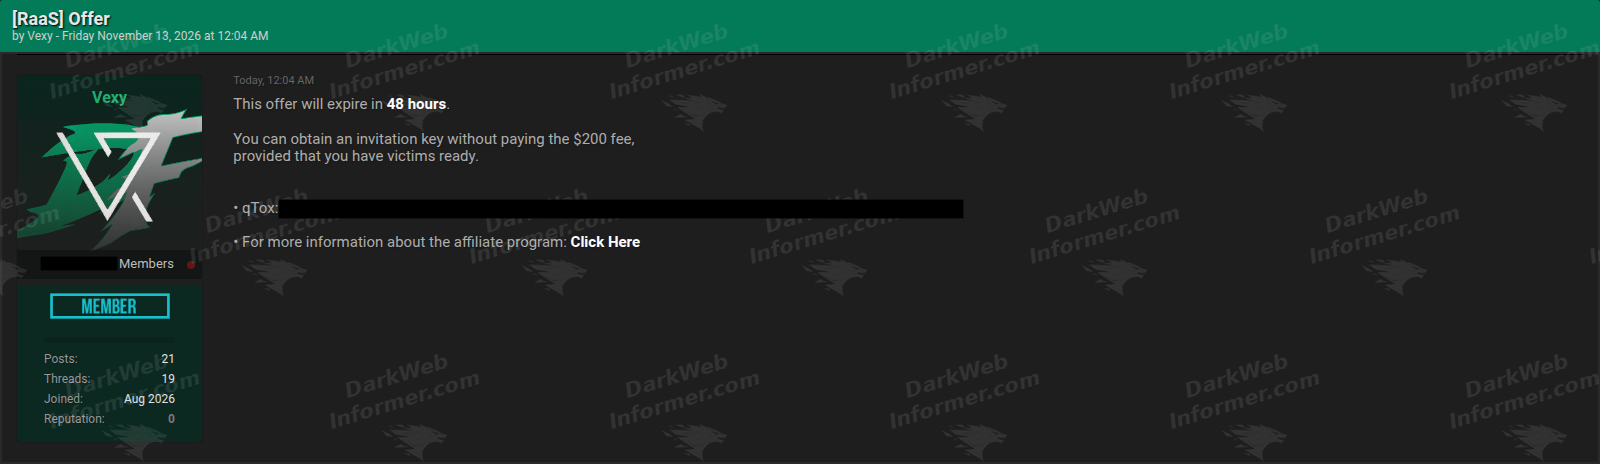
🚨 Vexy ransomware waives $200 affiliate fee for operators with victims ready
The Vexy ransomware-as-a-service (RaaS) operation has announced a limited 48-hour recruitment offer, allowing new affiliates to join without paying its usual $200 registration fee.
The offer is specifically aimed at affiliates who already have potential victims prepared for attacks, suggesting the group is looking to accelerate its operations.
Vexy previously advertised ransomware tools targeting Windows, Linux, and VMware ESXi, along with a 90% revenue share for affiliates.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
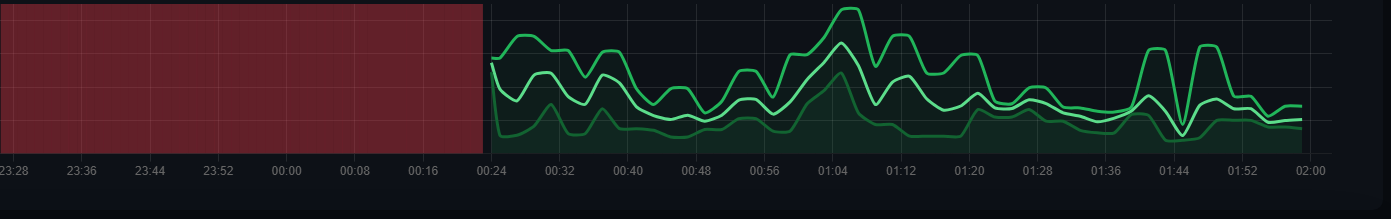
One of my servers' DNS just flat out stopped. Feeds were down for a little over an hour, but recovered. Unsure if it was provider related as I did not intervene.
No claims on any of the feeds were missed, as I have measures in place to catch up when this happens.
11:06pm UTC to 12:23am UTC 🫡
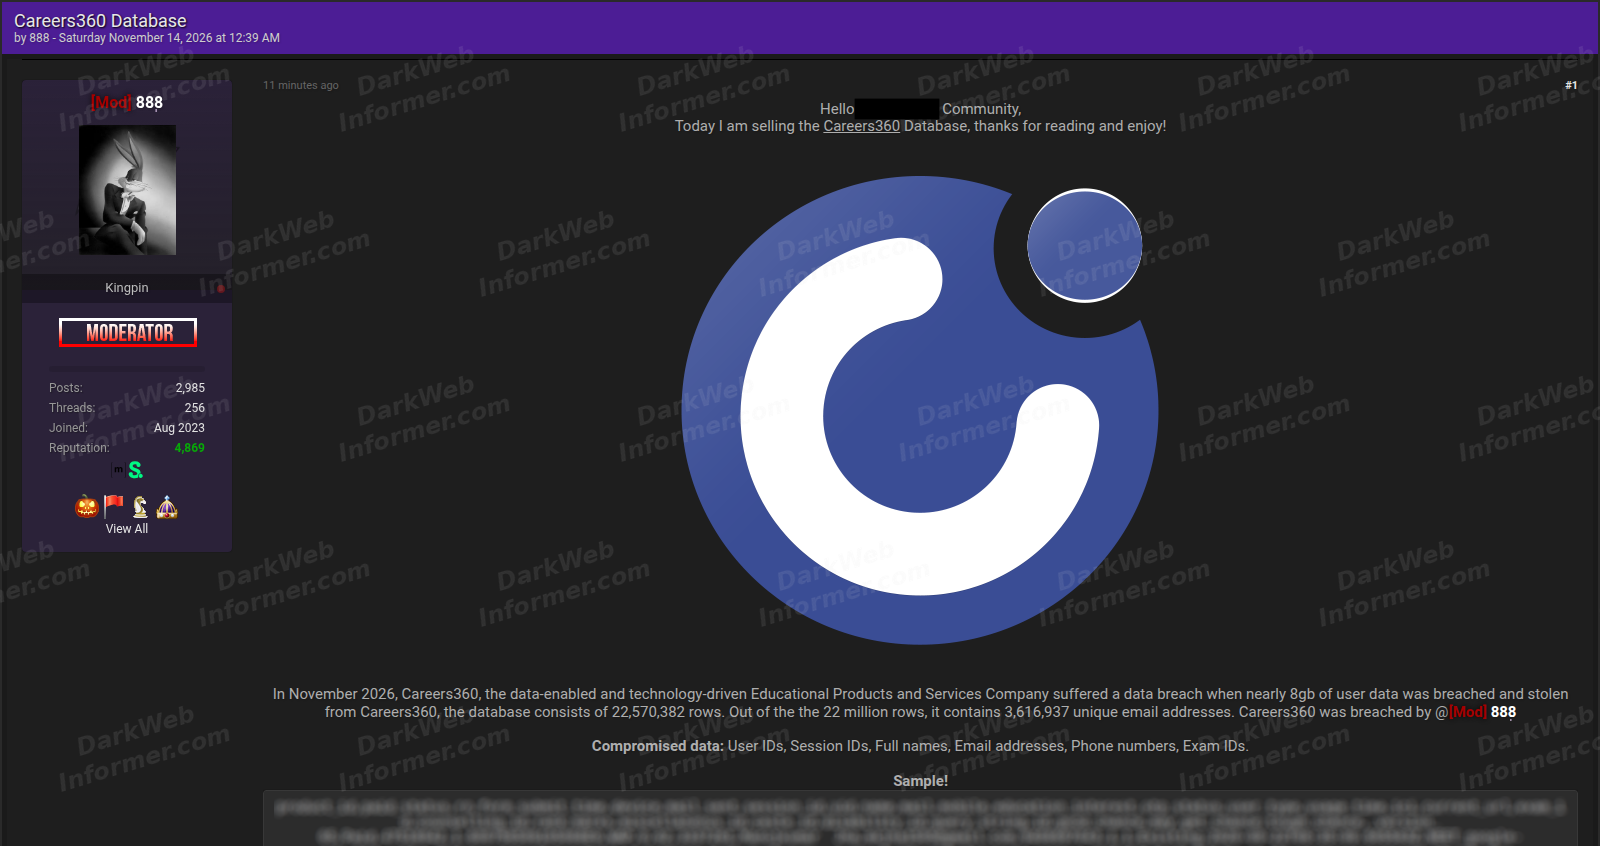
🚨🇮🇳 Careers360 allegedly breached, over 22.5 million records offered for sale
An actor known as "888" claims to have compromised Careers360, an Indian education and career guidance platform, stealing approximately 8 GB of user data.
The dataset reportedly contains 22,570,382 records, including 3.6 million unique email addresses, full names, phone numbers, user and session IDs, examination details, and student counseling information.
The actor has published 1,000 sample records and is accepting offers XMR.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
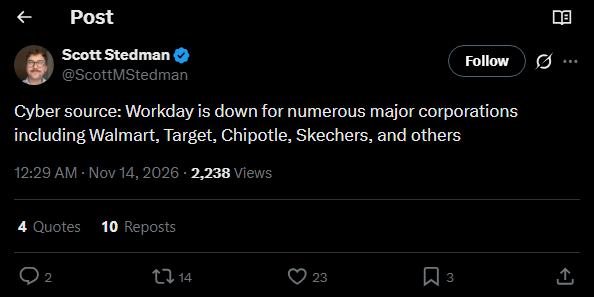
Seems Workday is down for many major companies. 👇
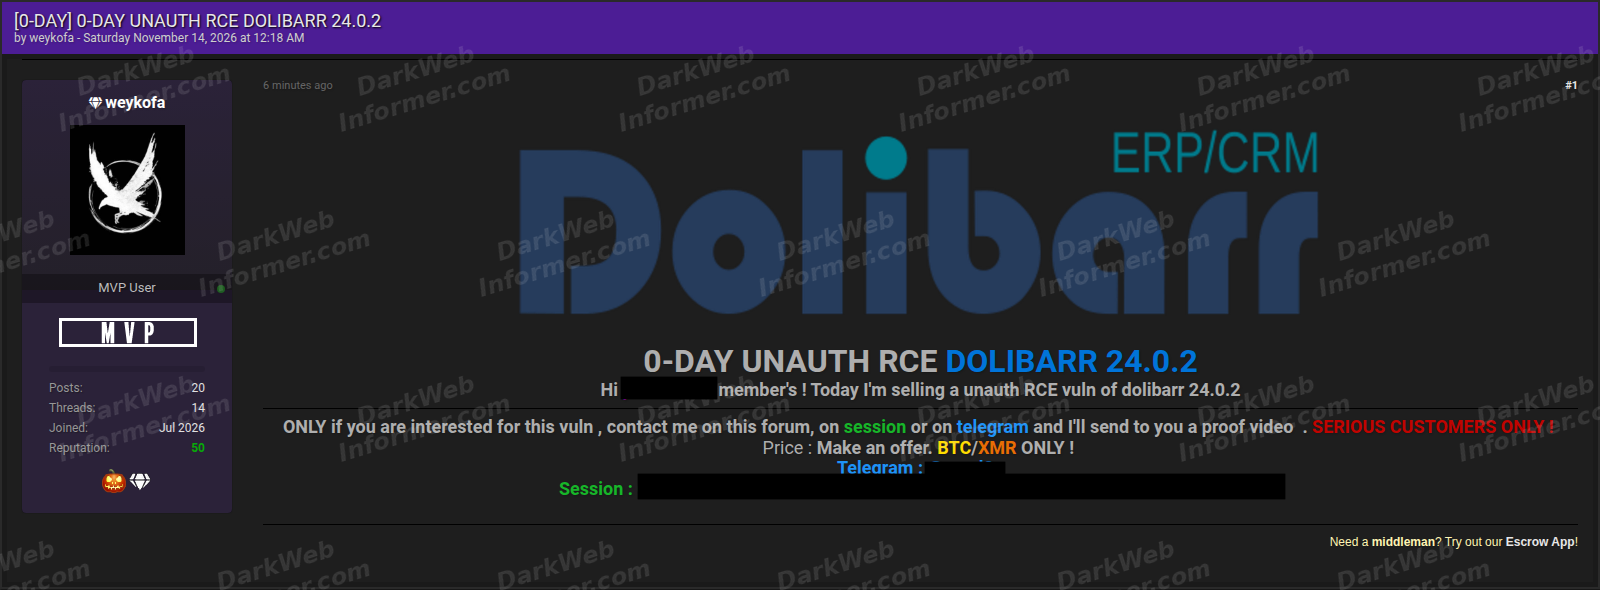
🚨 Zero-day exploit allegedly targeting Dolibarr 24.0.2 offered for sale
An actor known as "weykofa" is advertising an alleged zero-day vulnerability affecting Dolibarr ERP/CRM version 24.0.2, claiming it allows unauthenticated remote code execution (RCE).
The seller is accepting offers in Bitcoin (BTC) or Monero (XMR) and claims to have a proof-of-concept video available for prospective buyers.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
‼️ New Dark Web Informer Blog Post!
Title: INBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone Numbers
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Capiter Data Leak Claim Exposes 208,206 User Accounts and Phone Numbers
Link: https://darkwebinformer.com/capiter-data-leak-claim-exposes-208-206-user-accounts-and-phone-numbers/
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment Records
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Defy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ Emails
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure Dump
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: SENA Colombia Database Sale Claim Lists 20.56 Million Citizen Records With Identity, Contact and Employment Data
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Ma Deco de Fête Data Leak Claim Lists 45,156 Records With Customer and Payment Information
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Multiple ERP Access Claims Span 13 Organizations Across Nine Countries After Alleged 0-Day Exploitation
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Kensium Breach Claim Says 18 TB Exfiltrated, With 170 GB of Source Code and Database Backups Released
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Colorbox Data Leak Claim Lists 7.67 Million Rows With Customer, Shipping and Invoice Data
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Adems14 Data Leak Claim Lists 100,826 Records Covering 36,628 People and Property Service Data
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Lithos DEX Database Sale Claim Lists 173,146 Wallet Addresses and 50,239 IP Addresses
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: Geofixe Data Leak Claim Lists 1,656 Records With Customer, Billing and Payment Information
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: HomeMaison Data Sale Claim Lists 36.4 Million Records, 1.6M Emails and 330K Plaintext Passwords
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
‼️ New Dark Web Informer Blog Post!
Title: ARTE.TV Data Leak Claim Lists 673,760 Records With 604,083 Email Addresses
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
Dr.Gloves: 4chans Darkest Unsolved Mystery
⚠️ WARNING: This video covers disturbing subject matter that some viewers may find distressing. Viewer discretion is advised.
Video Credit: youtube.com/@Voidthewarlock

How I will explain it to my kids one day.
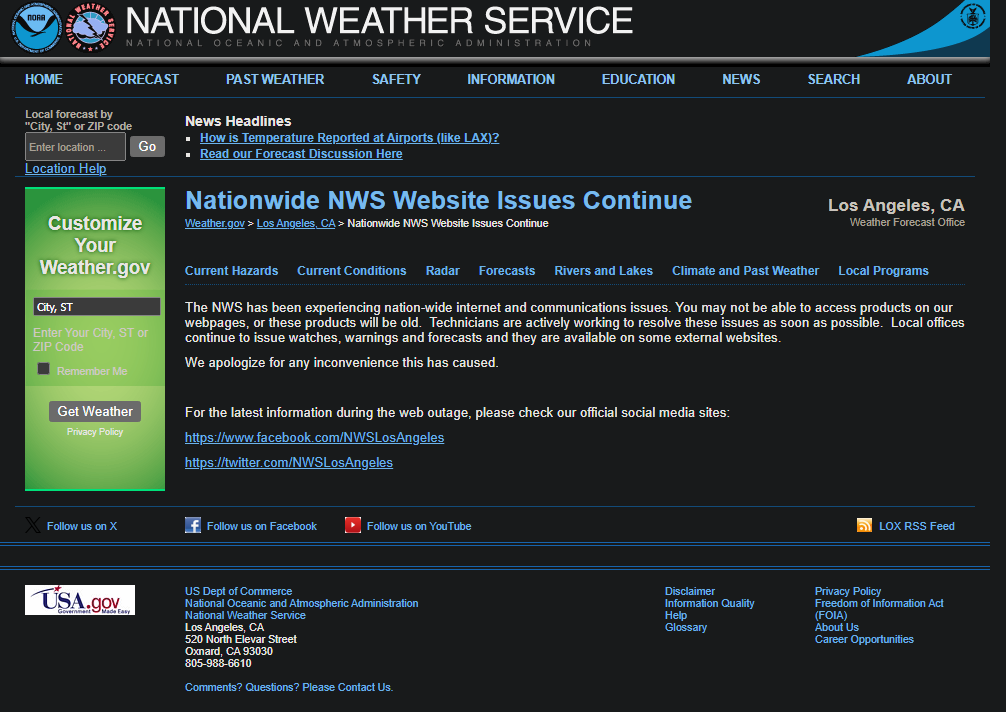
🚨🇺🇸 The National Weather Service (NWS) is currently experiencing technical issues.
🚨🇺🇸 The FAA’s nationwide ground stop advisory orders all departing flights to remain grounded “until further notice,” citing extraordinary circumstances and safety concerns.
Inbound international flights will be handled case by case. The advisory does not provide a confirmed time for departures to resume.
🚨🇺🇸 University of Texas at Arlington confirms hackers stole personal information as Qilin ransomware claims responsibility
The University of Texas at Arlington has confirmed that hackers stole personal information belonging to students and employees during a cyberattack in October.
The university says its investigation is ongoing to determine what information was stolen and who was affected. Its MachForms online portal remains offline following the incident.
The Qilin ransomware group claimed responsibility for the attack this week, although the university has not confirmed the group's involvement. The school serves more than 41,000 students.
Source: https://therecord.media/university-of-texas-arlington-warns-data-breach
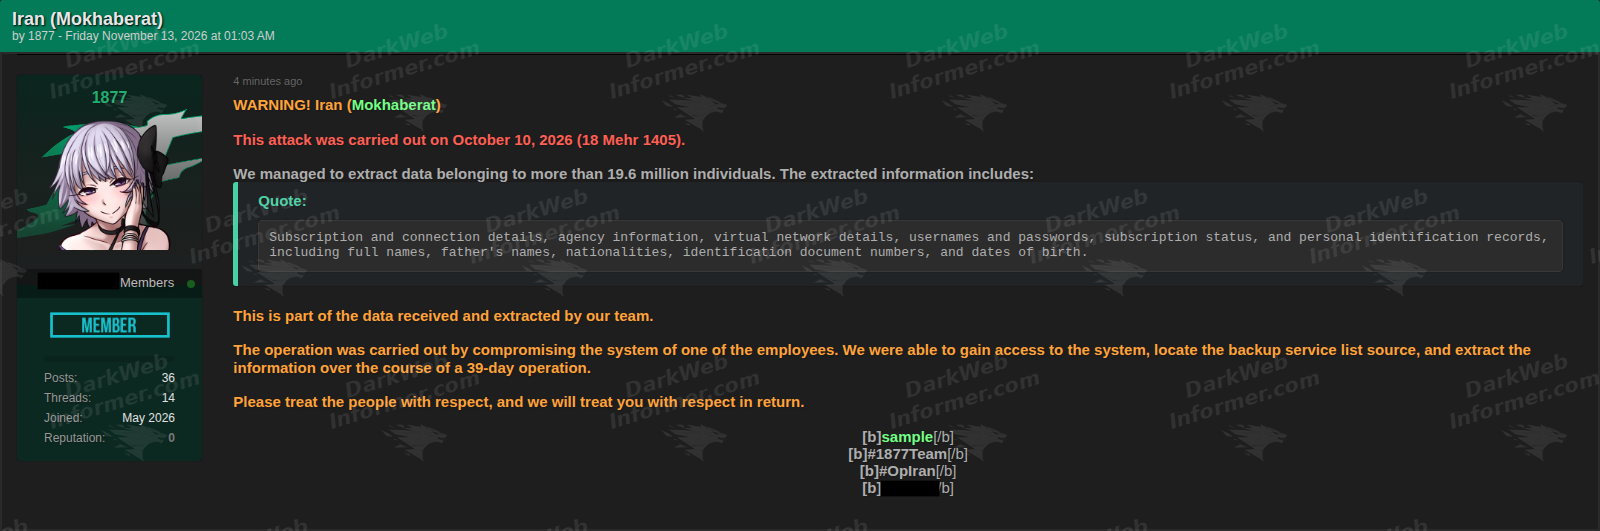
🚨🇮🇷 Iran's Mokhaberat telecommunications data allegedly breached, over 19.6 million individuals affected
A group known as "1877" claims to have compromised an employee account and extracted sensitive information from Iran's telecommunications infrastructure during a 39-day operation.
The allegedly stolen data includes:
• Full names, nationalities, and dates of birth • National identification numbers • Usernames and passwords • Subscriber and connection records • Agency and virtual network information
The group claims the attack occurred on October 10, 2026, and that access to backup services enabled the extraction of millions of records.
Claim is currently unverified.
💥 Enterprise-level intel, without the enterprise price tag. Plans for everyone. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
🚨🇺🇸 Uber confirms data breach exposing thousands of drivers' licenses after hackers compromise AI provider
Uber has confirmed that hackers stole personal information and driver's license details belonging to thousands of U.S. drivers following a cyberattack on third-party AI provider Fireworks AI.
The attackers reportedly stole internal credentials in October, allowing them to access Uber data stored with the provider.
Breach notifications confirm at least 7,870 affected individuals across Massachusetts, South Carolina, and Rhode Island, with additional victims reported in other states.
Fireworks AI attributed its breach to financially motivated cybercriminals targeting credentials used to access AI models.
Uber has begun notifying affected drivers, but the total number of victims remains unknown.
🚨 Citrix patches 28 NetScaler security flaws, including a critical vulnerability affecting every default installation
Citrix has released urgent security updates addressing 28 vulnerabilities in NetScaler ADC and Gateway, including CVE-2026-120868 (CVSS 9.3), which affects all unpatched deployments without requiring any special configuration.
The flaw allows unauthenticated attackers to trigger memory corruption and potentially crash affected appliances. Another critical vulnerability, CVE-2026-107412 (CVSS 9.5), affects systems configured as VPN gateways or authentication servers.
Affected versions include NetScaler 13.1 and 14.1, with security fixes now available. Citrix is urging administrators to patch immediately, particularly internet-facing deployments.
Source: https://support.citrix.com/external/article/CTX697305
🚨 Hackers hijack Microsoft SQL Servers to deploy Gh0st RAT and cryptocurrency miners
Fortinet researchers have uncovered an active campaign targeting internet-facing Microsoft SQL Servers, using brute-force attacks against weak credentials to gain access and deploy malware.
Once inside, attackers abuse legitimate T-SQL commands to execute malicious code, install Monero cryptocurrency miners, and deploy Gh0st RAT, a remote access trojan capable of stealing files, recording keystrokes, and remotely controlling compromised systems.
The campaign also uses scheduled tasks disguised as Microsoft Edge updates to maintain persistence. Researchers recommend restricting public access to SQL Servers, strengthening authentication, and disabling unnecessary command execution features.
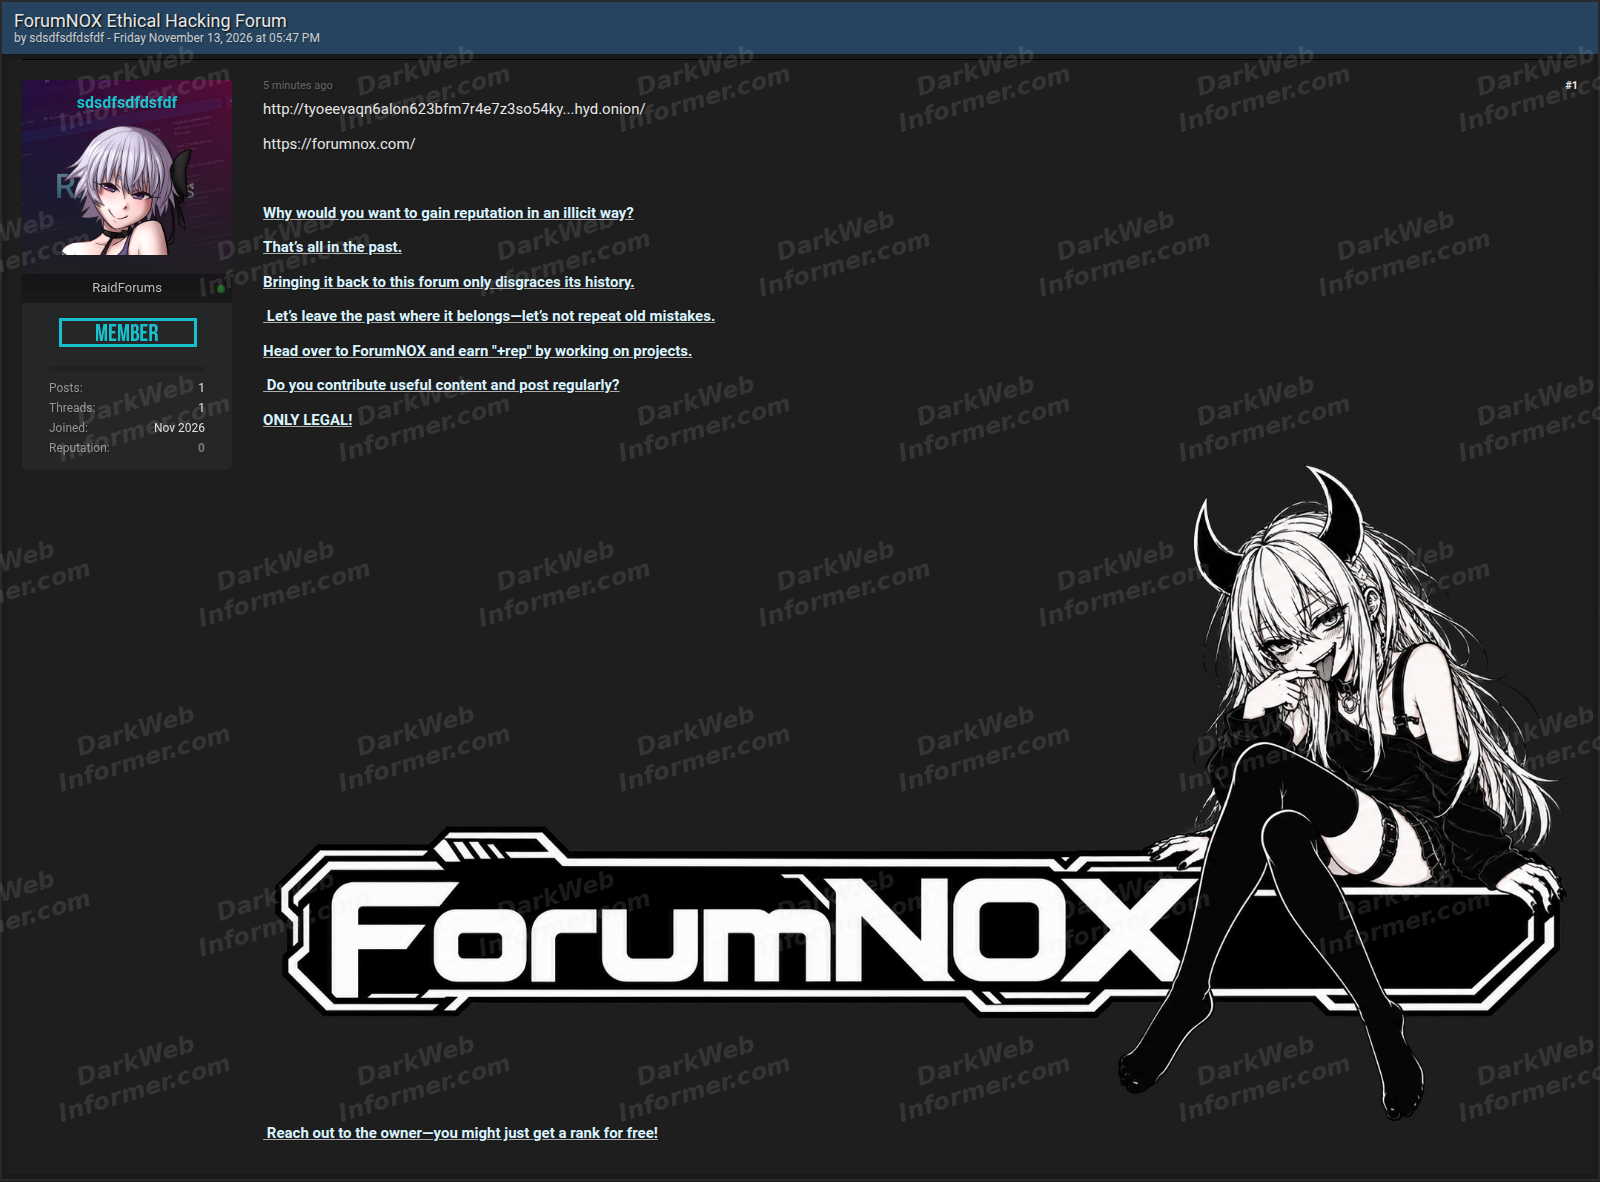
New "ethical hacking" forum: ForumNOX
Clearnet: forumnox[.]com
Dark Web: http://tyoeevaqn6alon623bfm7r4e7z3so54ky6uvbqkza3fyun7g4cm24hyd[.]onion
🚨 Hackers exploit Check Point zero-day to gain root access, deploy backdoors, and wipe VMware servers
PoC: https://github.com/googlesky/CVE-2026-123039
Check Point has confirmed active exploitation of CVE-2026-123039, a privilege escalation vulnerability that attackers chained with PHP2Shell to gain root access to vulnerable Security Gateways.
The attacks began October 30, initially targeting Israeli organizations before expanding worldwide. Hackers deployed persistent backdoors, stole configurations, and moved laterally into VMware ESXi infrastructure, where destructive wiper malware was used.
Check Point confirmed approximately two dozen unpatched systems were compromised.
Security fixes were available before the attacks, and administrators are urged to install the latest Jumbo Hotfix immediately.
Source: https://research.checkpoint.com/2026/php2shell-exploitation-on-check-point-gateway/
No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
🚨🇫🇷 Grand Est Automobiles customer and dealership data allegedly leaked
An actor known as "Alduin" claims to have leaked approximately 2,500 records from Grand Est Automobiles, a French automotive dealership group operating primarily in the Alsace region.
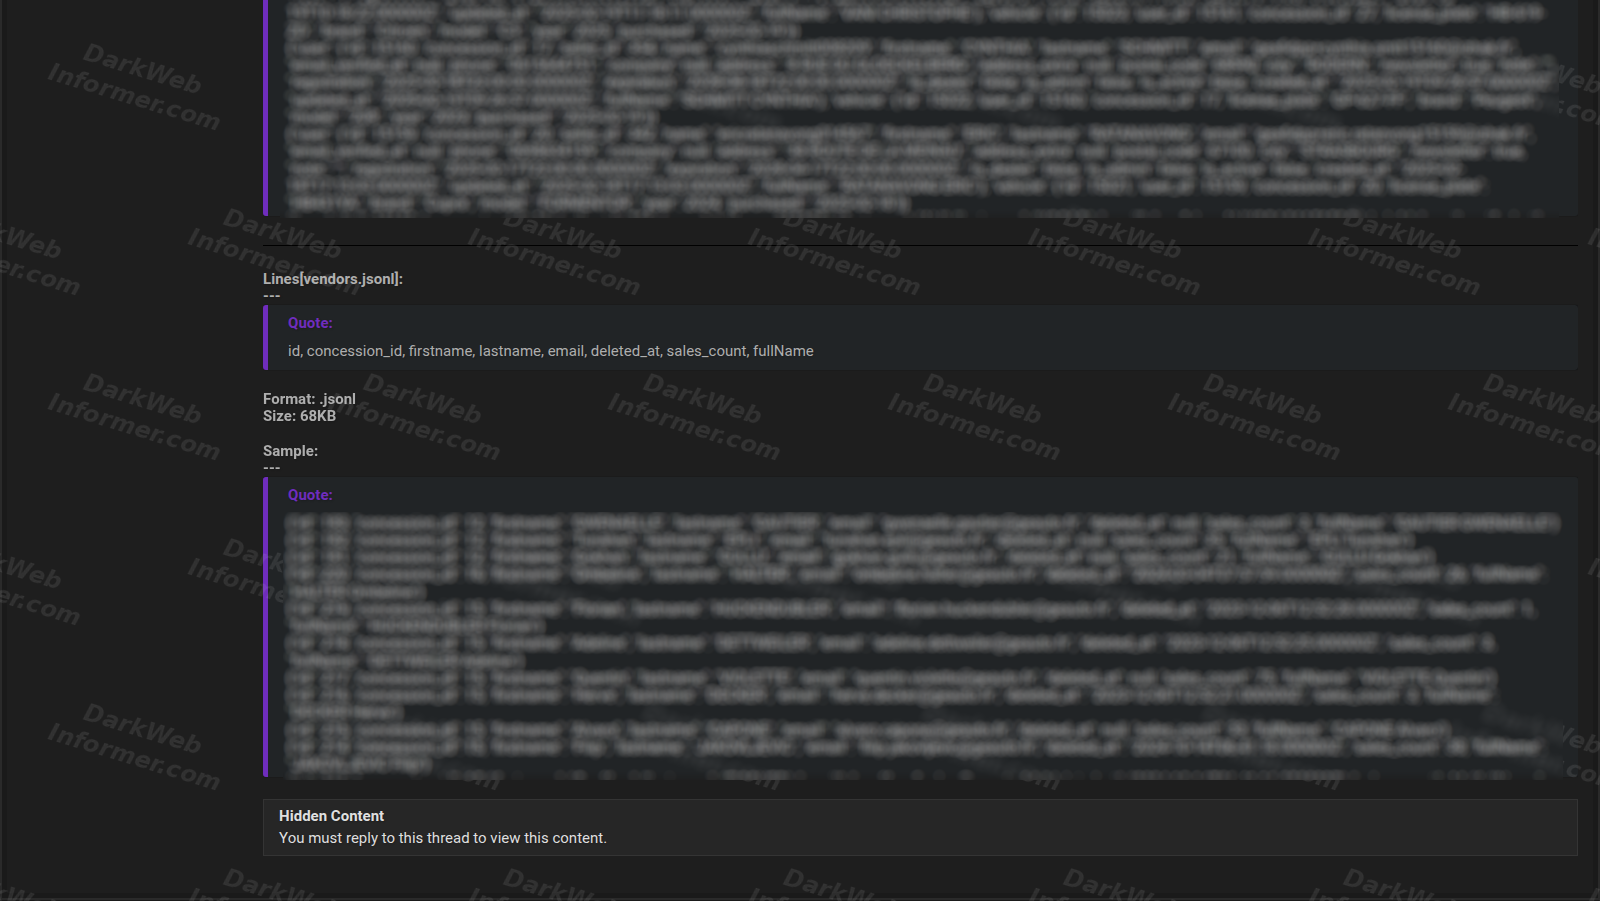
The exposed databases reportedly contain:
• Customer names, emails, and phone numbers • Residential addresses and postal codes • Vehicle registration plates, brands, and models • Vehicle purchase information • Dealership employee records and sales figures
Samples of the customer and vendor databases have been published, with the full files advertised for download.
Claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee
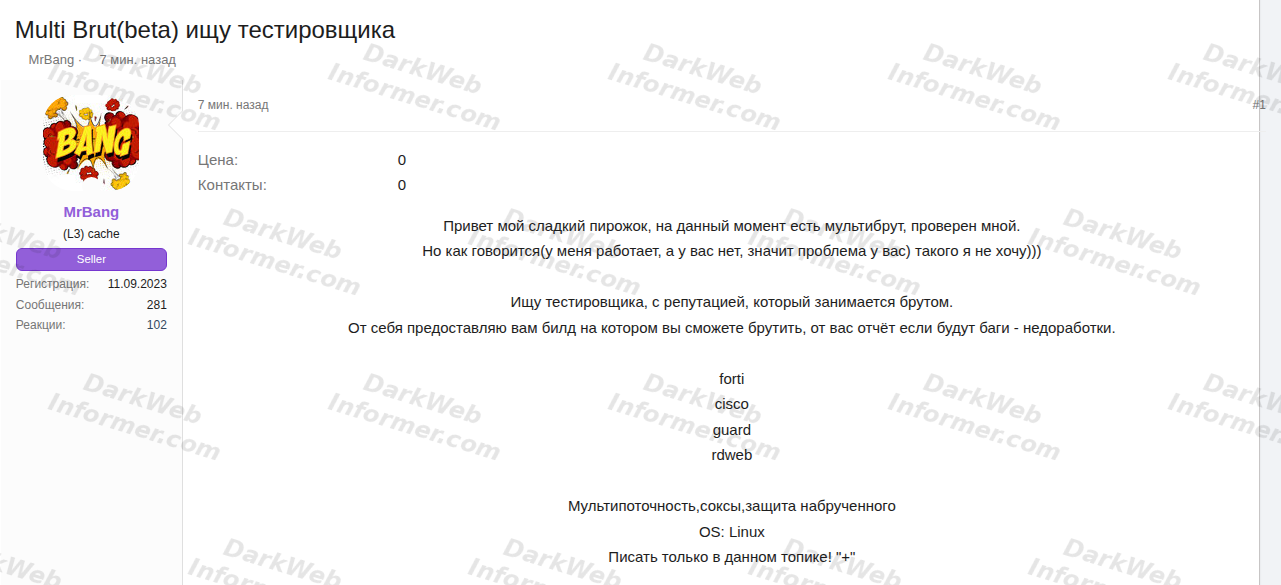
🚨 Multi Brut beta advertised, targeting Fortinet, Cisco, and RDWeb systems
An actor known as "MrBang" is recruiting testers for Multi Brut, a Linux-based brute-force tool currently in beta development.
The tool reportedly supports:
• Fortinet and Cisco targets • RDWeb authentication • Multithreaded operations • SOCKS proxy support • Protection of obtained credentials
The developer is offering test builds to experienced users in exchange for bug reports and feedback before a wider release.
The tool's capabilities have not been independently verified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Need API access? darkwebinformer.com/api-details
Check out the Telegram channel: t.me/SliceForLifeee